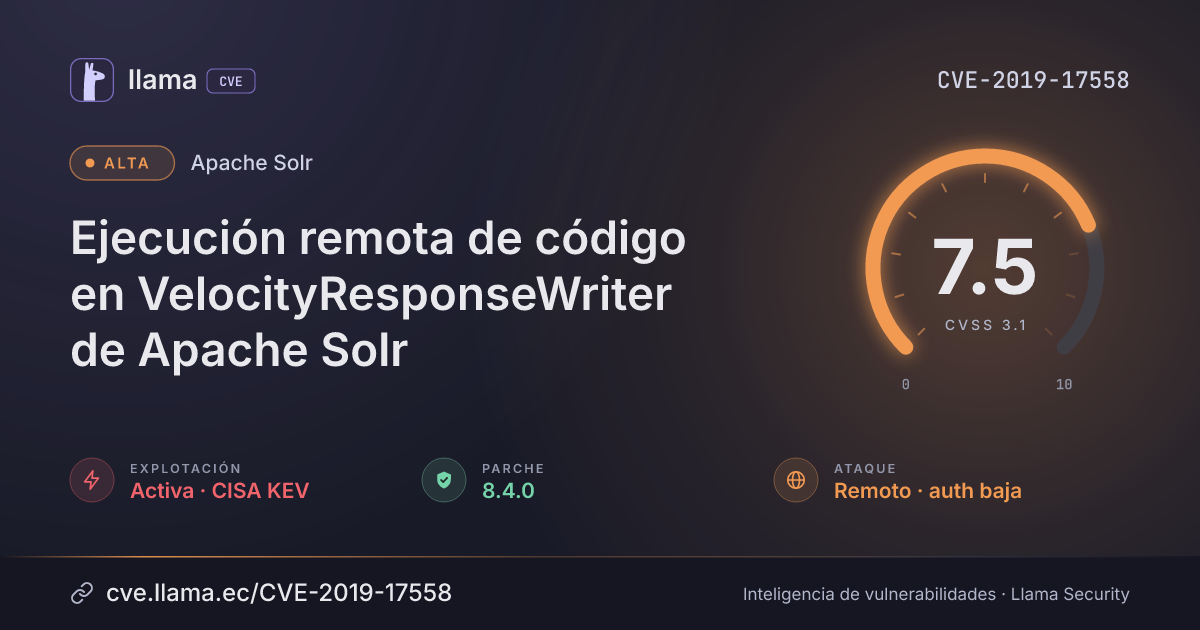
CVE-2019-17558
Apache Solr remote code execution in VelocityResponseWriter
An attacker who can supply malicious Velocity templates could run arbitrary code on the server.
CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H
Fuente: NVD
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 8.4.0 | org.apache.solr:solr-core · -2 d desde divulgación | |
| Divulgación | Publicada | CVE-2019-17558 divulgada · CVSS 7.5 (NVD) | |
| Explotación | CISA KEV | Agregada al catálogo de vulnerabilidades explotadas | |
| Remediación | Plazo KEV | Fecha límite de remediación para agencias federales (EE. UU.) | |
| Divulgación | Modificada | Última actualización del registro | |
| Explotación | Umbral EPSS | La probabilidad de explotación supera el 10 % | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Apache Solr, an open-source enterprise search platform, is affected in versions from 5.0.0 through 8.3.1, where its VelocityResponseWriter can be abused to run arbitrary code on the server. An attacker who can supply or modify malicious Velocity templates, such as through a user-defined configset or, when explicitly enabled, through request parameters, could gain remote code execution on the affected system.
Affects Apache Solr 5.0.0 through 8.3.1, where the VelocityResponseWriter allows remote code execution through custom Velocity templates. The facts name no fixed version or patch.
Descripción original del registro
Apache Solr 5.0.0 to Apache Solr 8.3.1 are vulnerable to a Remote Code Execution through the VelocityResponseWriter. A Velocity template can be provided through Velocity templates in a configset `velocity/` directory or as a parameter. A user defined configset could contain renderable, potentially malicious, templates. Parameter provided templates are disabled by default, but can be enabled by setting `params.resource.loader.enabled` by defining a response writer with that setting set to `true`. Defining a response writer requires configuration API access. Solr 8.4 removed the params resource loader entirely, and only enables the configset-provided template rendering when the configset is `trusted` (has been uploaded by an authenticated user).
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
mavenorg.apache.solr:solr-core |
Corregida | 8.4.0 | -2 d | 10.1.0 no afectada |
8.4.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://lists.apache.org/thread.html/rb964fe5c4e3fc05f75e8f74bf6b885f456b7a7750c36e9a8045c627a%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r9271d030452170ba6160c022757e1b5af8a4c9ccf9e04164dec02e7f%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/ra29fa6ede5184385bf2c63e8ec054990a7d4622bba1d244bee70d82d%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r36e35fd76239a381643555966fb3e72139e018d52d76544fb42f96d8%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r5074d814d3a8c75df4b20e66bfd268ee0a73ddea7e85070cec3ae78d%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/rf6d7ffae2b940114324e036b6394beadf27696d051ae0c4a5edf07af%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r58c58fe51c87bc30ee13bb8b4c83587f023edb349018705208e65b37%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r25f1bd4545617f5b86dde27b4c30fec73117af65598a30e20209739a%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r12ab2cb15a34e49b4fecb5b2bdd7e10f3e8b7bf1f4f47fcde34d3a7c%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r99c3f7ec3a079e2abbd540ecdb55a0e2a0f349ca7084273a12e87aeb%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r0b7b9d4113e6ec1ae1d3d0898c645f758511107ea44f0f3a1210c5d5%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r339865b276614661770c909be1dd7e862232e3ef0af98bfd85686b51%40%3Cdev.lucene.apache.org%3EVer 13 referencias más
https://lists.apache.org/thread.html/r19d23e8640236a3058b4d6c23e5cd663fde182255f5a9d63e0606a66%40%3Cdev.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/rafc939fdd753f55707841cd5886fc7fcad4d8d8ba0c72429b3220a9a%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/rde3dbd8e646dabf8bef1b097e9a13ee0ecbdb8441aaed6092726c98d%40%3Cissues.ambari.apache.org%3Ehttps://lists.apache.org/thread.html/r204ba2a9ea750f38d789d2bb429cc0925ad6133deea7cbc3001d96b5%40%3Csolr-user.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/rf5230a049d989dbfdd404b4320a265dceeeba459a4d04ec21873bd55%40%3Csolr-user.lucene.apache.org%3Ehttps://issues.apache.org/jira/browse/SOLR-13971https://lists.apache.org/thread.html/rc400db37710ee79378b6c52de3640493ff538c2beb41cefdbbdf2ab8%40%3Ccommits.submarine.apache.org%3Ehttps://lists.apache.org/thread.html/r79c7e75f90e735fd32c4e3e97340625aab66c09dfe8c4dc0ab768b69%40%3Csolr-user.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/re8d12db916b5582a23ed144b9c5abd0bea0be1649231aa880f6cbfff%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r8a36e4f92f4449dec517e560e1b55639f31b3aca26c37bbad45e31de%40%3Cissues.lucene.apache.org%3Ehttps://lists.apache.org/thread.html/r7b89b3dcfc1b6c52dd8d610b897ac98408245040c92b484fe97a51a2%40%3Csolr-user.lucene.apache.org%3Ehttp://packetstormsecurity.com/files/157078/Apache-Solr-8.3.0-Velocity-Template-Remote-Code-Execution.htmlhttps://www.oracle.com/security-alerts/cpuoct2020.htmlLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.