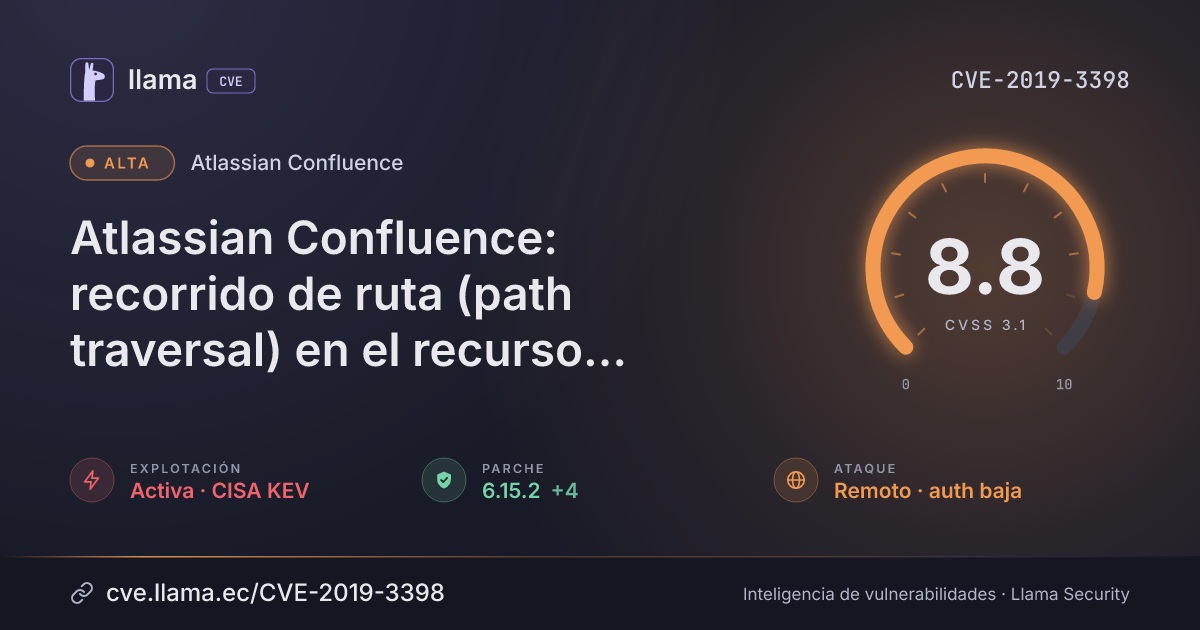
CVE-2019-3398
Atlassian Confluence path traversal in downloadallattachments resource
A remote attacker with some permissions can write files to any location on the server, potentially running code.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H
Fuente: NVD
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2019-3398 divulgada · CVSS 8.8 (NVD) | |
| Explotación | CISA KEV | Agregada al catálogo de vulnerabilidades explotadas | |
| Remediación | Plazo KEV | Fecha límite de remediación para agencias federales (EE. UU.) | |
| Divulgación | Modificada | Última actualización del registro | |
| Explotación | Umbral EPSS | La probabilidad de explotación supera el 10 % | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Confluence Server and Data Center are affected, where a remote attacker with certain permissions, such as the ability to add attachments or administrative rights to a space, could write files to arbitrary locations on the server. This could lead to remote code execution, giving the attacker control over the affected system.
Affects Confluence Server and Data Center across several version ranges starting at 2.0.0. Fixed in 6.15.2, with branch fixes 6.6.13, 6.12.4, 6.13.4 and 6.14.3.
Descripción original del registro
Confluence Server and Data Center had a path traversal vulnerability in the downloadallattachments resource. A remote attacker who has permission to add attachments to pages and / or blogs or to create a new space or a personal space or who has 'Admin' permissions for a space can exploit this path traversal vulnerability to write files to arbitrary locations which can lead to remote code execution on systems that run a vulnerable version of Confluence Server or Data Center. All versions of Confluence Server from 2.0.0 before 6.6.13 (the fixed version for 6.6.x), from 6.7.0 before 6.12.4 (the fixed version for 6.12.x), from 6.13.0 before 6.13.4 (the fixed version for 6.13.x), from 6.14.0 before 6.14.3 (the fixed version for 6.14.x), and from 6.15.0 before 6.15.2 are affected by this vulnerability.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Confluence |
Corregida | 6.6.13, 6.12.4, 6.13.4, 6.14.3, 6.15.2 | — | — |
6.6.136.12.46.13.46.14.36.15.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://jira.atlassian.com/browse/CONFSERVER-58102https://seclists.org/bugtraq/2019/Apr/33http://packetstormsecurity.com/files/152616/Confluence-Server-Data-Center-Path-Traversal.htmlhttp://packetstormsecurity.com/files/155235/Atlassian-Confluence-6.15.1-Directory-Traversal.htmlhttp://packetstormsecurity.com/files/155245/Atlassian-Confluence-6.15.1-Directory-Traversal.htmlhttp://www.securityfocus.com/bid/108067Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.