llamaCVEVulnerability Intelligence
/
Atlassian Bitbucket Server

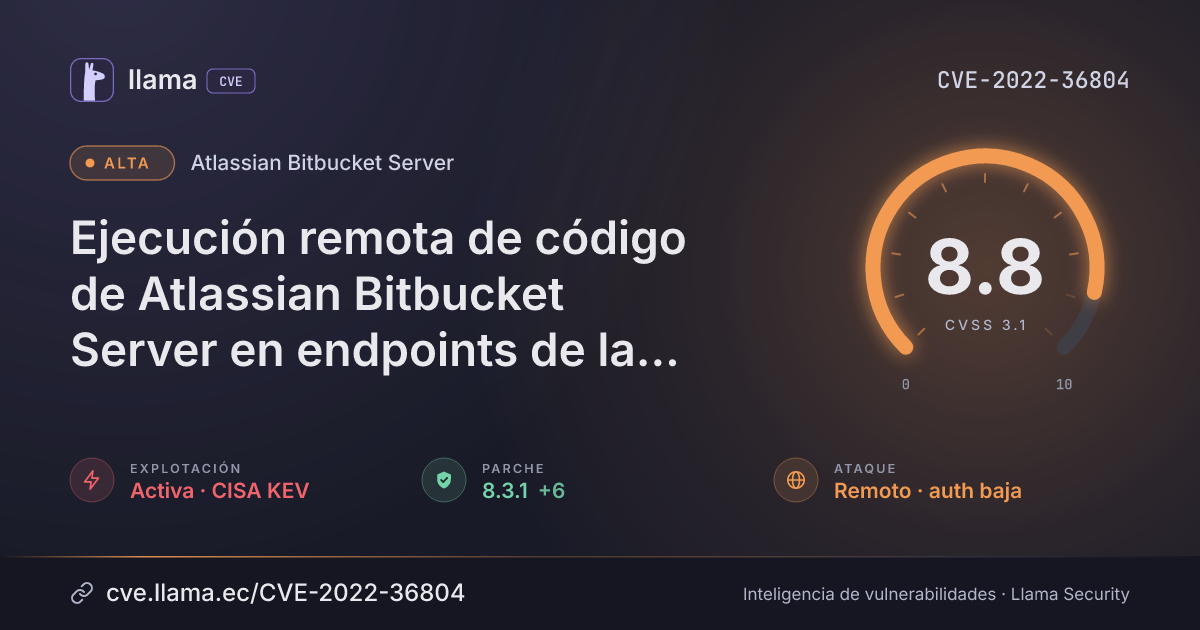
CVE-2022-36804

Atlassian Bitbucket Server remote code execution in API endpoints

An attacker with repository read access can run arbitrary code on the server via crafted HTTP requests.

Texto original en inglés · Ver en español

CISA KEV · explotación activaCrítica · en CISA KEV, EPSS ≥ 10 %Parche disponible
Descargar PNG JSON
CVSS 3.1
8.8
Alta
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H Fuente: NVD
ExplotaciónActivaEn CISA KEV desde 30 sept 2022
Exploits públicos0Explotada, pero sin código público enlazado
Parche7 versiones7.6.17 · 7.17.10 · 7.21.4 · 8.0.3 …
Exposición1.549 dDesde la divulgación, 25 ago 2022, 12:40 a. m.
EPSS ≥ 10 %22 oct 2026Fecha en que la probabilidad de explotación superó el umbral
Decisión estimadaAtender
Priorizar en el próximo ciclo de cambios
Estimación de Llama con el árbol SSVC de CISA a partir de vector CVSS 3.1 y la evidencia de explotación (sin evaluación oficial): explotación activa (CISA KEV), no automatizable e impacto técnico total. Plazo KEV: 21 oct 2022.
CVSS alto, corazón bajito. Priorízala.Yo que tú, revisaba los logs de anoche.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Modificada
Explotación
CISA KEV
Umbral EPSS
Remediación
Plazo KEV
Monitoreo
Detectada
Verificada
25 ago 22
30 sept 22
21 oct 22
21 oct 25
22 oct 26
17 nov 26
21 nov 26
25 ago 22
16 sept 23
7 oct 24
30 oct 25
21 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2022-36804 divulgada · CVSS 8.8 (NVD)
Explotación CISA KEV Agregada al catálogo de vulnerabilidades explotadas
Remediación Plazo KEV Fecha límite de remediación para agencias federales (EE. UU.)
Divulgación Modificada Última actualización del registro
Explotación Umbral EPSS La probabilidad de explotación supera el 10 %
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 16 nov 2026

Atlassian Bitbucket Server and Data Center have a flaw in several API endpoints that lets an attacker run arbitrary code on the Bitbucket instance through command injection with a malicious HTTP request. The attacker can send it remotely over the network with only read access to a repository, and this bug is being exploited in attacks.

Affects Atlassian Bitbucket Server and Data Center 7.0.0 through 8.3.0, where someone with read access to a repository (public ones included) can send a crafted request. Fixed in 7.6.17, 7.17.10, 7.21.4, 8.0.3, 8.1.3, 8.2.2, 8.3.1.

¿Qué significa?Several API endpoints in Bitbucket pass request data into commands without safe handling (command injection). A malicious HTTP request can make the Bitbucket instance run arbitrary code.
¿Quién está afectado?All Bitbucket Server and Data Center versions from 7.0.0 to 8.3.0 inclusive are covered. The attacker needs access to a public repository or read permission on a private one. The installed version appears in the Bitbucket administration area or the About page.
¿Qué hacer?Upgrade to a fixed version for the release line in use: 7.6.17, 7.17.10, 7.21.4, 8.0.3, 8.1.3, 8.2.2, or 8.3.1. The advisory lists no workaround.
Descripción original del registro

Multiple API endpoints in Atlassian Bitbucket Server and Data Center 7.0.0 before version 7.6.17, from version 7.7.0 before version 7.17.10, from version 7.18.0 before version 7.21.4, from version 8.0.0 before version 8.0.3, from version 8.1.0 before version 8.1.3, and from version 8.2.0 before version 8.2.2, and from version 8.3.0 before 8.3.1 allows remote attackers with read permissions to a public or private Bitbucket repository to execute arbitrary code by sending a malicious HTTP request. This vulnerability was reported via our Bug Bounty Program by TheGrandPew.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Bitbucket Server or Data Center version between 7.0.0 and 8.3.0 inclusive“All Bitbucket Server and Data Center versions from 7.0.0 to 8.3.0 inclusive.”
02
Attacker can reach a public repository, or has read permission on a private one“An attacker with access to a public Bitbucket repository or with read permissions to a private one can execute arbitrary code by sending a malicious HTTP request.”
¿Quién debe revisar?Teams running Atlassian Bitbucket Server or Data Center 7.0.0 to 8.3.0, including any Bitbucket Mesh nodes, which must be updated to a Mesh version containing the fix.
No protegeUpgrading Bitbucket alone is not enough if Mesh nodes are configured; they must be updated too.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · NVD
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:L
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:H
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 8.3 (muy fácil) · +1.7 por explotación activa.
Versiones

Rangos afectados

Afectada Corregida
Bitbucket Server · Bitbucket Data Center≥ unspecified < 7.6.17
Bitbucket Server · Bitbucket Data Center≥ unspecified < 7.17.10
Bitbucket Server · Bitbucket Data Center≥ unspecified < 7.21.4
Bitbucket Server · Bitbucket Data Center≥ unspecified < 8.0.3
Bitbucket Server · Bitbucket Data Center≥ unspecified < 8.1.3
Bitbucket Server · Bitbucket Data Center≥ unspecified < 8.2.2
Bitbucket Server · Bitbucket Data Center≥ unspecified < 8.3.1
Bitbucket Server · Bitbucket Data Center≥ 7.0.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 7.7.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 7.18.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 8.0.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 8.1.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 8.2.0 < unspecified
Bitbucket Server · Bitbucket Data Center≥ 8.3.0 < unspecified
unspecified
7.6.17
7.7.0
7.17.10
7.18.0
7.21.4
8.0.0
8.0.3
8.1.0
8.1.3
8.2.0
8.2.2
8.3.0
8.3.1
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
Bitbucket Server
Corregida 7.6.17, 7.17.10, 7.21.4, 8.0.3, 8.1.3, 8.2.2, 8.3.1 — —
Versiones corregidas7.6.177.17.107.21.48.0.38.1.38.2.28.3.1
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://jira.atlassian.com/browse/BSERV-13438
Exploithttp://packetstormsecurity.com/files/168470/Bitbucket-Git-Command-Injection.html
Exploithttp://packetstormsecurity.com/files/171453/Bitbucket-7.0.0-Remote-Command-Execution.html

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.