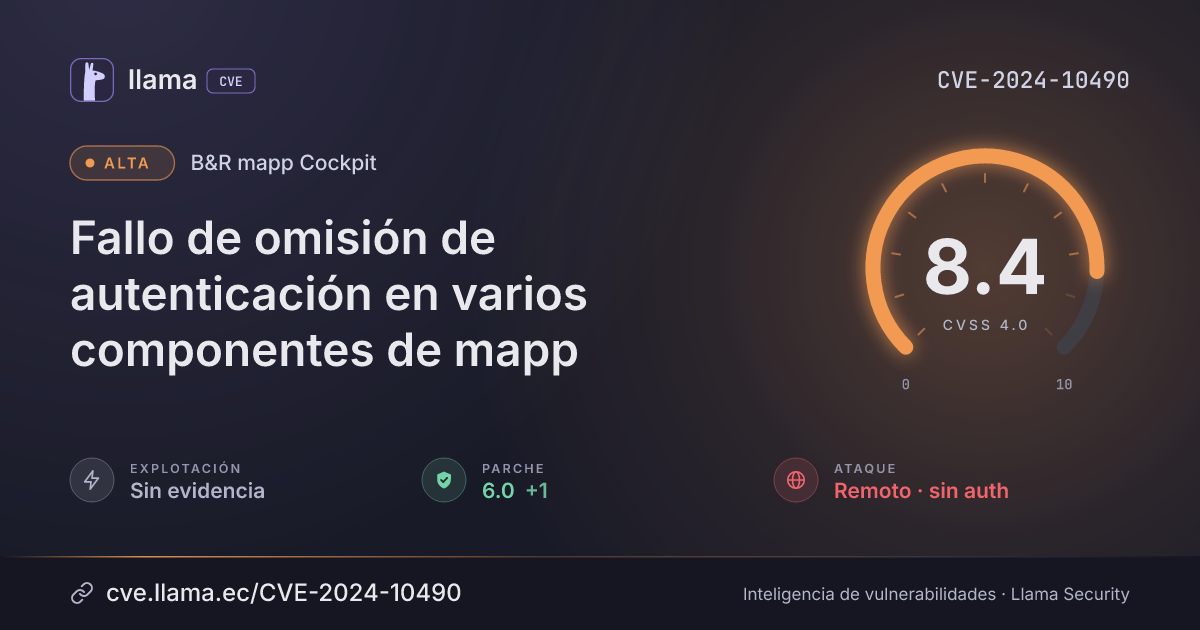
ExplotaciónSin evidenciaSSVC: ninguna · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche2 versiones6.0;0 · 6.0
Exposición718 dDesde la divulgación, 2 dic 2024, 3:46 a. m.
Detección714 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir
Remediar en la ventana regular de mantenimiento
Sin explotación conocida, no automatizable e impacto técnico parcial. Hay versiones corregidas disponibles.
Timeline
Ciclo de vida de la vulnerabilidad
Hoy
Divulgación
Publicada +2
Explotación
Remediación
Monitoreo
Detectada
2 dic 24
17 nov 26
21 nov 26
2 dic 24
31 may 25
26 nov 25
25 may 26
21 nov 26
Fecha
Fase
Evento
Detalle
Divulgación
Publicada
CVE-2024-10490 divulgada · CVSS 8.4 (CNA)
Divulgación
Evaluación SSVC
CISA-ADP · explotación ninguna
Divulgación
Modificada
Última actualización del registro
Monitoreo
Detectada
Ingresó al índice
Resumen
An “Authentication Bypass Using an Alternate Path or Channel” vulnerability in the OPC UA Server configuration required for B&R mapp Cockpit before 6.0, B&R mapp View before 6.0, B&R mapp Services before 6.0, B&R mapp Motion before 6.0 and B&R mapp Vision before 6.0 may be used by an unauthenticated network-based attacker to cause information disclosure, unintended change of data, or denial of service conditions.
B&R mapp Services is only affected, when mpUserX or mpCodeBox are used in the Automation Studio project.
Vector CVSS 4.0
Desglose de métricas
Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:P
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:L
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
7.1/ 10Alto
Vector 7.1 (fácil) · sin evidencia de explotación.
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
Registro
EscenarioGENERALABB
MitigaciónEnforce client device authentication in the configuration of the OPC UA server. Configure a proper “SecurityPolicy” for OPC UA Server ( Automation Help https://help.br-automation.com/#/en/4/communication/opcua/runtime/opcua_config_security.html ) and select a “CertificateStore configuration” which has “Validate SSL communication partner” set to “on” ( Automation Help https://help.br-automation.com/#/en/4/access_and_security%2Fssl%2Fssl_configuration.html ).
Limit access to the OPC UA Server (default 4840/tcp) to IP addresses or IP subnets which are running instances of impacted mapp components and legitime OPC UA clients using the B&R Automation Runtime host-based firewall. Ensure only trusted personal is able to access devices with the specified IP (range) and enforce strict authentication on these devices.
Please be aware that B&R Automation Runtime and its services (like mapp components) are not intended to be directly connected to the internet at any time. Customers are advised to use the host-based firewall as well as an external control network firewall to limit access to each service running at B&R Automation Runtime. Additionally, consider granting access from the outside of the control network only to specific timeframes (e.g. for maintenance).
mapp View
For customers only using the OPC UA Server for their mapp View Visualization, block all incoming traffic to the OPC UA Server (default port 4840/tcp) using the B&R Automation Runtime host-based firewall. Blocking external traffic on the OPC UA Server has no impact on the functionality of mapp View.ABB
Usamos cookies propias estrictamente necesarias para que el sitio funcione y sea seguro. Con tu permiso, también usamos almacenamiento local para recordar tus preferencias y medir el uso del sitio de forma agregada. Puedes aceptar, rechazar o configurar cada categoría, y cambiar tu decisión cuando quieras desde el enlace “Preferencias de cookies” del pie de página. Más información
Preferencias de cookies
Elige qué permites
Solo usamos tecnologías propias de este dominio. Sin publicidad ni rastreadores de terceros. Detalle en la Política de cookies.