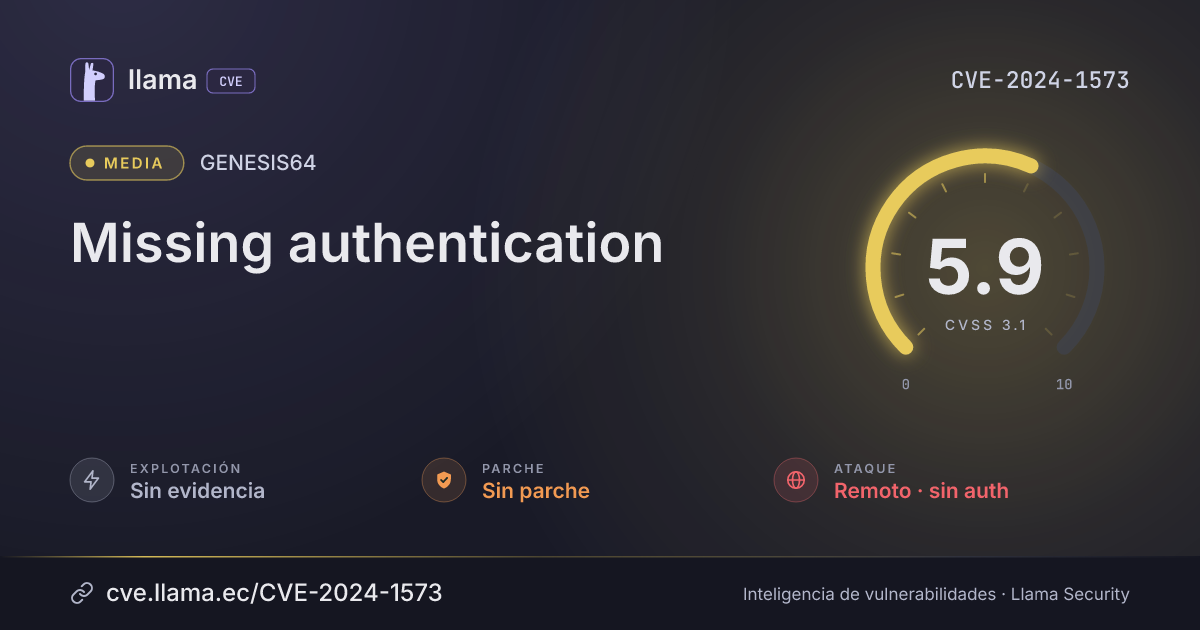
CVE-2024-1573
Missing authentication
CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:H/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2024-1573 divulgada · CVSS 5.9 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Missing Authentication for Critical Function vulnerability in the mobile monitoring feature of Mitsubishi Electric GENESIS64 versions 10.97.2 and prior, Mitsubishi Electric ICONICS Suite versions 10.97.2 and prior, Mitsubishi Electric Hyper Historian versions 10.97.2 and prior, Mitsubishi Electric AnalytiX versions 10.97.2 and prior, Mitsubishi Electric MobileHMI versions 10.97.2 and prior, Mitsubishi Electric IoTWorX version 10.95, Mitsubishi Electric MC Works64 all versions, Mitsubishi Electric Iconics Digital Solutions GENESIS64 versions 10.97.2 and prior, Mitsubishi Electric Iconics Digital Solutions ICONICS Suite versions 10.97.2 and prior, Mitsubishi Electric Iconics Digital Solutions Hyper Historian versions 10.97.2 and prior, Mitsubishi Electric Iconics Digital Solutions AnalytiX versions 10.97.2 and prior, Mitsubishi Electric Iconics Digital Solutions MobileHMI versions 10.97.2 and prior, and Mitsubishi Electric Iconics Digital Solutions IoTWorX version 10.95 allows a remote unauthenticated attacker to bypass proper authentication and log in to the system when all of the following conditions are met: (1) Active Directory is used in the security setting (2) "Automatic log in" option is enabled in the security setting (3) The IcoAnyGlass IIS Application Pool is running under an Active Directory Domain Account. (4) The IcoAnyGlass IIS Application Pool account is included in GENESIS64, ICONCIS Suite, and MC Works64 Security and has permission to log in.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
GENESIS64 |
Sin parche | — | — | — |
ICONICS Suite |
Sin parche | — | — | — |
Hyper Historian |
Sin parche | — | — | — |
AnalytiX |
Sin parche | — | — | — |
MobileHMI |
Sin parche | — | — | — |
IoTWorX |
Sin parche | — | — | — |
MC Works64 |
Sin parche | — | — | — |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://www.mitsubishielectric.com/psirt/vulnerability/pdf/2024-004_en.pdfhttps://www.mitsubishielectric.com/en/psirt/vulnerability/pdf/2024-004_en.pdfhttps://jvn.jp/vu/JVNVU98894016/https://www.cisa.gov/news-events/ics-advisories/icsa-24-184-03Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.