llamaCVEVulnerability Intelligence
/
deno

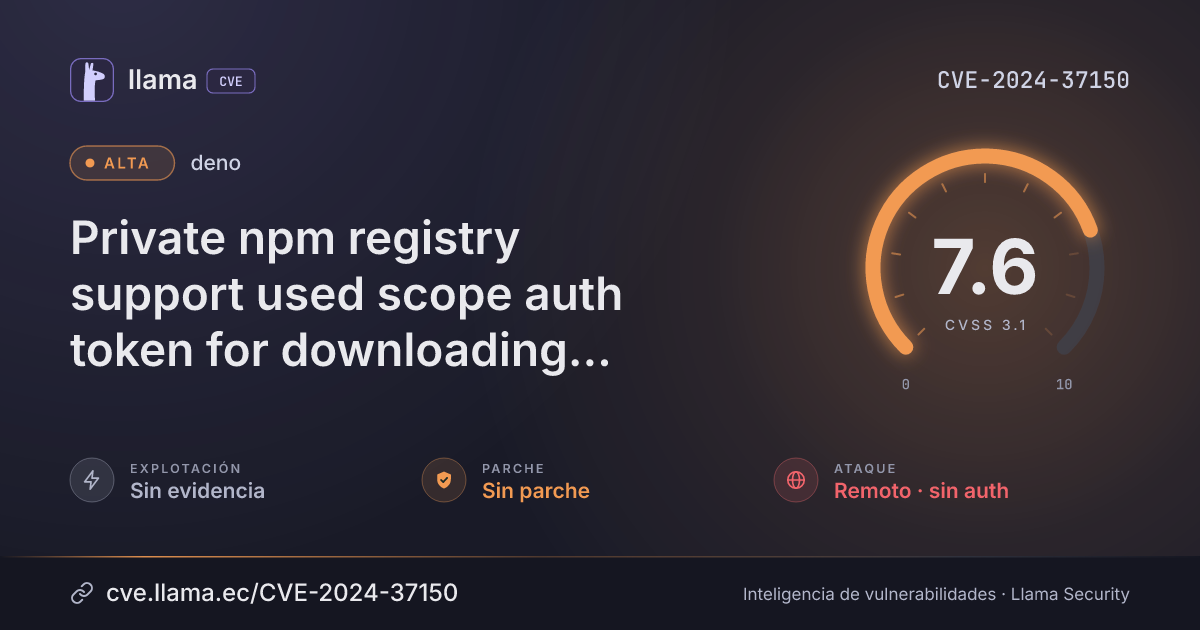
CVE-2024-37150

Private npm registry support used scope auth token for downloading tarballs

Specific setups onlySin parche publicado
Descargar PNG JSON
CVSS 3.1
7.6
Alta
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:L Fuente: CNA
6.5NVD · CVSS 3.1CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:N/A:N
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
ParcheSin parcheEl fabricante no ha publicado corrección
Exposición896 dDesde la divulgación, 6 jun 2024, 10:28 a. m.
Detección879 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir
Remediar en la ventana regular de mantenimiento
Sin explotación conocida, no automatizable e impacto técnico parcial. No hay versión corregida: aplique mitigaciones.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada +1
Modificada
Explotación
Remediación
Monitoreo
Detectada
Fuente: OSV +1
6 jun 24
2 ago 24
3 nov 26
18 nov 26
20 nov 26
6 jun 24
16 ene 25
28 ago 25
10 abr 26
20 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2024-37150 divulgada · CVSS 7.6 (CNA)
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: OSV Registro visto por primera vez en OSV
Monitoreo Verificada Última verificación contra las fuentes
Resumen

An issue in `.npmrc` support in Deno 1.44.0 was discovered where Deno would send `.npmrc` credentials for the scope to the tarball URL when the registry provided URLs for a tarball on a different domain. All users relying on .npmrc are potentially affected by this vulnerability if their private registry references tarball URLs at a different domain. This includes usage of deno install subcommand, auto-install for npm: specifiers and LSP usage. It is recommended to upgrade to Deno 1.44.1 and if your private registry ever serves tarballs at a different domain to rotate your registry credentials.

Only affects Deno 1.44.0 using .npmrc credentials for a private npm registry scope whose registry serves tarballs on a different domain. CVSS scores it 7.6 (high); no vendor rating is given. The advisory names no fixed version.

¿Qué significa?Deno sends the scope's .npmrc auth credentials to a tarball URL on another domain, which exposes the registry token to whatever host serves that tarball.
¿Quién está afectado?The issue is in Deno 1.44.0 and involves a private npm registry scope that uses .npmrc credentials and serves tarball URLs on a different domain. Check the installed version with deno --version and review the .npmrc scope settings and the registry's tarball URL domains.
¿Qué hacer?The advisory names no fixed version and no patch ids, so no upgrade target is available from the sources.
no-patchRotate the registry credentials if the private registry ever serves tarballs at a different domain.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Uses .npmrc credentials for a private npm registry scope“All users relying on .npmrc are potentially affected by this vulnerability”
02
The private registry serves tarball URLs on a different domain“if their private registry references tarball URLs at a different domain”
03
Deno 1.44.0 is affected“An issue in .npmrc support in Deno 1.44.0”
¿Quién debe revisar?Teams running Deno 1.44.0 with .npmrc-based private npm registry auth, including deno install, npm: specifier auto-install and LSP users.
MitigaciónRotate your registry credentials if your private registry ever serves tarballs at a different domain.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:R
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:L
AltoBajoNinguno
DisponibilidadA:L
AltoBajoNinguno
Versiones

Versiones afectadas

1.44.0
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
deno
Sin parche — — —
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/denoland/deno/security/advisories/GHSA-rfc6-h225-3vxv
Otrahttps://github.com/denoland/deno/commit/566adb7c0a0c0845e90a6e867a2c0ef5d2ada575
Otrahttps://github.com/npm/cli/wiki/%22No-auth-for-URI,-but-auth-present-for-scoped-registry%22

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.