llamaCVEVulnerability Intelligence
/
Craftcms CMS

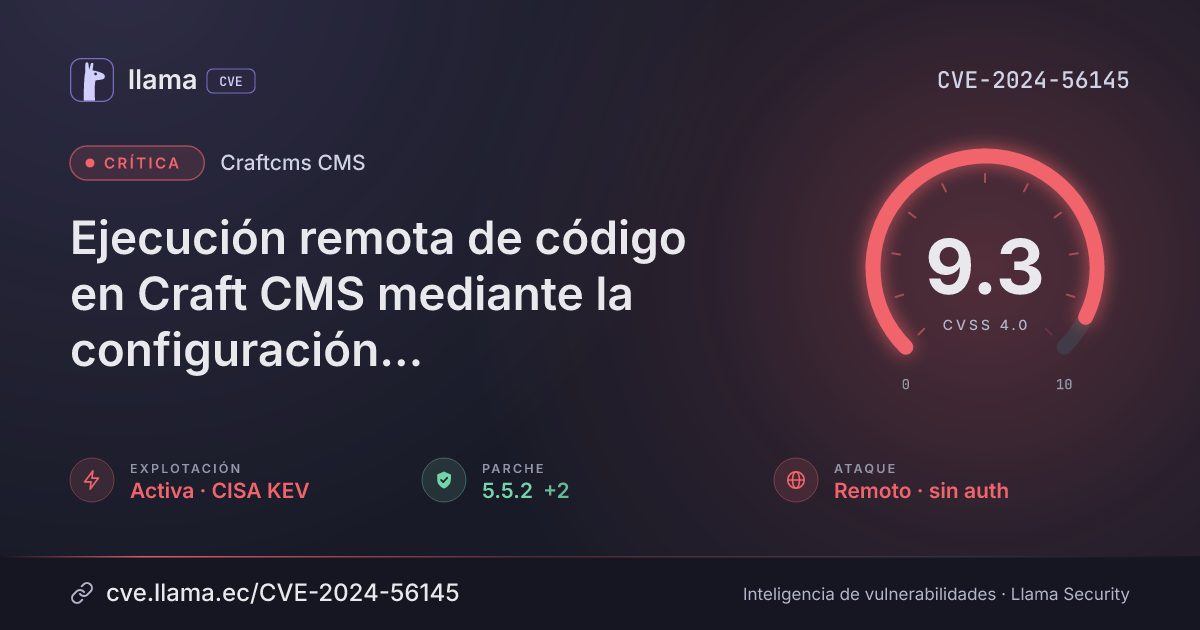
CVE-2024-56145

Craftcms CMS remote code execution via PHP register_argc_argv setting

An attacker could remotely run arbitrary code on the affected server when a PHP setting is enabled.

Texto original en inglés · Ver en español

CISA KEV · explotación activaCrítica · en CISA KEV, EPSS ≥ 10 %Parche disponible
Descargar PNG JSON
CVSS 4.0
9.3
Crítica
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónActivaEn CISA KEV desde 2 jun 2025
Exploits públicos0Explotada, pero sin código público enlazado
Parche3 versiones3.9.14 · 4.13.2 · 5.5.2
Exposición702 dDesde la divulgación, 18 dic 2024, 3:37 p. m.
EPSS ≥ 10 %22 oct 2026Fecha en que la probabilidad de explotación superó el umbral
Decisión estimadaActuar
Parchear de inmediato
Estimación de Llama con el árbol SSVC de CISA a partir de vector CVSS 4.0 y la evidencia de explotación (sin evaluación oficial): explotación activa (CISA KEV), automatizable e impacto técnico total. Plazo KEV: 23 jun 2025.
¿Escuchas eso? Es tu SIEM llorando.Si lees esto con calma, no entendiste. ¡Parche YA!
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Modificada
Explotación
CISA KEV
Umbral EPSS
Remediación
Plazo KEV
Monitoreo
Detectada
Verificada
18 dic 24
2 jun 25
23 jun 25
21 oct 25
22 oct 26
14 nov 26
21 nov 26
18 dic 24
12 jun 25
5 dic 25
30 may 26
21 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2024-56145 divulgada · CVSS 9.3 (CNA)
Explotación CISA KEV Agregada al catálogo de vulnerabilidades explotadas
Remediación Plazo KEV Fecha límite de remediación para agencias federales (EE. UU.)
Divulgación Modificada Última actualización del registro
Explotación Umbral EPSS La probabilidad de explotación supera el 10 %
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 13 nov 2026

Craft CMS (craftcms/cms) has a flaw that could let an attacker run code on the site, and they can reach it remotely without logging in. It only affects sites with a non-default PHP setting, `register_argc_argv`, turned on, and it is being exploited in attacks.

Affects Craft CMS 3.0.0 to before 3.9.14, 4.0.0-RC1 to before 4.13.2, and 5.0.0-RC1 to before 5.5.2, when PHP's register_argc_argv is enabled. Fixed in 3.9.14, 4.13.2 and 5.5.2.

¿Qué significa?When PHP's register_argc_argv setting is enabled, a flaw in Craft CMS could allow remote code execution on the site. The advisory describes it as a potential RCE.
¿Quién está afectado?Craft CMS 3.0.0 up to before 3.9.14, 4.0.0-RC1 up to before 4.13.2, and 5.0.0-RC1 up to before 5.5.2 are affected. The advisory says the issue applies when php.ini has register_argc_argv enabled, so check that setting in php.ini and the installed Craft CMS version.
¿Qué hacer?Upgrade to Craft CMS 5.5.2, 4.13.2 or 3.9.14, depending on the major version in use. If upgrading is not yet possible, the advisory says to disable register_argc_argv in php.ini.
Descripción original del registro

Craft is a flexible, user-friendly CMS for creating custom digital experiences on the web and beyond. Users of affected versions are affected by this vulnerability if their php.ini configuration has `register_argc_argv` enabled. For these users an unspecified remote code execution vector is present. Users are advised to update to version 3.9.14, 4.13.2, or 5.5.2. Users unable to upgrade should disable `register_argc_argv` to mitigate the issue.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
php.ini has register_argc_argv enabled“You are affected if your php.ini configuration has register_argc_argv enabled.”
02
Craft CMS 5.0.0-RC1 to before 5.5.2, 4.0.0-RC1 to before 4.13.2, or 3.0.0 to before 3.9.14“>= 5.0.0-RC1, < 5.5.2”
¿Quién debe revisar?Teams running Craft CMS (craftcms/cms) 3.x, 4.x or 5.x on PHP with register_argc_argv enabled in php.ini.
MitigaciónIf you can't upgrade yet, disable register_argc_argv in php.ini.
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:N
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:H
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 10.0 (muy fácil) · sin evidencia de explotación.
Versiones

Rangos afectados

Afectada Corregida
cms · craftcms/cms≥ 3.0.0 < 3.9.14
cms · craftcms/cms≥ 4.0.0-RC1 < 4.13.2
cms · craftcms/cms≥ 5.0.0-RC1 < 5.5.2
3.0.0
3.9.14
4.0.0-RC1
4.13.2
5.0.0-RC1
5.5.2
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
cms
Corregida 3.9.14, 4.13.2, 5.5.2 — —
Versiones corregidas3.9.144.13.25.5.2
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/craftcms/cms/security/advisories/GHSA-2p6p-9rc9-62j9
Otrahttps://github.com/craftcms/cms/commit/82e893fb794d30563da296bca31379c0df0079b3

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.