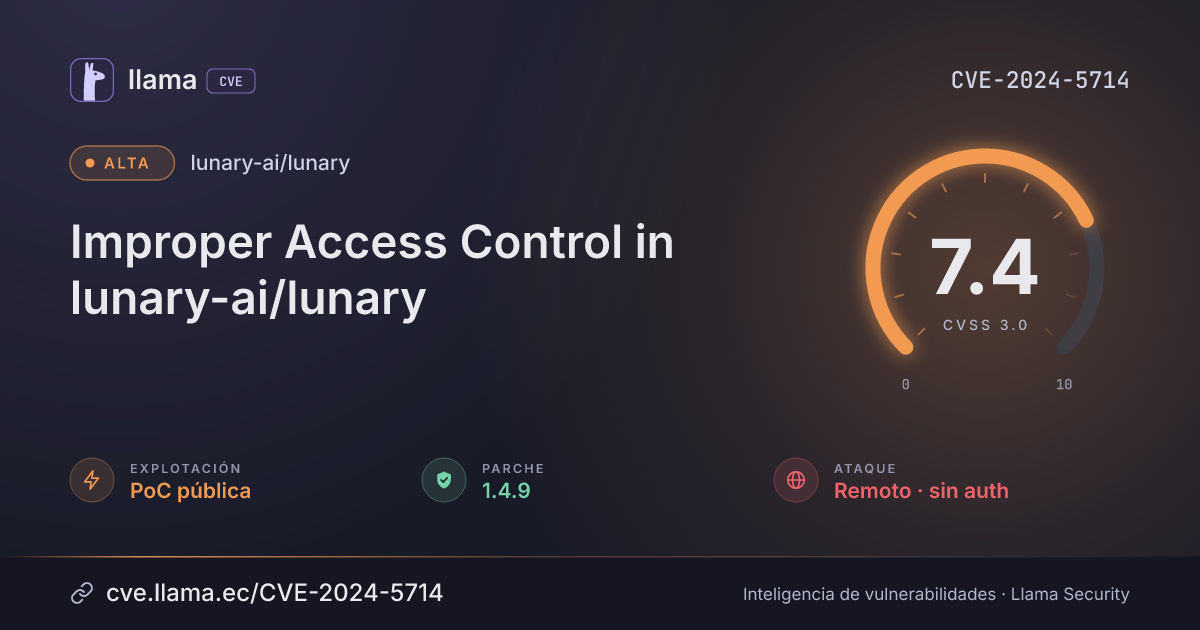
CVE-2024-5714
Improper Access Control in lunary-ai/lunary
CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N
Fuente: CNA
CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:NCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2024-5714 divulgada · CVSS 7.4 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación PoC pública | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
In lunary-ai/lunary version 1.2.4, an improper access control vulnerability allows members with team management permissions to manipulate project identifiers in requests, enabling them to invite users to projects in other organizations, change members to projects in other organizations with escalated privileges, and change members from other organizations to their own or other projects, also with escalated privileges. This vulnerability is due to the backend's failure to validate project identifiers against the current user's organization ID and projects belonging to it, as well as a misconfiguration in attribute naming (`org_id` should be `orgId`) that prevents proper user organization validation. As a result, attackers can cause inconsistencies on the platform for affected users and organizations, including unauthorized privilege escalation. The issue is present in the backend API endpoints for user invitation and modification, specifically in the handling of project IDs in requests.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
lunary-ai/lunary |
Corregida | 1.4.9 | — | — |
1.4.9Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://huntr.com/bounties/8cff4afa-131b-4a7e-9f0d-8a3c69f3d024https://github.com/lunary-ai/lunary/commit/43206bacac3b43ad9f2db6dafd165e61a21e6b97Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.