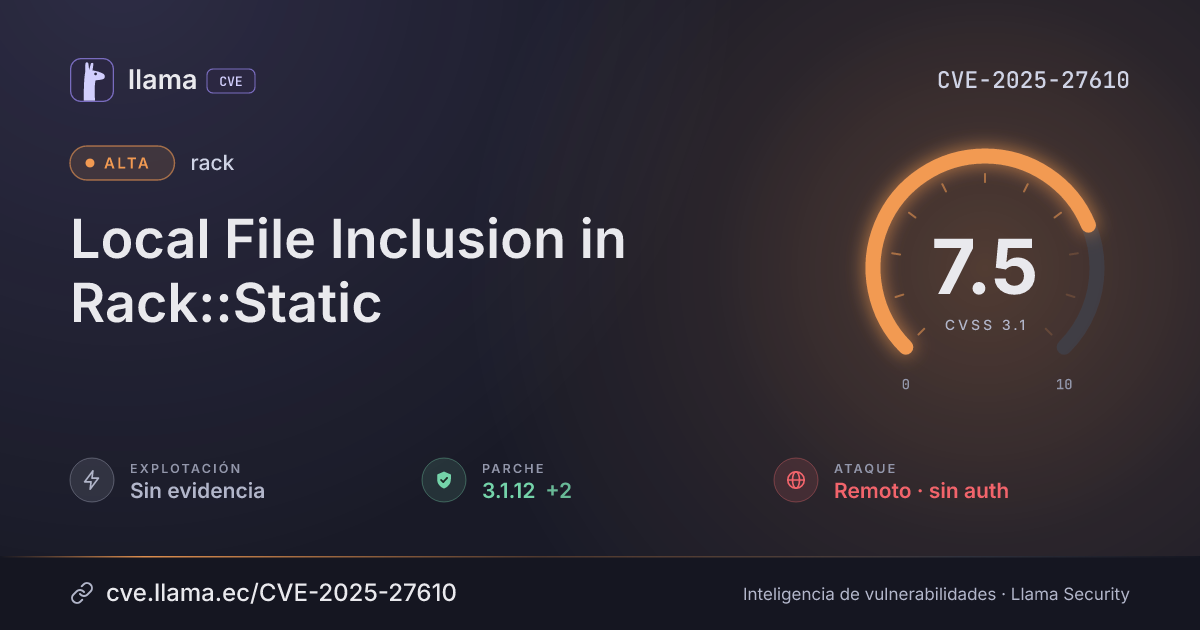
CVE-2025-27610
Local File Inclusion in Rack::Static
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2025-27610 divulgada · CVSS 7.5 (CNA) | |
| Remediación | Parche 2.2.13 | rack · 0 d desde divulgación | |
| Remediación | Parche 3.0.14 | rack · 0 d desde divulgación | |
| Remediación | Parche 3.1.12 | rack · 0 d desde divulgación | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Rack provides an interface for developing web applications in Ruby. Prior to versions 2.2.13, 3.0.14, and 3.1.12, `Rack::Static` can serve files under the specified `root:` even if `urls:` are provided, which may expose other files under the specified `root:` unexpectedly. The vulnerability occurs because `Rack::Static` does not properly sanitize user-supplied paths before serving files. Specifically, encoded path traversal sequences are not correctly validated, allowing attackers to access files outside the designated static file directory. By exploiting this vulnerability, an attacker can gain access to all files under the specified `root:` directory, provided they are able to determine then path of the file. Versions 2.2.13, 3.0.14, and 3.1.12 contain a patch for the issue. Other mitigations include removing usage of `Rack::Static`, or ensuring that `root:` points at a directory path which only contains files which should be accessed publicly. It is likely that a CDN or similar static file server would also mitigate the issue.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
rubygemsrack |
Corregida | 2.2.13, 3.0.14, 3.1.12 | 0 d · 0 d · 0 d | 3.2.8 no afectada |
2.2.133.0.143.1.12Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/rack/rack/security/advisories/GHSA-7wqh-767x-r66vhttps://github.com/rack/rack/commit/50caab74fa01ee8f5dbdee7bb2782126d20c6583https://lists.debian.org/debian-lts-announce/2025/03/msg00016.htmlLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.