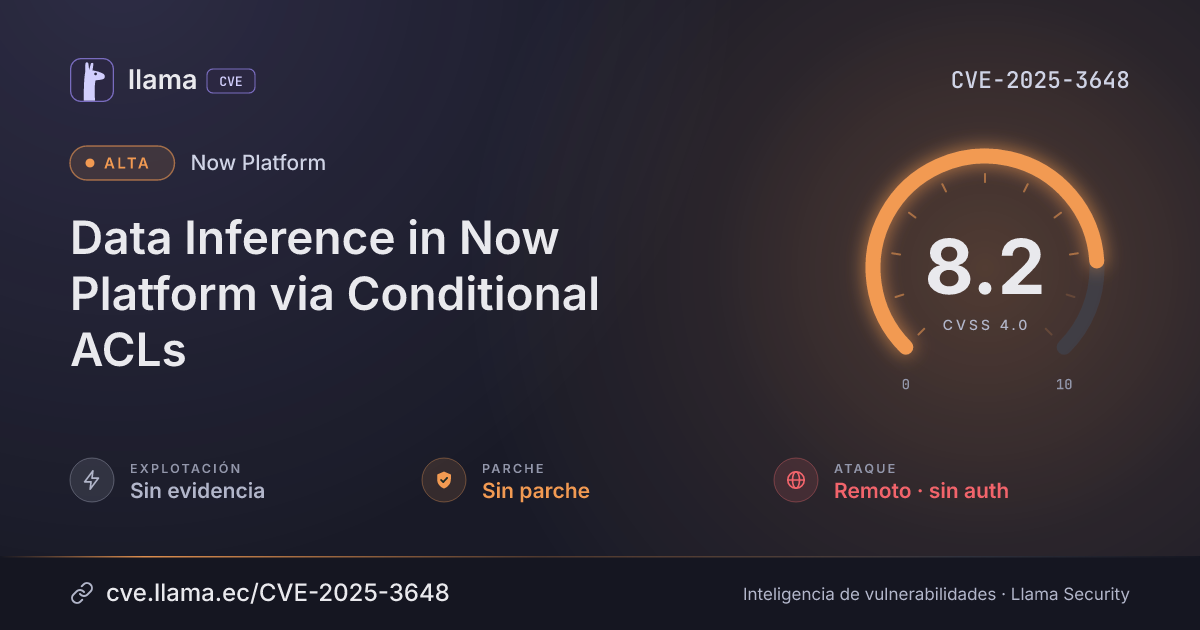
CVE-2025-3648
Data Inference in Now Platform via Conditional ACLs
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2025-3648 divulgada · CVSS 8.2 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
A vulnerability has been identified in the Now Platform that could result in data being inferred without authorization. Under certain conditional access control list (ACL) configurations, this vulnerability could enable unauthenticated and authenticated users to use range query requests to infer instance data that is not intended to be accessible to them. To assist customers in enhancing access controls, ServiceNow has introduced additional access control frameworks in Xanadu and Yokohama, such as Query ACLs, Security Data Filters and Deny-Unless ACLs. Additionally, in May 2025, ServiceNow delivered to customers a security update that is designed to enhance customer ACL configurations. Customers, please review the KB Articles in the References section.
Desglose de métricas
Versiones afectadas
AspenEstado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Now Platform |
Sin parche | — | — | — |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://support.servicenow.com/kb?id=kb_article_view&sysparm_article=KB2139567https://support.servicenow.com/kb?id=kb_article_view&sysparm_article=KB2046494https://support.servicenow.com/kb?id=kb_article_view&sysparm_article=KB2256712Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.