llamaCVEVulnerability Intelligence
/
Samsung MagicINFO 9 Server

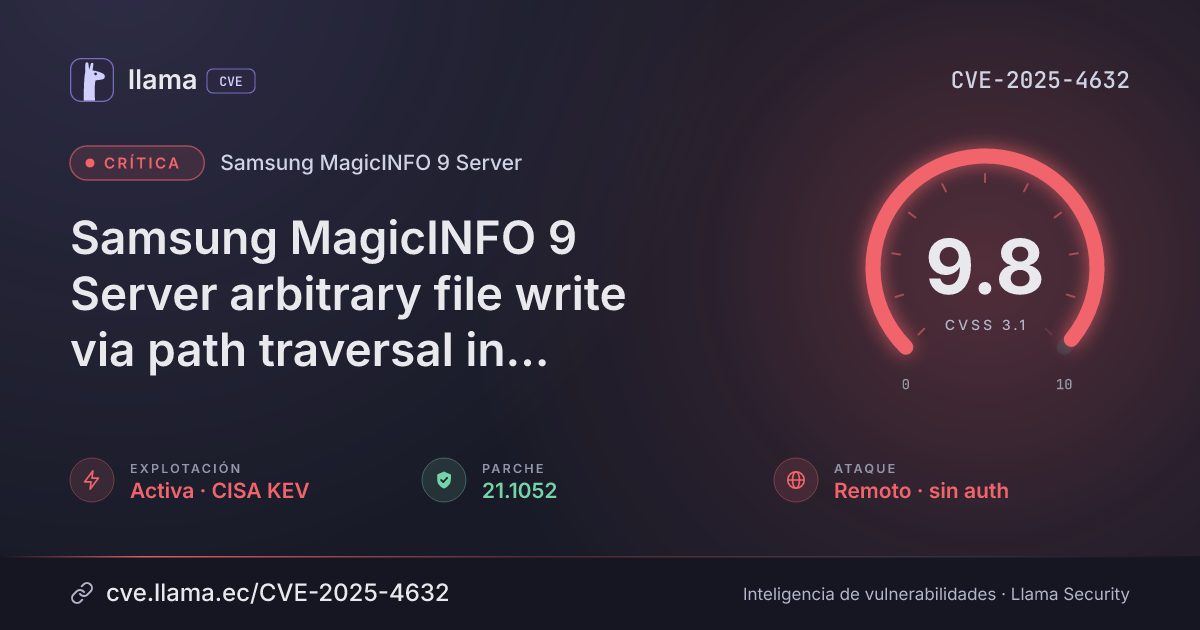
CVE-2025-4632

Samsung MagicINFO 9 Server arbitrary file write via path traversal in signage server

An attacker can write arbitrary files as system and potentially take full control of the server.

CISA KEV · explotación activaCrítica · en CISA KEV, EPSS ≥ 10 %Explotación activaParche disponible
Descargar PNG JSON
CVSS 3.1
9.8
Crítica
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H Fuente: CNA
ExplotaciónActivaEn CISA KEV desde 22 may 2025
Exploits públicos0Ninguno conocido
Parche1 versión21.1052
Exposición555 dDesde la divulgación, 13 may 2025, 12:19 a. m.
EPSS ≥ 10 %22 oct 2026Fecha en que la probabilidad de explotación superó el umbral
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Modificada
Explotación
CISA KEV
Umbral EPSS
Remediación
Plazo KEV
Monitoreo
Detectada
Verificada
13 may 25
22 may 25
12 jun 25
26 feb 26
22 oct 26
15 nov 26
19 nov 26
13 may 25
29 sept 25
14 feb 26
3 jul 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2025-4632 divulgada · CVSS 9.8 (CNA)
Explotación CISA KEV Agregada al catálogo de vulnerabilidades explotadas
Remediación Plazo KEV Fecha límite de remediación para agencias federales (EE. UU.)
Divulgación Modificada Última actualización del registro
Explotación Umbral EPSS La probabilidad de explotación supera el 10 %
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 14 nov 2026

A path traversal flaw in Samsung Electronics' MagicINFO 9 Server lets an attacker write arbitrary files with system authority, and it can be reached remotely over the network without logging in. It is listed in CISA's Known Exploited Vulnerabilities catalog, so attacks are happening.

Affects Samsung MagicINFO 9 Server versions before 21.1052, where attackers can write arbitrary files with system authority. The facts list 21.1052 as the version boundary but name no separate fix.

¿Qué significa?The server does not properly restrict file paths to an allowed directory (a path traversal flaw). This lets attackers write arbitrary files on the MagicINFO 9 Server with system authority.
¿Quién está afectado?Samsung MagicINFO 9 Server versions before 21.1052 are affected, according to the advisory data. To check, look at the installed MagicINFO 9 Server version in the server's about or version information and compare it with 21.1052.
¿Qué hacer?The affected range ends at 21.1052, so moving to version 21.1052 or later puts the server outside the listed range. The facts give no workaround and name no other fix.
Descripción original del registro

Improper limitation of a pathname to a restricted directory vulnerability in Samsung MagicINFO 9 Server version before 21.1052 allows attackers to write arbitrary file as system authority.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Samsung MagicINFO 9 Server is affected, versions before 21.1052“Improper limitation of a pathname to a restricted directory vulnerability in Samsung MagicINFO 9 Server allows attackers to write arbitrary file as system authority.”
¿Quién debe revisar?Teams running Samsung MagicINFO 9 Server (digital signage management) on versions before 21.1052.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:H
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
MagicINFO 9 Server< 21.1052
21.1052
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
MagicINFO 9 Server
Corregida 21.1052 — —
Versiones corregidas21.1052
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Otrahttps://security.samsungtv.com/securityUpdates#SVP-MAY-2025

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.