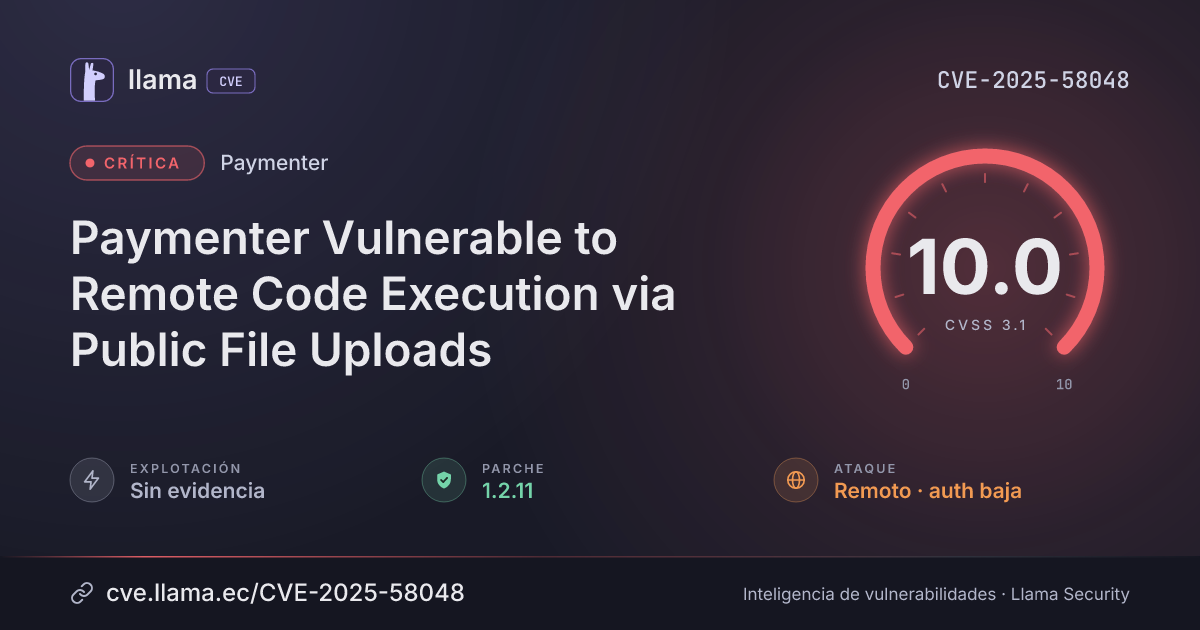
CVE-2025-58048
Paymenter Vulnerable to Remote Code Execution via Public File Uploads
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2025-58048 divulgada · CVSS 10 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Paymenter is a free and open-source webshop solution for hostings. Prior to version 1.2.11, the ticket attachments functionality in Paymenter allows a malicious authenticated user to upload arbitrary files. This could result in sensitive data extraction from the database, credentials being read from configuration files, and arbitrary system commands being run under the web server user context. This vulnerability was patched by commit 87c3db4 and was released under the version 1.2.11 tag without any other code modifications compared to version 1.2.10. If upgrading is not immediately possible, administrators can mitigate this vulnerability with one or more of the following measures: updating nginx config to download attachments instead of executing them or disallowing access to /storage/ fully using a WAF such as Cloudflare.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Paymenter |
Corregida | 1.2.11 | — | — |
1.2.11Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/Paymenter/Paymenter/security/advisories/GHSA-5pm9-r2m8-rcmjhttps://github.com/Paymenter/Paymenter/commit/87c3db42282ada1e3cda54b9a01f846926c0669bhttps://github.com/Paymenter/Paymenter/releases/tag/v1.2.11Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.