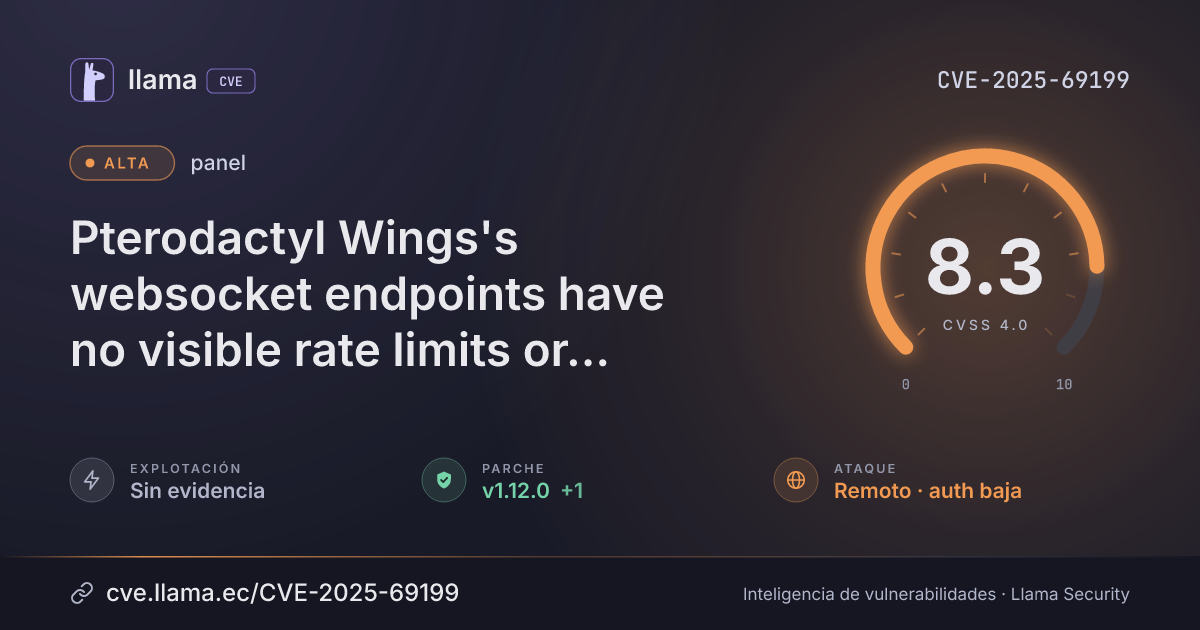
CVE-2025-69199
Pterodactyl Wings's websocket endpoints have no visible rate limits or monitoring, allowing for DOS attacks under certain circumstances
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:H
Fuente: CNA
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:HCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche v1.12.0 | github.com/pterodactyl/wings · -13 d desde divulgación | |
| Divulgación | Publicada | CVE-2025-69199 divulgada · CVSS 8.3 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Wings is the server control plane for Pterodactyl, a free, open-source game server management panel. Prior to version 1.12.0, websockets within wings lack proper rate limiting and throttling. As a result a malicious user can open a large number of connections and then request data through these sockets, causing an excessive volume of data over the network and overloading the host system memory and cpu. Additionally, there is not a limit applied to the total size of messages being sent or received, allowing a malicious user to open thousands of websocket connections and then send massive volumes of information over the socket, overloading the host network, and causing increased CPU and memory load within Wings. Version 1.12.0 patches the issue.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gogithub.com/pterodactyl/wings |
Corregida | v1.12.0 | -13 d | v1.13.5 no afectada |
1.12.0v1.12.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/pterodactyl/panel/security/advisories/GHSA-8w7m-w749-rx98Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.