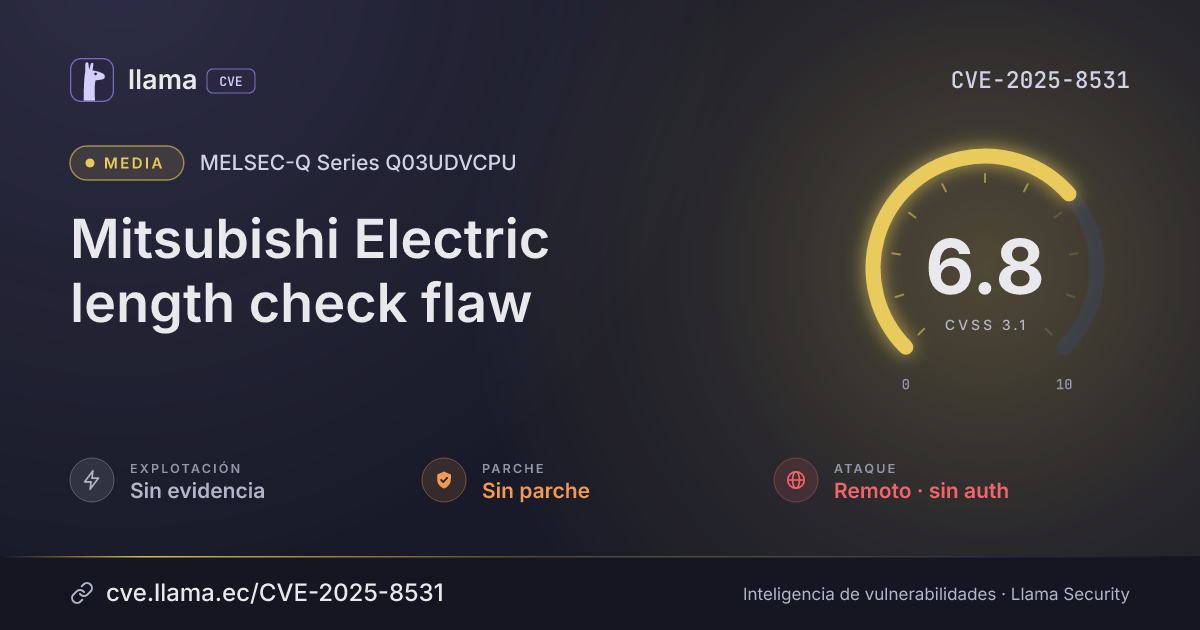
CVE-2025-8531
Mitsubishi Electric length check flaw
CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:N/I:N/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2025-8531 divulgada · CVSS 6.8 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Improper Handling of Length Parameter Inconsistency vulnerability in Mitsubishi Electric Corporation MELSEC-Q Series Q03UDVCPU, Q04UDVCPU, Q06UDVCPU, Q13UDVCPU, Q26UDVCPU, Q04UDPVCPU, Q06UDPVCPU, Q13UDPVCPU, and Q26UDPVCPU with the first 5 digits of serial No. "24082" to "27081" allows a remote attacker to cause an integer underflow by sending specially crafted packets to the affected product to stop Ethernet communication and the execution of control programs on the product, when the user authentication function is enabled. The user authentication function is enabled by default only when settings are configured by GX Works2, which complies with the Cybersecurity Law of the People's Republic of China, and is normally disabled.
Desglose de métricas
Versiones afectadas
The first 5 digits of serial No. "24082" to "27081"Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
MELSEC-Q Series Q03UDVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q04UDVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q06UDVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q13UDVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q26UDVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q04UDPVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q06UDPVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q13UDPVCPU |
Sin parche | — | — | — |
MELSEC-Q Series Q26UDPVCPU |
Sin parche | — | — | — |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://www.mitsubishielectric.com/psirt/vulnerability/pdf/2025-013_en.pdfhttps://jvn.jp/vu/JVNVU97846038/https://www.cisa.gov/news-events/ics-advisories/icsa-25-266-02Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.