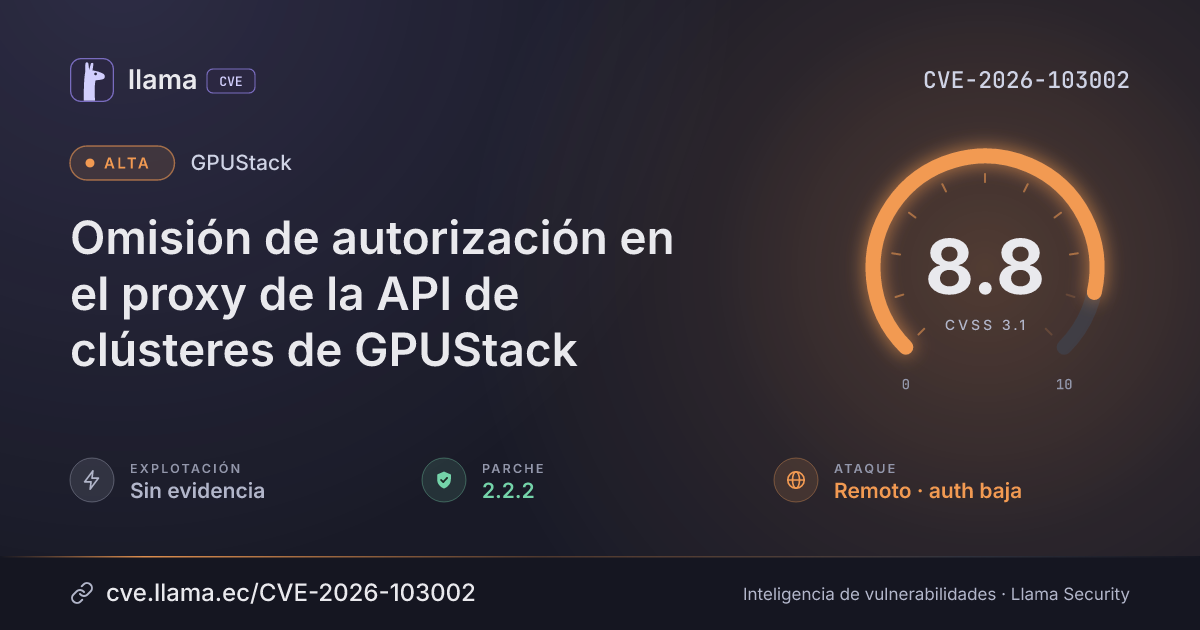
CVE-2026-103002
GPUStack authorization bypass in cluster API proxy
A low-privilege user can reach clusters they should not access and read, change, or delete resources.
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 2.2.2 | gpustack · -103 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-103002 divulgada · CVSS 8.8 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
GPUStack, an open-source GPU cluster manager for AI model serving, has missing authorization checks on its cluster API proxy that affect versions 2.2.0 through 2.2.2. An authenticated low-privilege user can remotely reach Kubernetes clusters they should not access and read, change, or delete resources using a worker's ServiceAccount permissions, and this can lead to code execution in the target cluster when the cluster uses a Kubernetes provider with a reachable worker.
Only affects GPUStack 2.2.0 up to 2.2.2 with a Kubernetes-provider cluster that has a reachable worker. Fixed in 2.2.2.
Descripción original del registro (GitHub_M)
GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 2.2.0 until 2.2.2, cluster_apiserver_proxy forwarded an authenticated non-administrator's requests to a selected Kubernetes cluster without a resource-level authorization check. The proxy used a reachable worker's Kubernetes ServiceAccount credentials, so the caller could read sensitive resources, create or modify workloads, or delete resources according to that ServiceAccount's permissions. Exploitation required a Kubernetes-provider cluster with a reachable worker, and attacker-controlled workloads could result in code execution in the target cluster. This issue is fixed in version 2.2.2.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypigpustack |
Corregida | 2.2.2 | -103 d | 2.3.1 no afectada |
2.2.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/gpustack/gpustack/security/advisories/GHSA-3hch-x692-6qj3https://github.com/gpustack/gpustack/pull/5911https://github.com/gpustack/gpustack/pull/5936https://github.com/gpustack/gpustack/commit/363191fa1da7e1426c6041f78b3cf00aff2622fehttps://github.com/gpustack/gpustack/commit/cdd67467e0f314609dc82216e142940d321abfedhttps://github.com/gpustack/gpustack/releases/tag/v2.2.2Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.