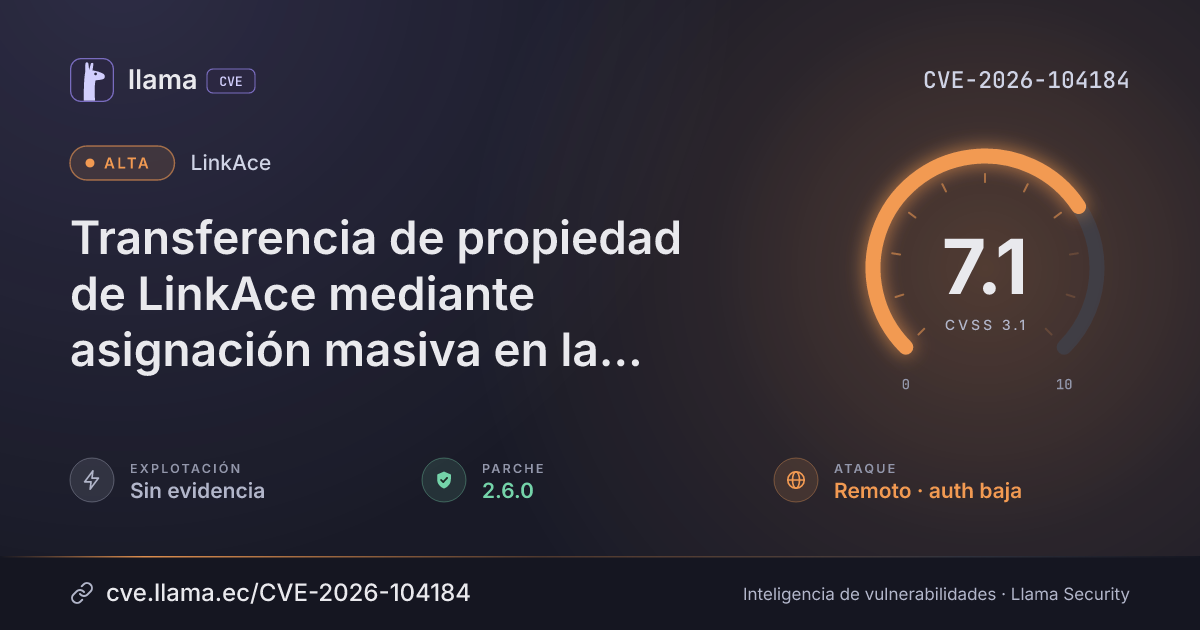
CVE-2026-104184
LinkAce ownership transfer via mass assignment in API link update
An attacker with a basic login can move editable links into other users' collections or orphan them.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:H/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-104184 divulgada · CVSS 7.1 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
LinkAce, a self-hosted link archive from Kovah, has a flaw in its API link update that lets a remote attacker with a low-privilege login transfer a link they are allowed to update. By setting the user_id field, the attacker can move the link into another user's bookmark collection or leave it orphaned from any real account.
Descripción original del registro (GitHub_M)
LinkAce is a self-hosted archive to collect website links. Prior to 2.6.0, LinkController::update() in app/Http/Controllers/API/LinkController.php passes $request->all() to the repository update method even though user_id is fillable and is not an allowed field in the validated update request. An authenticated API user who is authorized to update a link can therefore assign an arbitrary or nonexistent user_id, transferring the link into another user's bookmark collection or orphaning it from any real account. The web update controller is unaffected because it passes only validated fields. This issue is fixed in version 2.6.0.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
LinkAce |
Corregida | 2.6.0 | — | — |
2.6.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/Kovah/LinkAce/security/advisories/GHSA-p25r-m7hm-2rh2https://github.com/Kovah/LinkAce/pull/1125https://github.com/Kovah/LinkAce/commit/f71134c2e8f2b92e26eef63494542f877657bb67https://github.com/Kovah/LinkAce/releases/tag/v2.6.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.