llamaCVEVulnerability Intelligence
/
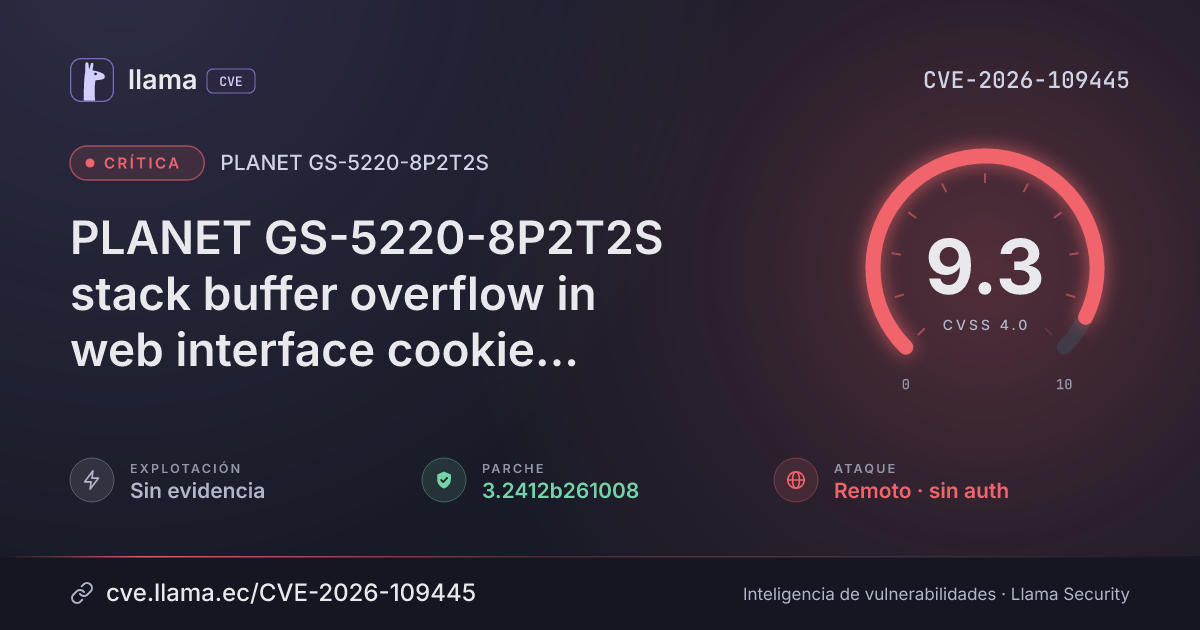
PLANET GS-5220-8P2T2S

CVE-2026-109445

PLANET GS-5220-8P2T2S stack buffer overflow in web interface cookie handling

A remote attacker can send a crafted request without logging in to corrupt memory and possibly crash the device.

UnclearParche disponiblestack buffer overflow
Descargar PNG JSON
CVSS 4.0
9.3
Crítica
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche1 versión3.2412b261008
Exposición6 dDesde la divulgación, 13 nov 2026, 9:48 a. m.
Detección7 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCAtender
Priorizar en el próximo ciclo de cambios
Sin explotación conocida, automatizable e impacto técnico total. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada +1
Fuente: ENISA EUVD
Verificada
13 nov 26
15 nov 26
18 nov 26
19 nov 26
13 nov 26
15 nov 26
16 nov 26
18 nov 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-109445 divulgada · CVSS 9.3 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 13 nov 2026

The PLANET GS-5220-8P2T2S switch has a stack buffer overflow in its web interface, triggered by an oversized webstax_auth cookie. A remote attacker can send a crafted request without logging in, which can corrupt memory and may crash the device.

¿Qué significa?A stack buffer overflow in the webstax_auth cookie handling lets crafted input overwrite memory on the device's stack, corrupting it and overwriting a saved return address. The advisory describes this as memory corruption and potential denial of service, and it does not confirm remote code execution on the hardware.
¿Quién está afectado?The affected product is PLANET GS-5220-8P2T2S hardware version 3.0 running firmware earlier than v3.2412b261008. To check, look at the hardware version on the device label or system information page and compare the firmware version shown there with v3.2412b261008.
¿Qué hacer?The facts provided do not name a fixed version or vendor patch identifier for this issue, so no specific upgrade target can be given. Check PLANET's support channels for a firmware update for the GS-5220-8P2T2S that is v3.2412b261008 or later.
Descripción original del registro (VulnCheck)

PLANET GS-5220-8P2T2S (hardware version 3.0) firmware versions before 3.2412b261008 contains a stack-based buffer overflow vulnerability that allows unauthenticated attackers to corrupt stack memory by submitting an oversized webstax_auth HTTP Cookie value that is copied into a fixed-size stack buffer without length validation. Attackers can send a crafted unauthenticated HTTP request with an oversized cookie to overwrite the saved return address and corrupt stack memory, leading to memory corruption and potential denial of service on the device.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Hardware version 3.0 of PLANET GS-5220-8P2T2S“PLANET GS-5220-8P2T2S (hardware version 3.0)”
02
Firmware earlier than v3.2412b261008 (per VulnCheck's affected range)“firmware versions before 3.2412b261008”
¿Quién debe revisar?Teams operating PLANET GS-5220-8P2T2S V3 (hardware version 3.0) switches with firmware before v3.2412b261022, including web management interface exposure
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:N
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:H
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
PLANET GS-5220-8P2T2S< 3.2412b261008
3.2412b261008
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
PLANET GS-5220-8P2T2S
Corregida 3.2412b261008 — —
Versiones corregidas3.2412b261008
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALVulnCheck
Referencias
Fabricantehttps://www.planet.com.tw/en/support/security-advisory/12
Otrahttps://www.vulncheck.com/advisories/planet-gs-5220-8p2t2s-stack-buffer-overflow-via-webstax-auth-cookie

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.