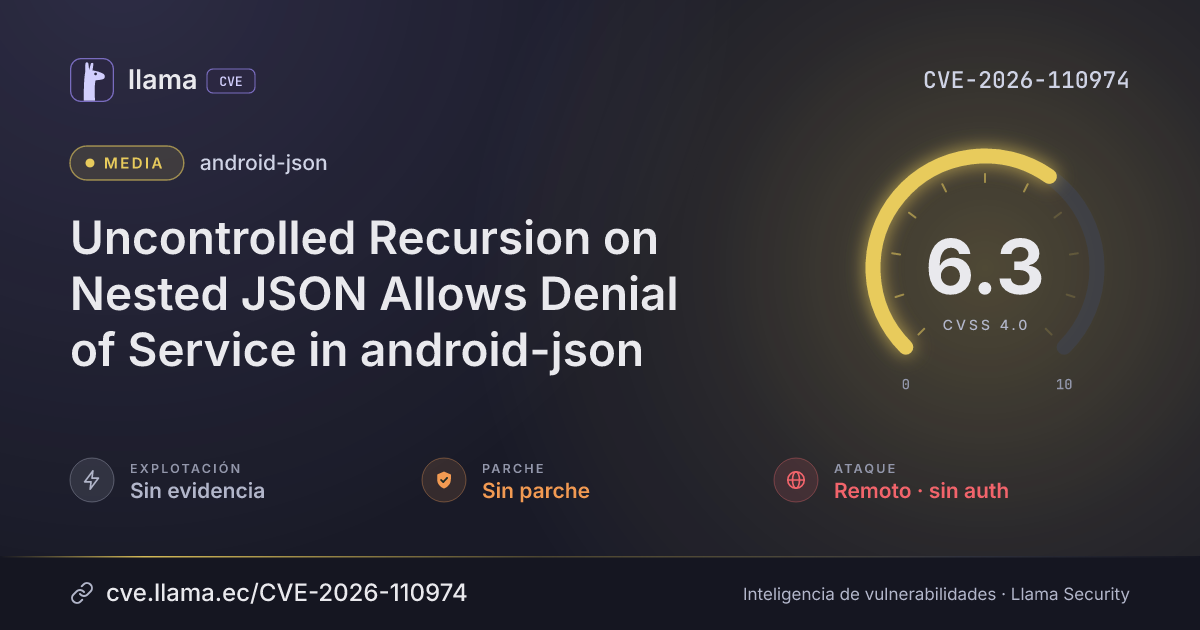
CVE-2026-110974
Uncontrolled Recursion on Nested JSON Allows Denial of Service in android-json
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:N/VI:N/VA:L/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-110974 divulgada · CVSS 6.3 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
The com.vaadin.external.google:android-json library, a repackaged copy of the org.json parser, is affected. A deeply nested JSON document can cause the parser to crash the thread handling it with a StackOverflowError, so applications that parse untrusted JSON can be made to fail.
Descripción original del registro (Vaadin)
The org.json parser in com.vaadin.external.google:android-json recurses once per nesting level with no depth limit: JSONTokener.nextValue() calls readArray() and readObject(), which call nextValue() again. A deeply nested JSON document, around 20 KB of nested arrays with the default thread stack, makes the JSONArray and JSONObject constructors throw a raw java.lang.StackOverflowError instead of a JSONException. Any application that parses untrusted JSON with this library can be made to fail the thread doing the parsing. The artifact is a 2013 repackage of third-party org.json classes, published once and never maintained, and no fixed version will be released. Users of the affected version should apply the following mitigation. Product version com.vaadin.external.google:android-json 0.0.20131108.vaadin1 Mitigation No fixed version will be released. Replace the artifact with an org.json implementation that limits the nesting depth, such as org.json:json 20231013 or later. Artifacts Maven coordinates / Vulnerable versions / Fixed version com.vaadin.external.google:android-json / 0.0.20131108.vaadin1 / none
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
mavencom.vaadin.external.google:android-json |
Sin parche | — | — | 0.0.20131108.vaadin1 afectada |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://repo.maven.apache.org/maven2/com/vaadin/external/google/android-json/0.0.20131108.vaadin1/Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.