llamaCVEVulnerability Intelligence
/
framework

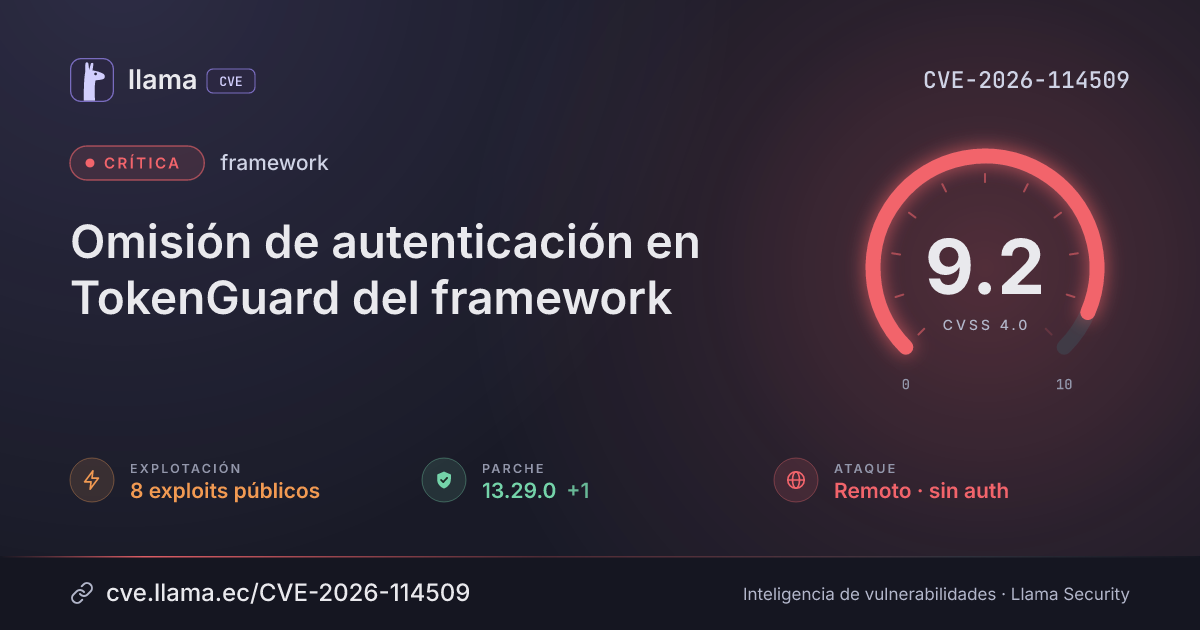
CVE-2026-114509

framework authentication bypass in TokenGuard

An unauthenticated attacker can send a crafted credential to log in as another user and take over their account.

UnclearParche disponibleauthentication bypass
Descargar PNG JSON
CVSS 4.0
9.2
Crítica
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónExploit públicoSSVC de CISA-ADP decía «ninguna» · ajustado por exploit detectado
Exploits públicos82 fuentes · 1 confirmado en GitHub
Parche2 versiones12.68.0 · 13.29.0
Exposición30 dDesde la divulgación, 21 oct 2026, 4:49 p. m.
Detección6 hDesde la divulgación hasta su ingreso al índice
Decisión SSVC · ajustadaAtender
Priorizar en el próximo ciclo de cambios
Exploit público disponible (8), no automatizable e impacto técnico total. Decisión recalculada: la evaluación SSVC original indicaba explotación «ninguna». Se eleva a «Atender» por existir un exploit funcional público. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Exploit en GitHub
Remediación
Monitoreo
Detectada
Fuente: OSV
Fuente: NIST NVD
Fuente: PoC-in-GitHub
Fuente: Nuclei templates
Verificada
21 oct 26
22 oct 26
23 oct 26
28 oct 26
30 oct 26
4 nov 26
16 nov 26
21 nov 26
21 oct 26
29 oct 26
6 nov 26
13 nov 26
21 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-114509 divulgada · CVSS 9.2 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: OSV Registro visto por primera vez en OSV
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Explotación Exploit en GitHub Nguemoue/project2026_20261030_tokengate
Monitoreo Fuente: PoC-in-GitHub Registro visto por primera vez en PoC-in-GitHub
Monitoreo Fuente: Nuclei templates Registro visto por primera vez en Nuclei templates
Monitoreo Verificada Última verificación contra las fuentes
Resumen

Laravel is a web application framework. Prior to 12.68.0 and 13.29.0, TokenGuard configured as a standard token-based API guard does not reject a crafted non-string credential. Under affected MySQL or MariaDB configurations, the authentication lookup can match an unintended existing user, allowing an unauthenticated attacker to bypass authentication and take over an account on routes protected by TokenGuard. This issue is fixed in versions 12.68.0 and 13.29.0.

Laravel below 12.68.0 or 13.29.0 is affected when it uses a standard token-based API guard (TokenGuard), with MySQL or MariaDB database configurations. Fixed in 12.68.0 and 13.29.0.

¿Qué significa?When API credentials are not strings, the TokenGuard authentication check can be bypassed. An attacker can then log in as an existing user without that user's API token, which takes over the account on routes protected by the guard.
¿Quién está afectado?The affected versions are Laravel below 12.68.0 or 13.29.0 that use a standard token-based API guard (TokenGuard). The issue is limited to certain database configurations, specifically MySQL or MariaDB. To check, run php artisan --version or look up laravel/framework in composer.lock, then check the guard settings in config/auth.php.
¿Qué hacer?Upgrade laravel/framework to 12.68.0 or 13.29.0, or to a later release in the same line. The fix data does not list a workaround.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Laravel below 12.68.0 or 13.29.0 with a standard token-based API guard (TokenGuard)“when configured with a standard token-based API guard”
02
MySQL or MariaDB database configuration“Under certain database configurations (MySQL/MariaDB)”
¿Quién debe revisar?Teams running laravel/framework (Composer) before 12.68.0 or 13.29.0 that use TokenGuard API guards on MySQL or MariaDB
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:P
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:H
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 7.1 (fácil) · +2.9 por exploit público.
Versiones

Rangos afectados

Afectada Corregida
laravel/framework< 10.50.4
laravel/framework≥ 11.0.0 < 11.56.1
framework · laravel/framework≥ 12.0.0 < 12.68.0
laravel/framework≥ 13.0.0 < 13.27.0
framework≥ 13.0.0 < 13.29.0
10.50.4
11.0.0
11.56.1
12.0.0
12.68.0
13.0.0
13.27.0
13.29.0
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
framework
Corregida 12.68.0, 13.29.0 — —
Versiones corregidas12.68.013.29.0
Explotación

Arsenal público

Exploit-DB
—
0
Metasploit
—
0
Nuclei
http/cves/2026/CVE-2026-114509.yaml
1
PoC en GitHub
ArioVeisa/cve-2026-114509-laravel-tokenguard · Nguemoue/project2026_20261030_tokengate · Nxploited/CVE-2026-114509 · dimasma0305/CVE-2026-114509 · hakaioffsec/CVE-2026-114509-PoC · nextmend/laravel-type-juggling-auth-bypass …
7
Ver los 7 repositorios de GitHub (1 con exploit confirmado)
ArioVeisa/cve-2026-114509-laravel-tokenguard
Nguemoue/project2026_20261030_tokengateexploit
Nxploited/CVE-2026-114509
dimasma0305/CVE-2026-114509
hakaioffsec/CVE-2026-114509-PoC
nextmend/laravel-type-juggling-auth-bypass
tajulasri/-CVE-2026-114509-POC

Los repositorios públicos incluyen exploits, escáneres, laboratorios y reglas de detección. No ejecute código de terceros sin revisarlo en un entorno aislado.

Referencias
Fabricantehttps://github.com/laravel/framework/security/advisories/GHSA-f9x3-7vq9-cph6
Exploithttps://github.com/projectdiscovery/nuclei-templates/blob/main/http/cves/2026/CVE-2026-114509.yaml
Exploithttps://github.com/ArioVeisa/cve-2026-114509-laravel-tokenguard
Exploithttps://github.com/Nguemoue/project2026_20261030_tokengate
Exploithttps://github.com/Nxploited/CVE-2026-114509
Exploithttps://github.com/dimasma0305/CVE-2026-114509
Exploithttps://github.com/hakaioffsec/CVE-2026-114509-PoC
Exploithttps://github.com/nextmend/laravel-type-juggling-auth-bypass
Exploithttps://github.com/tajulasri/-CVE-2026-114509-POC
Exploithttps://github.com/mehmet-emir-eroglu/CVE-2026-114509
Otrahttps://github.com/laravel/framework/commit/8dbb08bccac1be095dba4a9d259a419620f1e8a5
Otrahttps://github.com/laravel/framework/commit/9b21ce0a9bb2b2599978bc0b0df4abea952ad31c
Ver 2 referencias más
Otrahttps://github.com/laravel/framework/releases/tag/v12.68.0
Otrahttps://github.com/laravel/framework/releases/tag/v13.29.0

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.