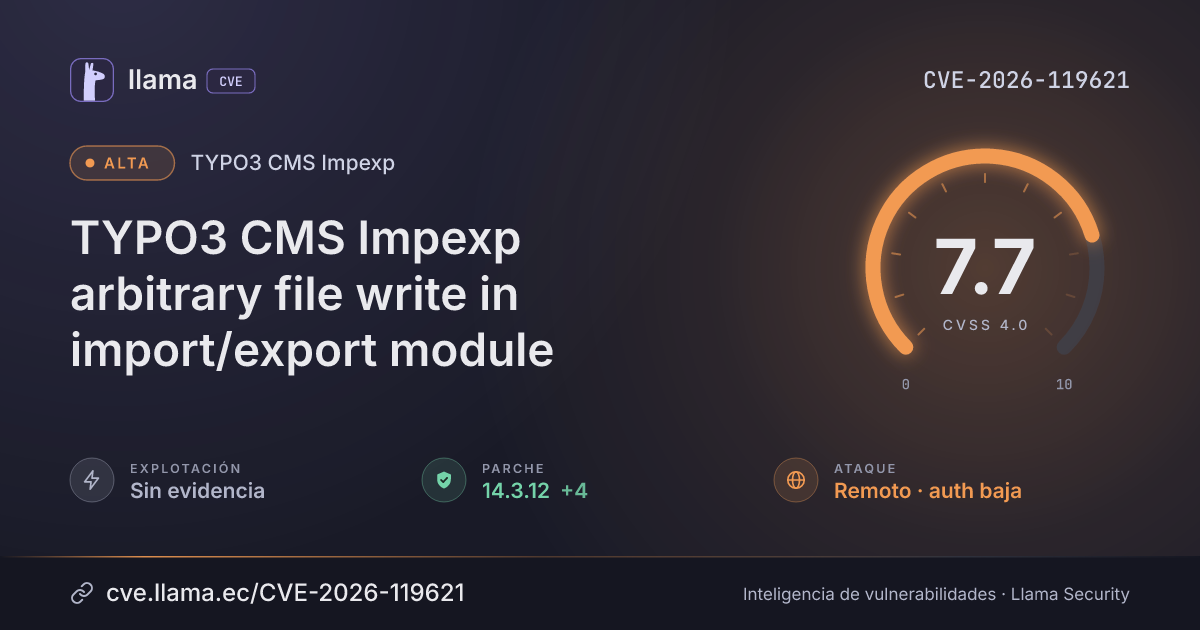
CVE-2026-119621
TYPO3 CMS Impexp arbitrary file write in import/export module
A backend user can upload a crafted file to write arbitrary content to any writable path, like a PHP file.
CVSS:4.0/AV:N/AC:L/AT:P/PR:L/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-119621 divulgada · CVSS 7.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
TYPO3 CMS's Import/Export module has a path traversal flaw that lets a user with a backend login, reached remotely over the network, import a crafted T3D or XML file that writes files with arbitrary content to any location the web server can write to. Such a file, for example a PHP file in the public web root, can lead to remote code execution.
Only affects TYPO3 CMS 10.0.0 through 14.x before the fixed releases when importing T3D or XML files in the Import/Export module, which requires an admin backend account. Fixed in 14.3.12, 13.4.40, 12.4.52, 11.5.57 and 10.4.63.
Descripción original del registro (TYPO3)
When importing a T3D or XML file in the Import/Export module, the file hash values of imported files were taken from the import data without validation and used to build the path of a temporary file. A crafted import file could therefore write files with arbitrary content to any location writable by the web server, for example a PHP file in the public web root, which leads to remote code execution. Exploiting this vulnerability requires an administrator backend user account, or a non-admin backend user for whom importing has been enabled via the user TSconfig option options.impexp.enableImportForNonAdminUser.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
typo3/cms-impexp |
Corregida | 10.4.63, 11.5.57, 12.4.52, 13.4.40, 14.3.12 | — | — |
10.4.6311.5.5712.4.5213.4.4014.3.12Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://news.typo3.com/security/advisory/typo3-core-sa-2026-025https://github.com/TYPO3/typo3/commit/365c39a4168f98a5e93bc1cb08a130894fcb8385https://github.com/TYPO3/typo3/commit/1f950ddbea861d6775e3074427f82683bdbec2d5https://github.com/TYPO3/typo3/commit/db74f64bd64770bd9b8c94e8aea0b633447167aeLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.