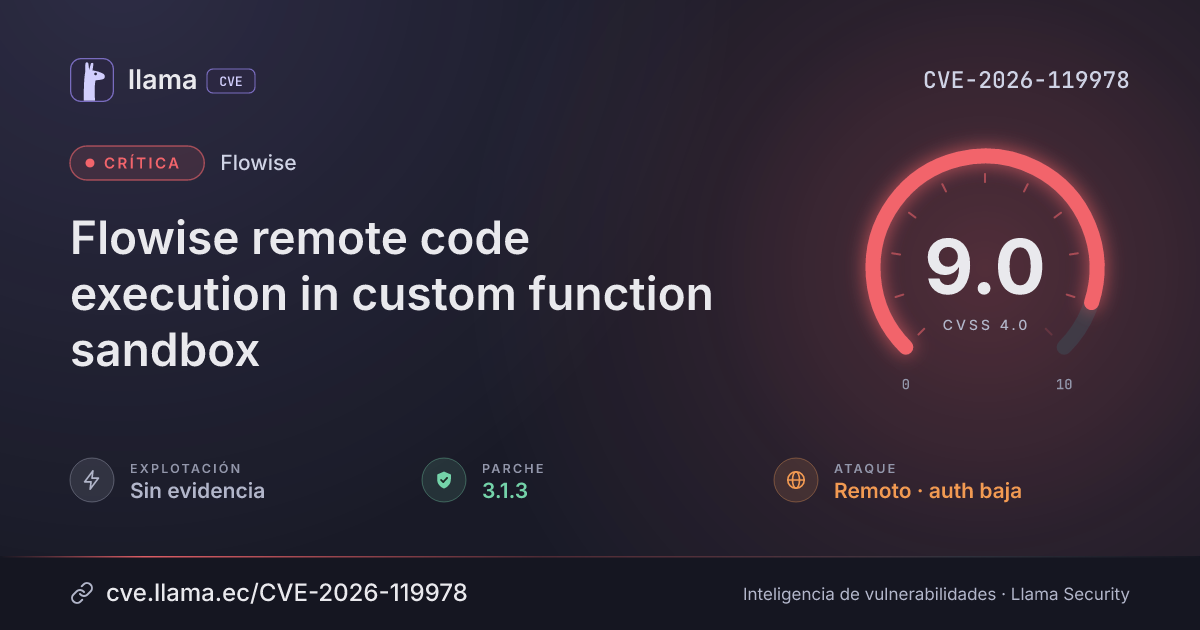
CVE-2026-119978
Flowise remote code execution in custom function sandbox
An authenticated user can break out of the sandbox and run system commands on the server.
CVSS:4.0/AV:N/AC:L/AT:P/PR:L/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.1.3 | flowise · -127 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-119978 divulgada · CVSS 9 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Flowise, an open-source platform for building AI workflows, is affected through version 3.1.4. An authenticated user can exploit its custom function sandbox to run arbitrary operating system commands on the server with the Flowise process's privileges, potentially giving full control over the host.
Descripción original del registro (VulnCheck)
Flowise through 3.1.4 contains a sandbox escape vulnerability that allows authenticated users to execute OS commands by abusing allowlisted langchain and mammoth modules when ALLOW_BUILTIN_DEP=true. Attackers can submit JavaScript to /api/v1/node-custom-function that writes a file into the mammoth package via LocalFileStore and requires it, escaping vm2 as the Flowise process user.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmflowise |
Corregida | 3.1.3 | -127 d | 3.1.4 no afectada |
npmflowise-components |
Corregida | 3.1.3 | -127 d | 3.1.4 no afectada |
3.1.3Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/soovwv/cve/blob/a37354aff1e78c0601772e7716f5318c473e8640/CVE-2026-119978.mdhttps://github.com/FlowiseAI/Flowise/blob/a65f81bb43ef66d3ce734bf0dff4223ae8041c95/packages/components/src/utils.ts#L55-L114https://github.com/FlowiseAI/Flowise/blob/a65f81bb43ef66d3ce734bf0dff4223ae8041c95/packages/components/src/utils.ts#L1733https://github.com/advisories/GHSA-9gvv-qjj3-2p6ghttps://github.com/FlowiseAI/Flowisehttps://www.vulncheck.com/advisories/flowise-through-3.1.4-custom-function-sandbox-escape-rce-via-localfilestoreLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.