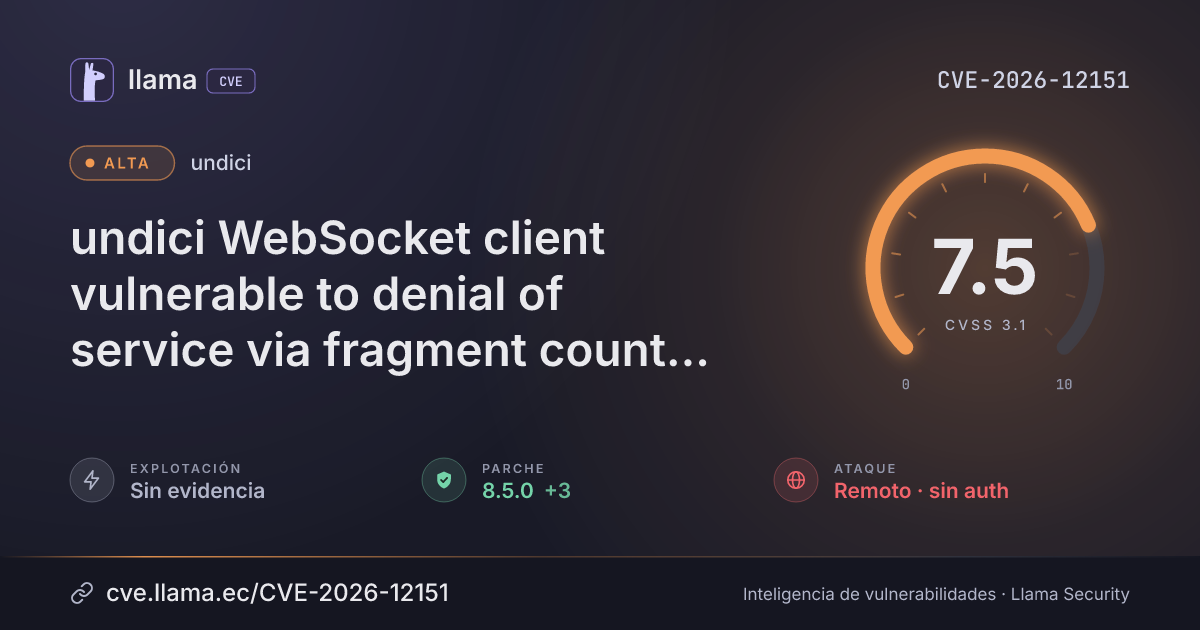
CVE-2026-12151
undici WebSocket client vulnerable to denial of service via fragment count bypass
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H
Fuente: CNA
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:HCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 6.27.0 | undici · -2 d desde divulgación | |
| Remediación | Parche 7.28.0 | undici · -2 d desde divulgación | |
| Remediación | Parche 8.5.0 | undici · -2 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-12151 divulgada · CVSS 7.5 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Impact: The undici WebSocket client enforces maxPayloadSize on the cumulative byte count of fragments in a message but does not enforce a limit on the number of fragments. A malicious WebSocket server can stream many small or empty continuation frames that each pass per-frame and cumulative-size validation, collectively causing unbounded memory growth in the client process. The result is memory exhaustion and a denial of service. Affected applications are those using the undici WebSocket client (new WebSocket(...)) or the WebSocketStream API that can be induced to connect to an attacker-controlled or compromised WebSocket endpoint. All releases starting at undici 6.17.0 are affected. Patches: Upgrade to undici >= 6.26.0, >= 7.28.0, or >= 8.5.0. Workarounds: No workaround is available. The fix must be applied through an upgrade.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmundici |
Corregida | 6.27.0, 7.28.0, 8.5.0 | -2 d · -2 d · -2 d | 8.12.4 no afectada |
6.26.06.27.07.28.08.5.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://access.redhat.com/errata/RHSA-2026:48151https://access.redhat.com/errata/RHSA-2026:39246https://access.redhat.com/errata/RHSA-2026:35842https://access.redhat.com/errata/RHSA-2026:35841https://access.redhat.com/errata/RHSA-2026:41947https://access.redhat.com/errata/RHSA-2026:39868https://access.redhat.com/errata/RHSA-2026:52399https://github.com/nodejs/undici/security/advisories/GHSA-vxpw-j846-p89qhttps://bugzilla.redhat.com/show_bug.cgi?id=2489980https://cna.openjsf.org/security-advisories.htmlhttps://access.redhat.com/security/cve/CVE-2026-12151https://security.access.redhat.com/data/csaf/v2/vex/2026/cve-2026-12151.jsonLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.