llamaCVEVulnerability Intelligence
/
Zebra

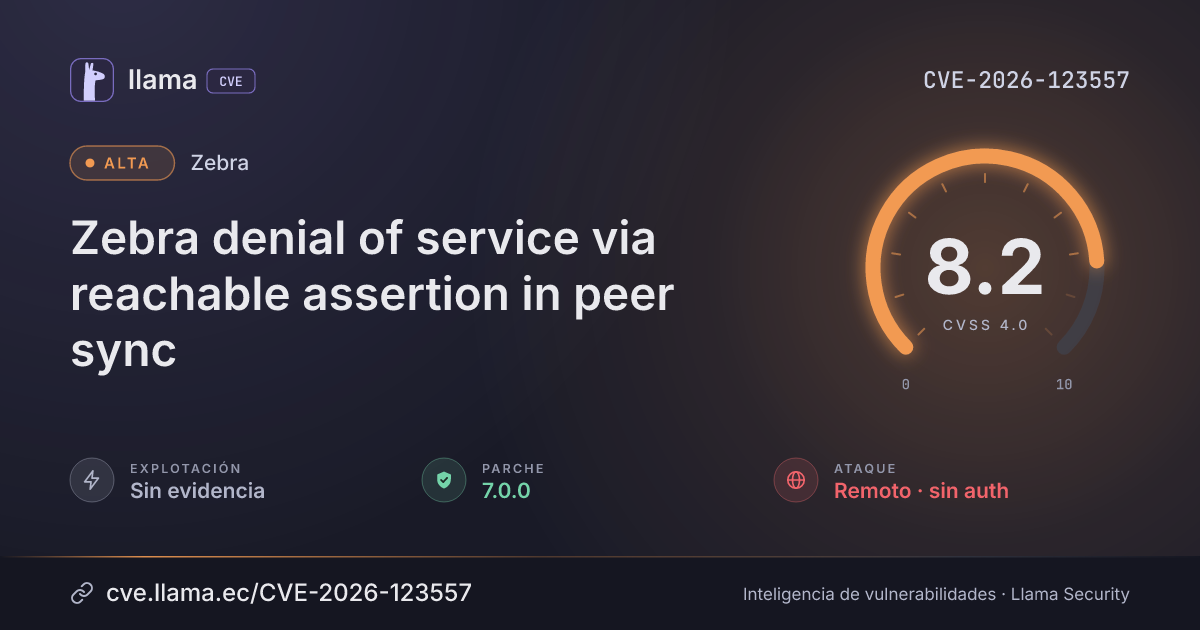
CVE-2026-123557

Zebra denial of service via reachable assertion in peer sync

Unauthenticated remote peers can crash syncing nodes by disconnecting while a block send is stalled.

Default setupsParche disponiblereachable assertion
Descargar PNG JSON
CVSS 4.0
8.2
Alta
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche1 versión7.0.0
Exposición11 dDesde la divulgación, 7 nov 2026, 8:37 p. m.
Detección6 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir
Remediar en la ventana regular de mantenimiento
Sin explotación conocida, no automatizable e impacto técnico parcial. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada +1
Fuente: ENISA EUVD +1
Verificada
8 nov 26
10 nov 26
16 nov 26
19 nov 26
8 nov 26
10 nov 26
13 nov 26
16 nov 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-123557 divulgada · CVSS 8.2 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Monitoreo Fuente: OSV Registro visto por primera vez en OSV
Monitoreo Verificada Última verificación contra las fuentes
Resumen

ZcashFoundation Zebra zebrad before 7.0.0 contains a reachable assertion race condition that allows unauthenticated remote peers to abort the node by triggering disconnection during a blocked outbound send. Malicious peers can return empty FindBlocks or FindHeaders replies and stop reading their socket, dropping an unresolved MustUseClientResponseSender and terminating syncing nodes.

Affects zebrad 6.4.2 and earlier, and 7.0.0-rc.0, on release builds that talk to untrusted P2P peers. CVSS 8.2 is the only rating given. Fixed in zebrad 7.0.0.

¿Qué significa?A peer disconnection can trigger a reachable assertion in zebrad. Because release builds abort the process on panic, a successful trigger terminates the whole node until it is restarted.
¿Quién está afectado?Versions zebrad 6.4.2 and earlier, and 7.0.0-rc.0, are affected. The trigger applies on a release build, such as published binaries and Docker images, while the node accepts or makes P2P connections to untrusted peers, which is the default, and while it is syncing more than 1,000 blocks behind the network tip. Check the running version and whether the node is still catching up to the tip.
¿Qué hacer?Upgrade to zebrad 7.0.0 or later, which contains the fix.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Running zebrad 6.4.2 or earlier, or 7.0.0-rc.0.“You run zebrad 6.4.2 or earlier, or 7.0.0-rc.0.”
02
Release build, which aborts the process on panic.“You run a release build (the default for published binaries and Docker images), which aborts the process on panic.”
03
Node accepts or makes P2P connections to untrusted peers.“Your node accepts or makes P2P connections to untrusted peers (the default).”
04
Node is syncing, more than 1,000 blocks behind the network tip.“The confirmed trigger applies while the node is syncing (more than 1,000 blocks behind the network tip).”
MitigaciónRun zebrad under a process supervisor with automatic restart to limit the outage if the process aborts.
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:H
BajaAlta
Requisitos de ataqueAT:P
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:N
AltoBajoNinguno
Integridad (sistema)VI:N
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
zebra< 7.0.0
7.0.0
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
zebra
Corregida 7.0.0 — —
Versiones corregidas7.0.0
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/ZcashFoundation/zebra/security/advisories/GHSA-6v36-c42v-v98p
Otrahttps://www.vulncheck.com/advisories/zebra-zebrad-before-7.0.0-reachable-assertion-dos-via-peer-disconnection

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.