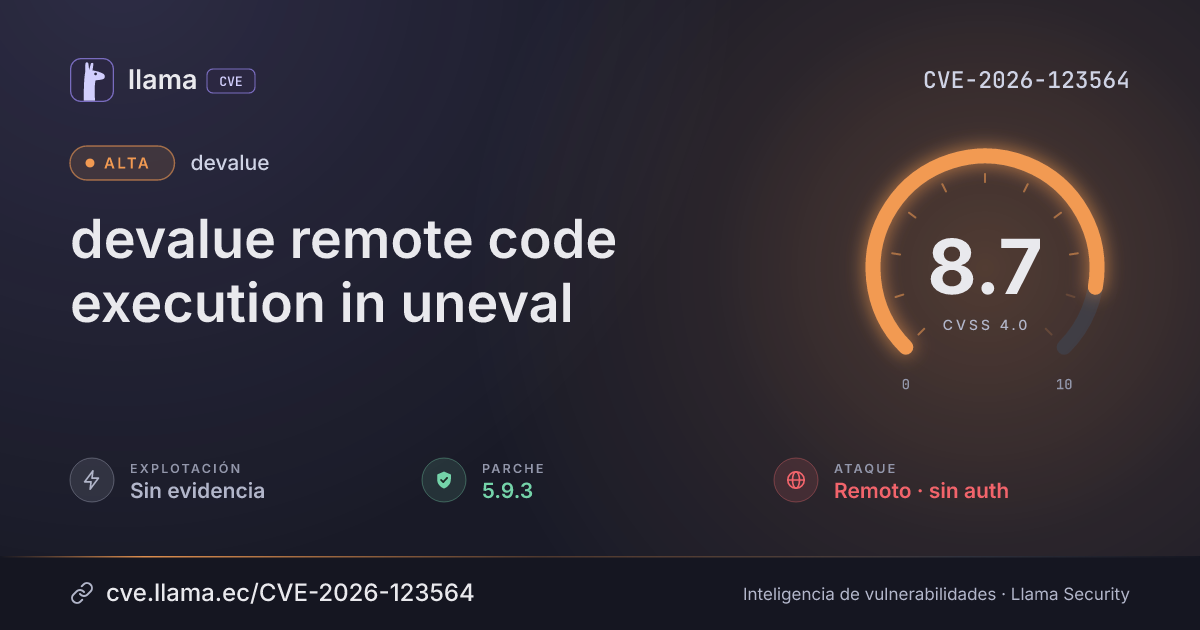
CVE-2026-123564
devalue remote code execution in uneval
Attackers who can shape a large sparse array an app serializes can exhaust memory when the output is evaluated.
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 5.9.3 | devalue · -51 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-123564 divulgada · CVSS 8.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Sveltejs devalue from 1.0.0 before 5.9.3 contains a memory exhaustion flaw in uneval, whose generated code for sparse arrays allocates memory proportional to the array's declared length when evaluated. Attackers who can influence a very large sparse array serialized by an application can exhaust memory in the browser or runtime evaluating the output.
Affects devalue 1.0.0 through 5.9.2 when uneval serializes very large sparse arrays that are then evaluated. Fixed in 5.9.3.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmdevalue |
Corregida | 5.9.3 | -51 d | 6.0.3 no afectada |
5.9.3Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/sveltejs/devalue/security/advisories/GHSA-wf3x-273g-mvxvhttps://www.vulncheck.com/advisories/sveltejs-devalue-before-5.9.3-memory-exhaustion-via-uneval-sparse-arraysLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.