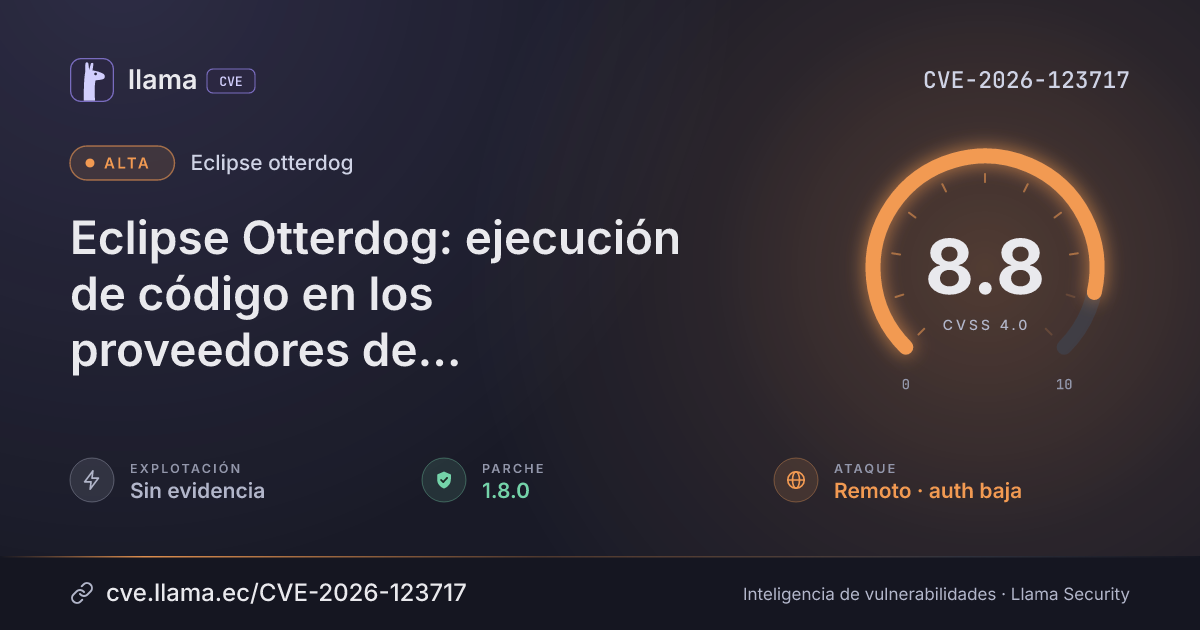
CVE-2026-123717
Eclipse otterdog code execution in pass and bitwarden credential providers
A user who can edit a configuration can run commands as the operator and access their credential vault.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:P/PR:L/UI:A/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-123717 divulgada · CVSS 8.8 (CNA) | |
| Remediación | Parche 1.8.0 | otterdog · 0 d desde divulgación | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
OS command injection in the pass and bitwarden credential providers of Eclipse Otterdog lets a user who can modify an organization configuration run arbitrary commands with the privileges of the operator running otterdog, including access to their credential vault. The attack is carried out remotely through a crafted secret reference or credential identifier that is resolved when "otterdog apply" runs, and it requires low-privilege login and some user action.
Descripción original del registro (eclipse)
OS command injection in the pass and bitwarden credential providers in Eclipse Foundation Eclipse Otterdog through 1.7.1 allows a user able to modify an organization configuration to execute arbitrary commands with the privileges of the operator running otterdog, including access to their credential vault, via a crafted secret reference (pass:<path> or bitwarden:<item>@<field>) or credential identifier that is resolved when otterdog apply is run.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypiotterdog |
Corregida | 1.8.0 | 0 d | 1.8.0 no afectada |
1.8.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/eclipse-csi/otterdog/security/advisories/GHSA-886p-g538-rcmphttps://gitlab.eclipse.org/security/cve-assignment/-/work_items/552https://github.com/eclipse-csi/otterdog/releases/tag/v1.8.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.