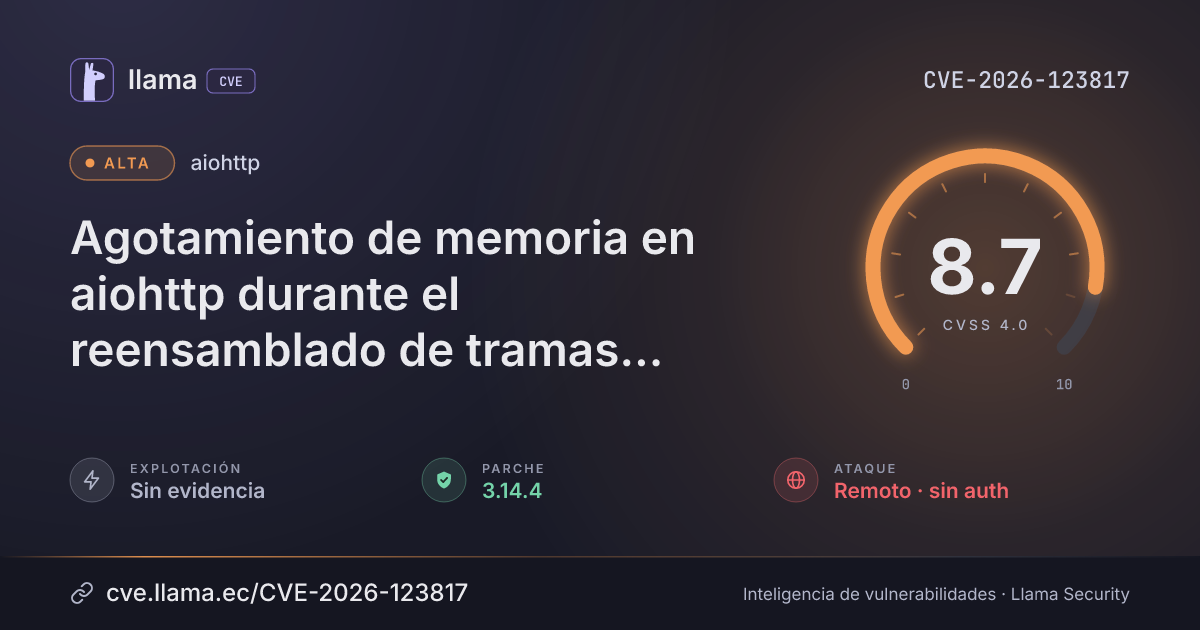
CVE-2026-123817
aiohttp memory exhaustion in WebSocket frame reassembly
An unauthenticated remote attacker can exhaust memory by sending a WebSocket frame split into tiny reads.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:HCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.14.4 | aiohttp · -35 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-123817 divulgada · CVSS 8.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
AIOHTTP, an asynchronous HTTP client and server framework for Python, can be made to consume excessive memory through its WebSocket frame reassembly, which can lead to denial of service. An attacker can trigger this remotely, without logging in, by sending a frame split into many tiny reads.
Descripción original del registro (GitHub_M)
AIOHTTP is an asynchronous HTTP client/server framework for asyncio and Python. Prior to 3.14.4, the WebSocket reader retains one bytes object for each transport read while reassembling an incomplete frame. A malicious peer can split a frame into many tiny reads so per-object overhead substantially exceeds the payload bytes allowed by max_msg_size. The condition affects a server receiving frames from a malicious client and a client receiving frames from a malicious server, and can cause excessive memory consumption or denial of service. This issue is fixed in version 3.14.4.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypiaiohttp |
Corregida | 3.14.4 | -35 d | 3.14.5 no afectada |
3.14.4Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/aio-libs/aiohttp/security/advisories/GHSA-2g87-pp6c-29x5https://github.com/aio-libs/aiohttp/pull/13352https://github.com/aio-libs/aiohttp/pull/13612https://github.com/aio-libs/aiohttp/commit/09bcaa73ff084a0c539bbf16a0a78743acb7141fhttps://github.com/aio-libs/aiohttp/commit/6a4f6682817839313b04b8e5cea2b39c1a88ab4fhttps://github.com/aio-libs/aiohttp/releases/tag/v3.14.4Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.