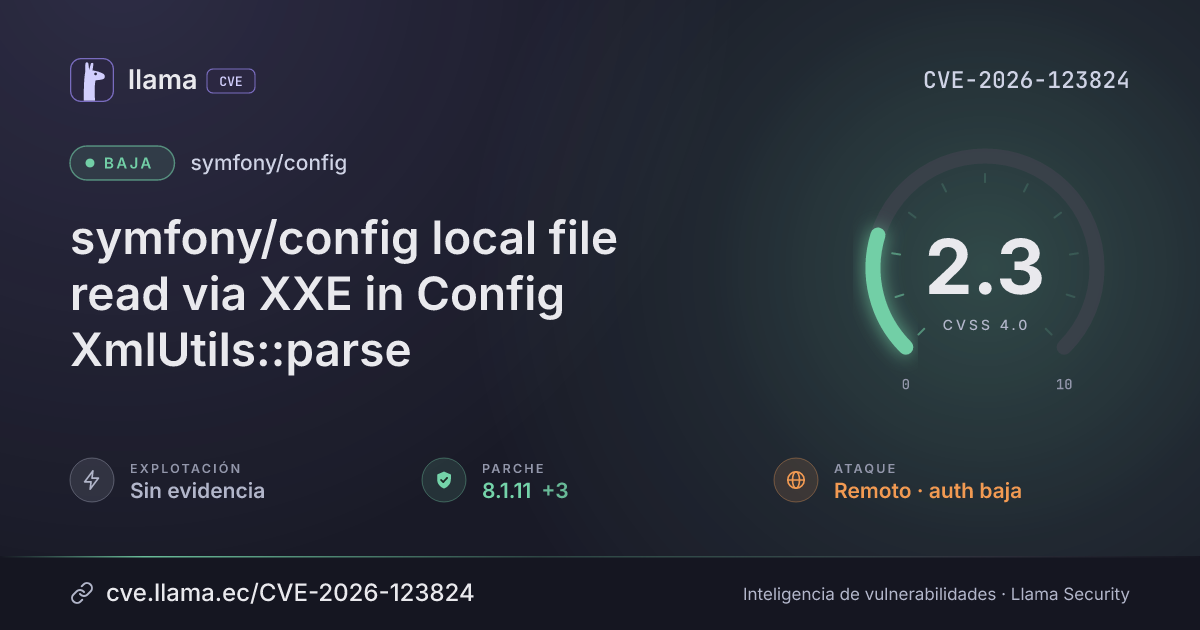
CVE-2026-123824
symfony/config local file read via XXE in Config XmlUtils::parse
A low-privilege remote attacker can probe for local files, cause denial of service, and sometimes leak file contents.
CVSS:4.0/AV:N/AC:L/AT:P/PR:L/UI:N/VC:L/VI:L/VA:L/SC:N/SI:N/SA:N
Fuente: CNA
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:LCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-123824 divulgada · CVSS 2.3 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Symfony's Config component, through its `XmlUtils::parse()` method, lets a remote attacker with low-privilege login determine whether local files exist and cause a denial of service through XML external entity injection, in applications that pass untrusted XML to that method. In some configurations, the attacker can also send local file contents to an external server.
Descripción original del registro (Checkmarx)
The Symfony Config component XmlUtils::parse() enables DTD validation before rejecting documents that carry a doctype, allowing XML external entity (XXE) injection in Symfony versions prior to 5.4.56, 6.x prior to 6.4.50, 7.x prior to 7.4.23, and 8.x prior to 8.1.11. A remote attacker who can supply XML to this method can determine whether local files exist, cause a denial of service, and, in some configurations, exfiltrate local file content via a crafted XML document whose doctype declares an external file:// entity. XmlUtils::parse() sets $dom->validateOnParse = true before calling loadXML() and only rejects documents carrying a doctype afterwards. Enabling DTD validation makes libxml resolve external entities during loadXML(), and LIBXML_NONET blocks http:// but not file://, so a file:// entity is read from disk before the doctype rejection runs. The content of the file is not returned to the caller, but the distinct libxml error for a missing path reveals whether a file exists, and an entity pointing at a large or slow file causes a denial of service. If the application registers a network-capable stream wrapper such as s3://, a parameter entity can also send the content of a local file to an external server. This is the same issue as CVE-2026-45071, which was fixed in the DomCrawler component but not in Config. Applications are affected if they pass untrusted XML to XmlUtils::parse() directly. The Symfony components that call it process developer-provided or operator-configured sources, such as configuration files and the XLIFF documents fetched by the translation providers.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
symfony/config |
Corregida | 5.4.56, 6.4.50, 7.4.23, 8.1.11 | — | — |
5.4.566.4.507.4.238.1.11Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/symfony/symfony/security/advisories/GHSA-5jff-8h8q-r5qxhttps://github.com/symfony/symfony/commit/334ef21a6039355c05b123e7df60699be0e28da3Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.