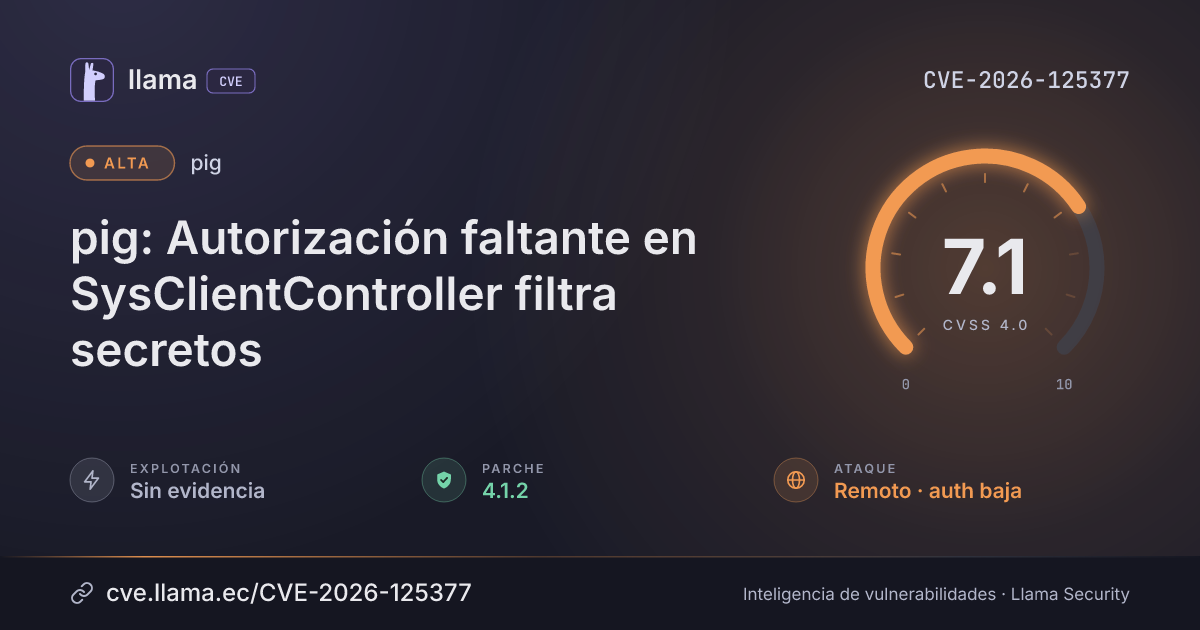
CVE-2026-125377
pig Missing authorization in SysClientController leaks secrets
A signed-in user without client permissions can read OAuth2 client secrets and use them to get tokens.
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-125377 divulgada · CVSS 7.1 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Pig before 4.1.2 contains a missing authorization vulnerability in SysClientController that allows authenticated users without client-management permission to retrieve OAuth2 client secrets via GET /client/{clientId} and GET /client/export. Attackers can fetch clientSecret values for seed clients like pig, app, and daemon or export the client table, then obtain tokens using those clients' configured grant types.
Only affects Pig versions before 4.1.2 (pig-mesh pig, Maven), where authenticated users without client-management permission can retrieve OAuth2 client secrets. Fixed in 4.1.2.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
com.pig4cloud:pig |
Corregida | 4.1.2 | — | — |
4.1.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/pig-mesh/pig/commit/0fffbf14d393f30a0272a3cdf0a54efd45e0d9e3https://github.com/pig-mesh/pig/issues/1298https://github.com/pig-mesh/pighttps://github.com/pig-mesh/pig/blob/a0d273afd3adc6678b065c0f2d25433541343ad7/pig-upms/pig-upms-biz/src/main/java/com/pig4cloud/pig/admin/controller/SysClientController.java#L69-L82https://github.com/pig-mesh/pig/releases/tag/v4.1.2https://www.vulncheck.com/advisories/pig-before-4.1.2-missing-authorization-exposes-oauth2-client-secrets-via-clientLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.