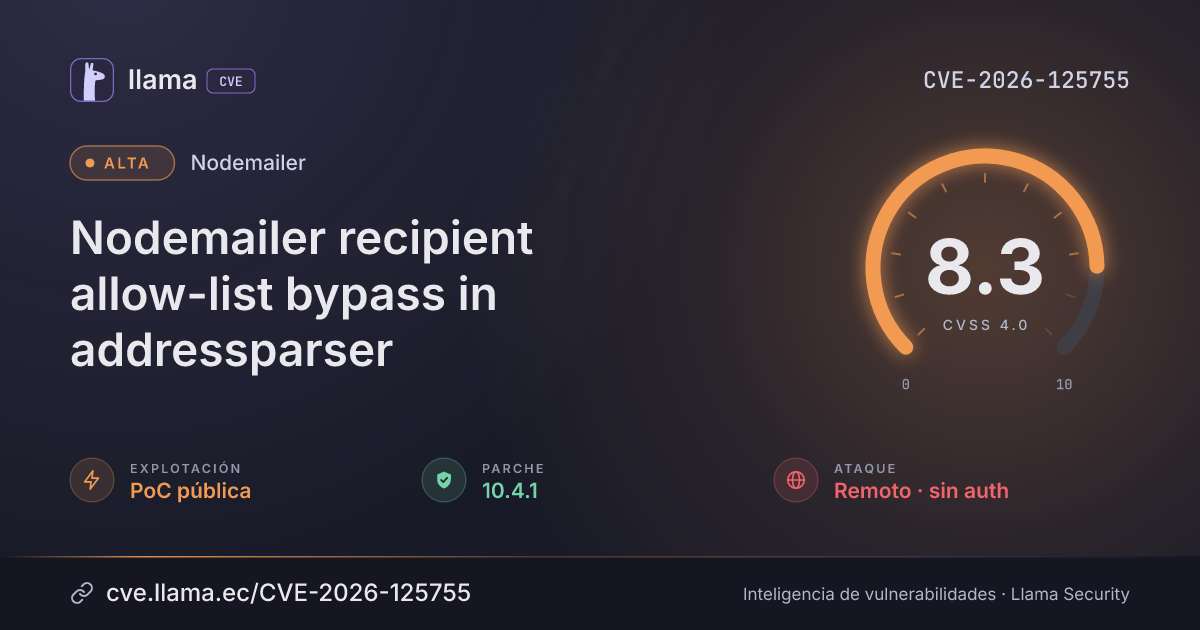
CVE-2026-125755
Nodemailer recipient allow-list bypass in addressparser
Attackers can send mail from the app's sender identity to arbitrary addresses outside allowed domains.
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:L/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-125755 divulgada · CVSS 8.3 (CNA) | |
| Remediación | Parche 10.4.1 | nodemailer · 0 d desde divulgación | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación PoC pública | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Nodemailer 3.0.0 before 10.4.1 contains an address parsing flaw in addressparser that truncates domains at folding whitespace or comments before a dot, allowing attackers to bypass recipient domain restrictions. Attackers can submit crafted to, cc, bcc or replyTo addresses that pass RFC 5322 domain checks but deliver mail to an attacker-chosen address under the application's sender identity.
Affects Nodemailer 3.0.0 up to but not including 10.4.1 when an app validates recipient addresses with something other than Nodemailer's parser and passes the raw strings to to, cc, bcc or replyTo. Fixed in 10.4.1.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmnodemailer |
Corregida | 10.4.1 | 0 d | 10.6.0 no afectada |
10.4.1Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/nodemailer/nodemailer/security/advisories/GHSA-3q53-mvfw-q9v8https://github.com/nodemailer/nodemailer/commit/c2b9c41bb81b2294ebadd294ad15ff035a17d0a5https://github.com/nodemailer/nodemailer/releases/tag/v10.4.1https://github.com/nodemailer/nodemailer/blob/3b5cf1eec32c81f287870c8a1c9c09640062cfd5/src/addressparser/index.ts#L330-L345https://www.vulncheck.com/advisories/nodemailer-3.0.0-before-10.4.1-recipient-allow-list-bypass-via-addressparserLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.