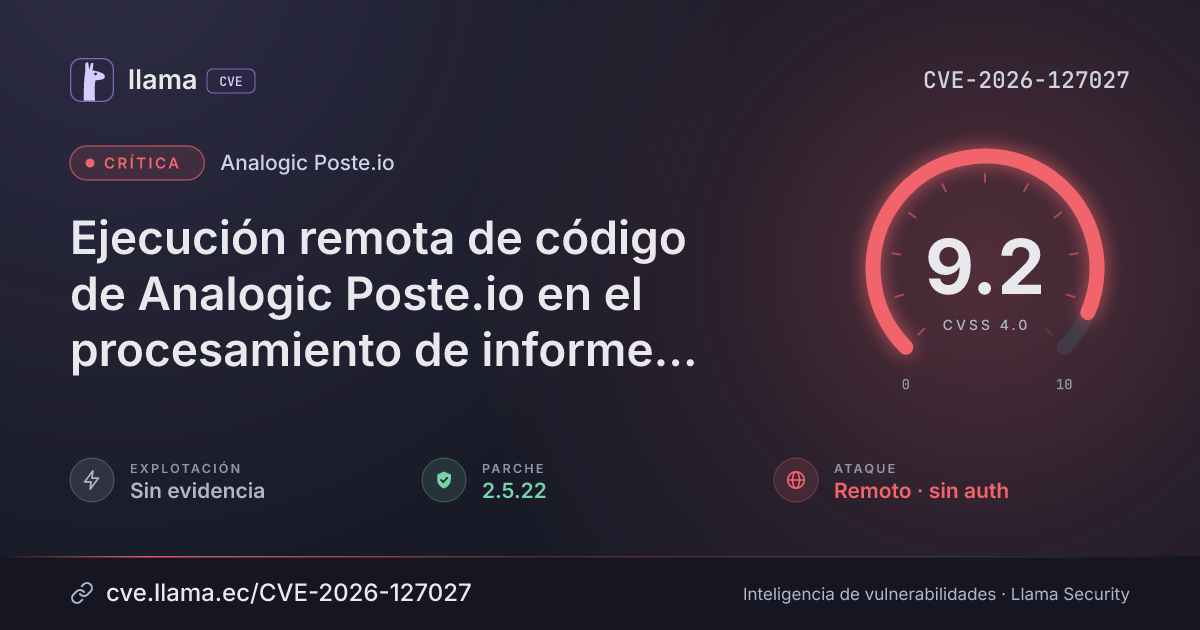
CVE-2026-127027
Analogic Poste.io remote code execution in DMARC report processing
Without logging in, an attacker can run commands as root by emailing crafted attachments to the DMARC address.
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-127027 divulgada · CVSS 9.2 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Poste.io, made by Analogic, has a remote code execution flaw in how it processes DMARC reports. A remote attacker who can send email to the server on port 25 can run arbitrary commands as root inside the Poste.io container, without logging in and with no user action needed, by sending crafted attachments to the DMARC reports address.
Poste.io versions before 2.5.22 are affected, through command injection in DMARC attachment processing. Fixed in 2.5.22.
Descripción original del registro (CERT-PL)
Poste.io is vulnerable to remote code execution in DMARC report processing. Email sent to dmarc-reports@<domain> is saved without sender verification. Script that runs as root unpacks the attachments using unsafe shell commands, allowing command injection through crafted attachments (e.g. file names or archive contents). A remote unauthenticated attacker who can send an email to the server's port 25 can execute arbitrary commands as root within the Poste.io container. This issue was fixed in version 2.5.22.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Poste.io |
Corregida | 2.5.22 | — | — |
2.5.22Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://poste.io/https://cert.pl/en/posts/2026/11/CVE-2026-127027Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.