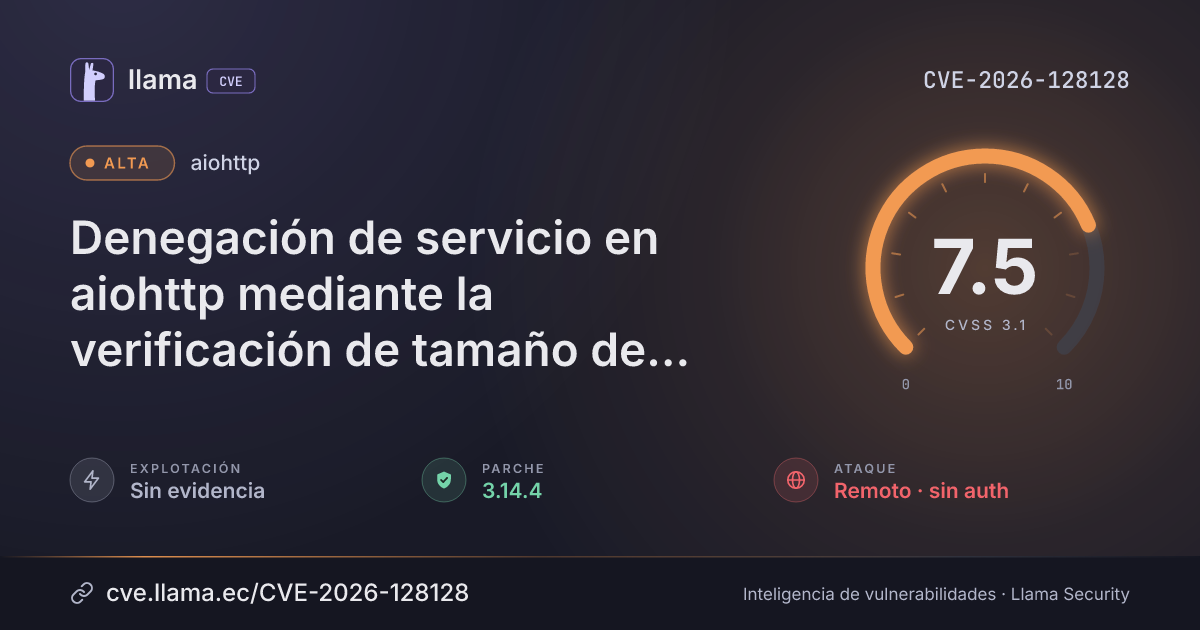
CVE-2026-128128
aiohttp denial of service in WebSocket message size check
Remote attackers can exhaust server memory without logging in by sending a fragmented oversized WebSocket message.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.14.4 | aiohttp · -39 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-128128 divulgada · CVSS 7.5 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
The AIOHTTP WebSocket reader can be made to use unbounded memory, which can exhaust a server's resources and cause a denial of service. A remote attacker can trigger this without logging in by sending a small non-final fragment followed by an oversized message, which bypasses the max_msg_size check through an integer overflow in the C WebSocket reader.
Affects aiohttp versions before 3.14.4 when the C extension WebSocket reader is in use; the Python reader is unaffected. Fixed in 3.14.4.
Descripción original del registro (GitHub_M)
AIOHTTP is an asynchronous HTTP client/server framework for asyncio and Python. Prior to 3.14.4, the C WebSocket reader adds a declared frame length to the size of an already buffered partial message using signed 64-bit arithmetic. A length near two to the power of 63 can overflow, allowing the max_msg_size check to pass. A remote peer can send a small non-final fragment followed by an oversized message and cause unbounded memory consumption. The Python WebSocket reader is unaffected. This issue is fixed in version 3.14.4.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypiaiohttp |
Corregida | 3.14.4 | -39 d | 3.14.5 no afectada |
3.14.4Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/aio-libs/aiohttp/security/advisories/GHSA-3rp8-rxj8-mvjwhttps://github.com/aio-libs/aiohttp/pull/13415https://github.com/aio-libs/aiohttp/pull/13494https://github.com/aio-libs/aiohttp/commit/8c8906a19f64e52ef6a7d44d65217eb3c5af413fhttps://github.com/aio-libs/aiohttp/commit/8cfbe9abe5e11b84006a10f9bdf82bf607671dabhttps://github.com/aio-libs/aiohttp/releases/tag/v3.14.4Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.