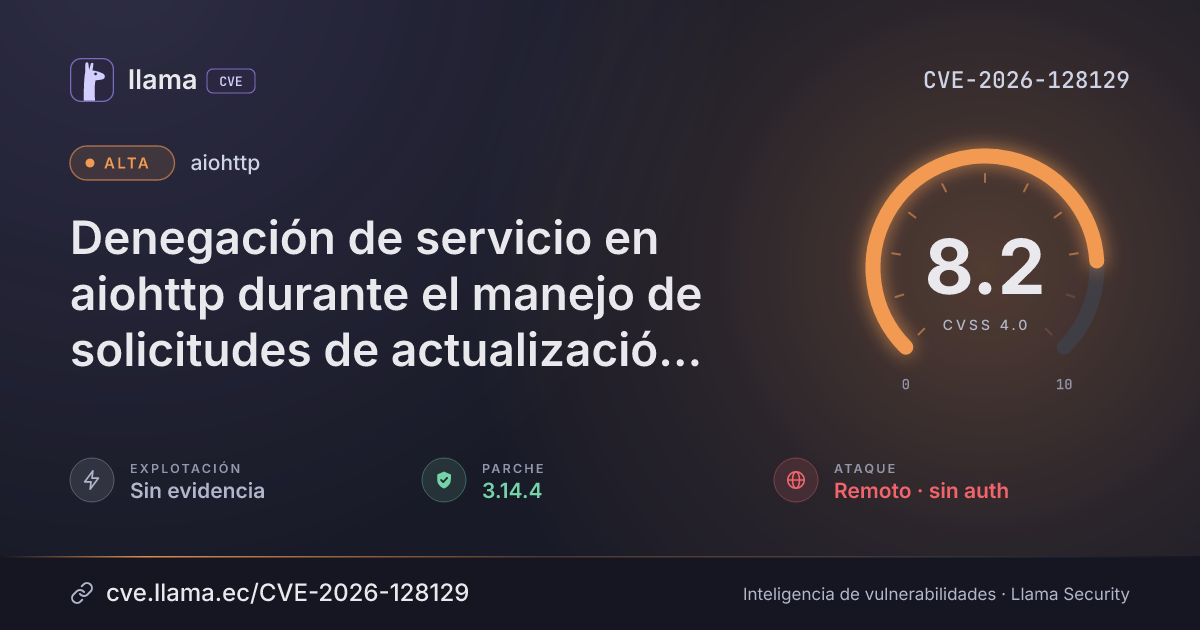
CVE-2026-128129
aiohttp denial of service in HTTP upgrade request handling
A remote attacker can send unlimited data after an upgrade request to exhaust server memory.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.14.4 | aiohttp · -39 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-128129 divulgada · CVSS 8.2 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
AIOHTTP, an asynchronous HTTP client and server framework for Python, buffers unlimited connection data sent after an upgrade request, such as a WebSocket handshake, when a handler has not yet accepted or rejected it. A remote attacker without logging in can send that data over the network to exhaust the server's memory.
Affects aiohttp servers whose handlers do not immediately accept or reject upgrade requests. Fixed in aiohttp 3.14.4.
Descripción original del registro (GitHub_M)
AIOHTTP is an asynchronous HTTP client/server framework for asyncio and Python. Prior to 3.14.4, aiohttp buffers all additional connection data received while a request marked for upgrade, such as a WebSocket handshake, is being handled, without a size limit or flow control. A remote attacker can stream data behind an upgrade request to a handler that does not immediately accept or reject the upgrade and cause unbounded memory consumption. This issue is fixed in version 3.14.4.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypiaiohttp |
Corregida | 3.14.4 | -39 d | 3.14.5 no afectada |
3.14.4Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/aio-libs/aiohttp/security/advisories/GHSA-pw86-h8fm-j323https://github.com/aio-libs/aiohttp/pull/13501https://github.com/aio-libs/aiohttp/pull/13511https://github.com/aio-libs/aiohttp/commit/3d850ee9b92573c7e913821cbcb96005beb3f4dfhttps://github.com/aio-libs/aiohttp/commit/c207cadb257e0959b192ffca0548eca8c71eb96ahttps://github.com/aio-libs/aiohttp/releases/tag/v3.14.4Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.