llamaCVEVulnerability Intelligence
/
PHP

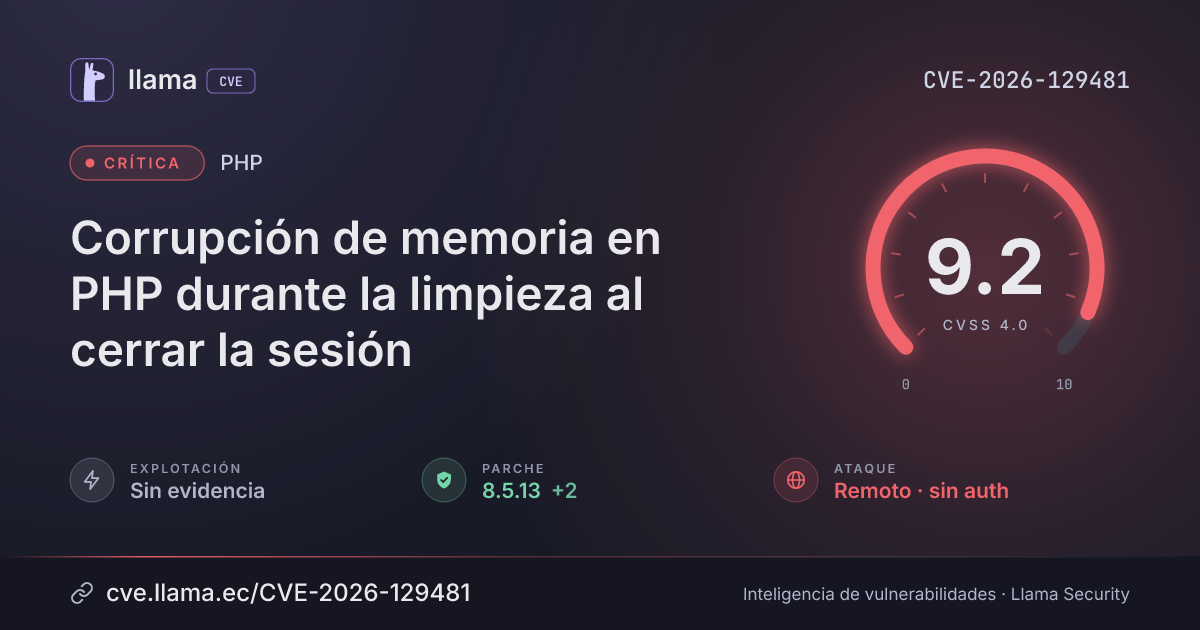
CVE-2026-129481

PHP memory corruption in session shutdown cleanup

A remote attacker could crash a worker or corrupt memory by triggering a failing session cleanup, without logging in.

Texto original en inglés · Ver en español

Crítica · CVSS alto en tecnología listadaUnclearParche disponibleuse-after-free
Descargar PNG JSON
CVSS 4.0
9.2
Crítica
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónSin evidenciaSSVC: ninguna · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche3 versiones8.3.37 · 8.4.28 · 8.5.13
Exposición2 dDesde la divulgación, 19 nov 2026, 9:43 a. m.
Detección7 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir de cerca
Monitorear y programar la remediación
Sin explotación conocida, no automatizable e impacto técnico total. Hay versiones corregidas disponibles.
Huele a exploit funcional. Y yo de olores sé.Se me erizó hasta la manta.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada
Fuente: NIST NVD
Fuente: ENISA EUVD +1
09:43 a. m.
10:25 a. m.
11:22 a. m.
12:19 p. m.
11:57 a. m.
09:43 a. m.
10:17 p. m.
10:50 a. m.
11:24 p. m.
11:57 a. m.
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-129481 divulgada · CVSS 9.2 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 19 nov 2026

PHP's session extension has a use-after-free flaw: if a fatal error occurs in an application callback during session shutdown, a stale pointer to the script filename can later be freed by another request handled by the same worker. An attacker who can trigger such a failing cleanup could crash the worker or corrupt memory, reaching it remotely without logging in, though it only applies when the filename sits in request memory, such as when the script is not cached by OPcache.

Affects PHP 8.3 before 8.3.37, 8.4 before 8.4.28 and 8.5 before 8.5.13 when a session cleanup callback fails fatally and the script filename sits in request memory. Fixed in 8.3.37, 8.4.28 and 8.5.13.

¿Qué significa?If a callback fails fatally during session cleanup, such as stream_close() of a user-defined stream wrapper, session shutdown aborts before a stored filename is released or cleared. A later request handled by the same PHP worker may then corrupt memory or crash that worker.
¿Quién está afectado?PHP 8.3 before 8.3.37, 8.4 before 8.4.28 and 8.5 before 8.5.13 are in range. PHP 8.2 lacks the affected session filename field. The demonstrated setup uses sessions, has OPcache disabled so the filename is in the request heap, and has later requests reaching the same worker. The installed version can be checked with php -v, and OPcache status in the opcache.enable setting.}
¿Qué hacer?Upgrade to the fixed release for the branch in use: PHP 8.3.37, 8.4.28 or 8.5.13 (or later).
Descripción original del registro (php)

Use-after-free after interrupted session shutdown. The session extension records the filename of the executing script when a session starts. If a fatal error occurs in an application callback while the session variables are destroyed at shutdown, such as stream_close() of a user-defined stream wrapper, the pointer is retained after the request memory is freed, and a later request handled by the same worker can free the stale string. An attacker who can trigger such a failing cleanup may crash the worker or corrupt memory; code execution has not been demonstrated. This requires the filename to be allocated in request memory, for example when the script is not cached by OPcache. This issue affects PHP versions 8.3.* before 8.3.37, 8.4.* before 8.4.28 and 8.5.* before 8.5.13.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
PHP 8.3 before 8.3.37, 8.4 before 8.4.28, or 8.5 before 8.5.13 (PHP 8.2 lacks the affected field)“It affects PHP 8.3 and later. PHP 8.2 does not contain the affected session filename field.”
02
Application uses sessions and a callback fails fatally during session cleanup, e.g. stream_close() of a user-defined stream wrapper“A fatal error in such a callback can abort session shutdown before the filename is released or cleared.”
03
Script filename is allocated in request memory, e.g. script not cached by OPcache“The demonstrated configuration has OPcache disabled, so the recorded filename belongs to the request heap.”
04
A later request must be handled by the same worker“The requests must reach the same worker, but they do not need to belong to the same user or session.”
¿Quién debe revisar?Teams running PHP 8.3, 8.4 or 8.5 (e.g. PHP-FPM) with sessions, where scripts run uncached by OPcache and session cleanup callbacks such as stream wrappers can fail fatally.
No protegeEnabling OPcache alone or disabling session upload progress does not fix it.
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:H
BajaAlta
Requisitos de ataqueAT:P
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:H
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
5.1/ 10Medio
Vector 5.1 (moderada) · sin evidencia de explotación.
Versiones

Rangos afectados

Afectada Corregida
PHP≥ 8.3.0 < 8.3.37
PHP≥ 8.4.0 < 8.4.28
PHP≥ 8.5.0 < 8.5.13
8.3.0
8.3.37
8.4.0
8.4.28
8.5.0
8.5.13
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
PHP
Corregida 8.3.37, 8.4.28, 8.5.13 — —
Versiones corregidas8.3.378.4.288.5.13
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALphp
Referencias
Fabricantehttps://github.com/php/php-src/security/advisories/GHSA-g3vh-838c-65v7

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.