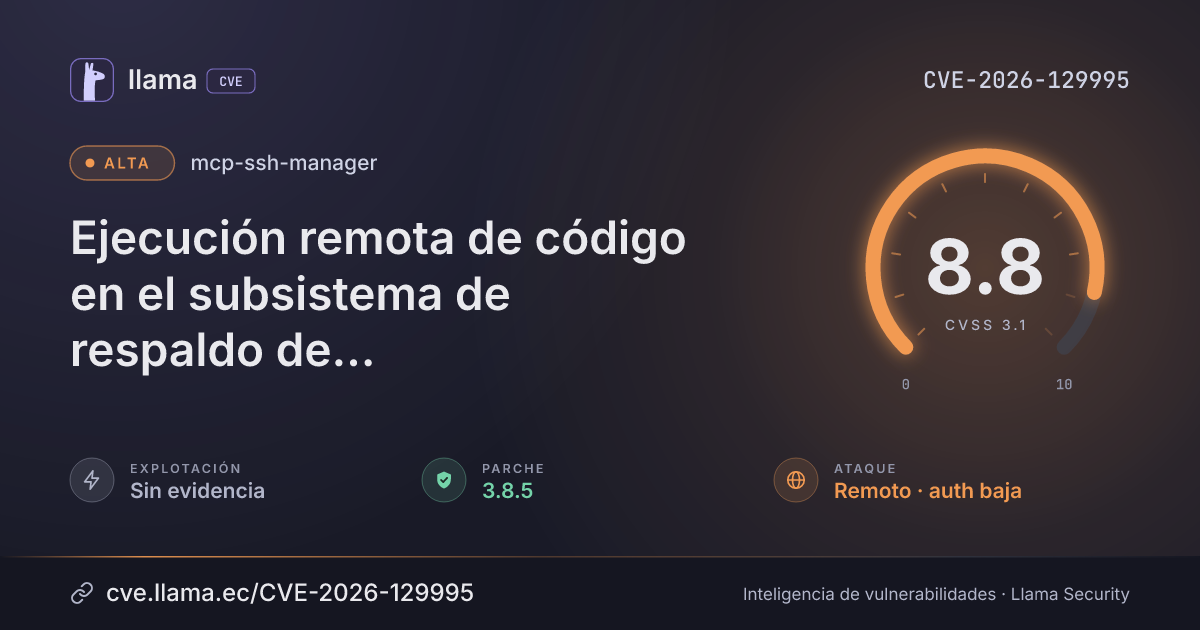
CVE-2026-129995
mcp-ssh-manager remote code execution in backup subsystem
A networked attacker with low-level login can run arbitrary OS commands on remote servers as the SSH user.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-129995 divulgada · CVSS 8.8 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
mcp-ssh-manager from bvisible has a command injection flaw in its backup functions, which pass caller-supplied values into remote shell commands without neutralizing shell metacharacters. An attacker who can reach the server over the network and log in with low-level access can run arbitrary operating system commands on managed remote servers as the configured SSH user.
mcp-ssh-manager versions before 3.8.5 have command injection in the backup subsystem when backup tool arguments carry shell metacharacters. Fixed in 3.8.5.
Descripción original del registro (GitHub_M)
mcp-ssh-manager is an MCP server for managing servers over SSH with human approval, an encrypted vault, and a live audit trail. Prior to 3.8.5, ssh_backup_create, ssh_backup_restore, ssh_backup_schedule, and ssh_backup_list build remote shell commands from caller-controlled values in src/backup-manager.js and inline backup handlers in src/index.js without neutralizing shell metacharacters. Crafted database, connection, backup directory, path, exclusion, schedule, or comment arguments can therefore execute arbitrary OS commands on managed remote servers as the configured SSH user. ssh_backup_schedule can persist execution through cron. ssh_backup_list does not pass through the server policy check and remains available in readonly and restricted modes, allowing command execution despite those restrictions. Tool arguments can be supplied by a malicious or compromised MCP client or steered through indirect prompt injection; fully trusted benign arguments do not trigger the issue. The earlier database-helper remediation for CVE-2026-77383 applied shell quoting to src/database-manager.js but did not cover these parallel backup builders. This issue is fixed in version 3.8.5.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
mcp-ssh-manager |
Corregida | 3.8.5 | — | — |
3.8.5Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/bvisible/mcp-ssh-manager/security/advisories/GHSA-qwwm-vrm9-4mw8https://github.com/bvisible/mcp-ssh-manager/commit/d40daa8a43388dfaedf593bff18f0064d50f9633https://github.com/bvisible/mcp-ssh-manager/releases/tag/v3.8.5Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.