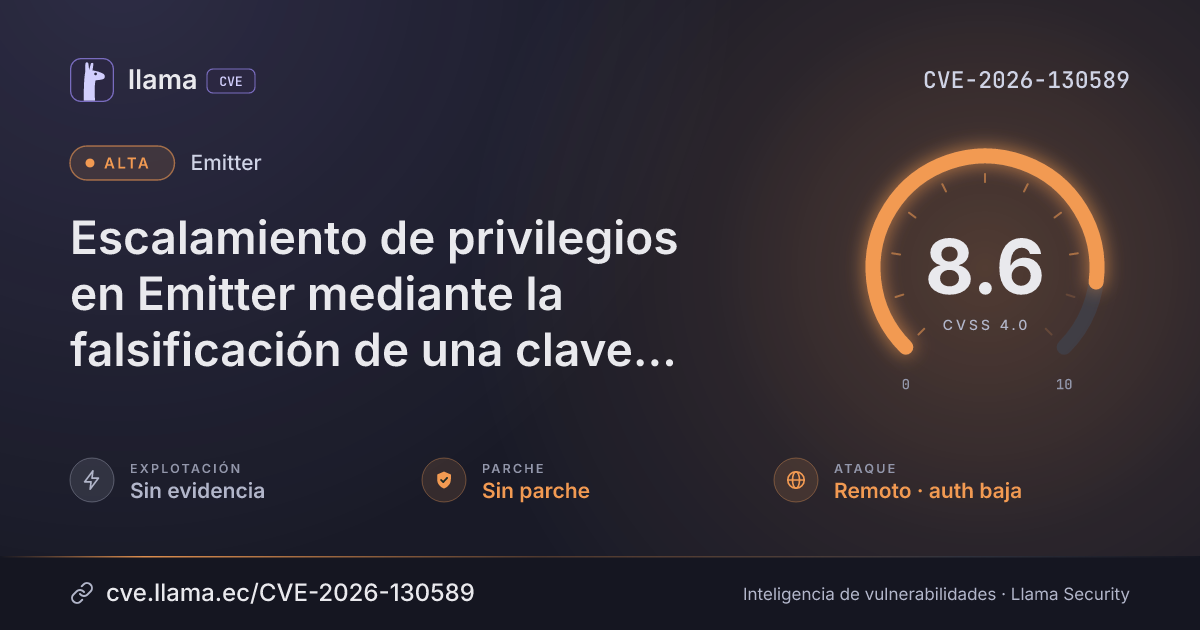
CVE-2026-130589
Emitter privilege escalation via forged master key in keygen
An attacker with one low-privilege channel key can forge a master key and gain permissions on every channel.
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-130589 divulgada · CVSS 8.6 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Emitter from emitter-io has a privilege escalation flaw that lets an attacker who holds a channel key forge a master key. The attacker can then use that key with the keygen service to create keys with arbitrary permissions on every channel in the contract. The attack can be carried out remotely with only a low-privilege channel key.
Affects Emitter 3.1 and earlier, where a channel key holder can forge a master key. CVSS scores it 8.6 (high); no vendor rating or fixed version is given.
Descripción original del registro (VulnCheck)
Emitter through 3.1 contains a privilege escalation vulnerability that allows any channel key holder to forge a master key because channel keys use bare XOR Salsa20 encryption without a MAC or signature. Attackers can flip the permissions byte to the master value and present the forged key to the keygen service to mint keys with arbitrary permissions on every channel of the contract.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gogithub.com/emitter-io/emitter |
Sin parche | — | — | v2.0.437+incompatible afectada |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/emitter-io/emitter/issues/439https://github.com/emitter-io/emitter/blob/v3.1/internal/security/cipher/shuffle.go#L75-L90https://github.com/emitter-io/emitter/blob/v3.1/internal/provider/contract/contract.go#L57-L62https://github.com/emitter-io/emitter/blob/v3.1/internal/service/keygen/keygen.go#L65https://www.vulncheck.com/advisories/emitter-through-3.1-master-key-forgery-via-unauthenticated-channel-key-encryptionLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.