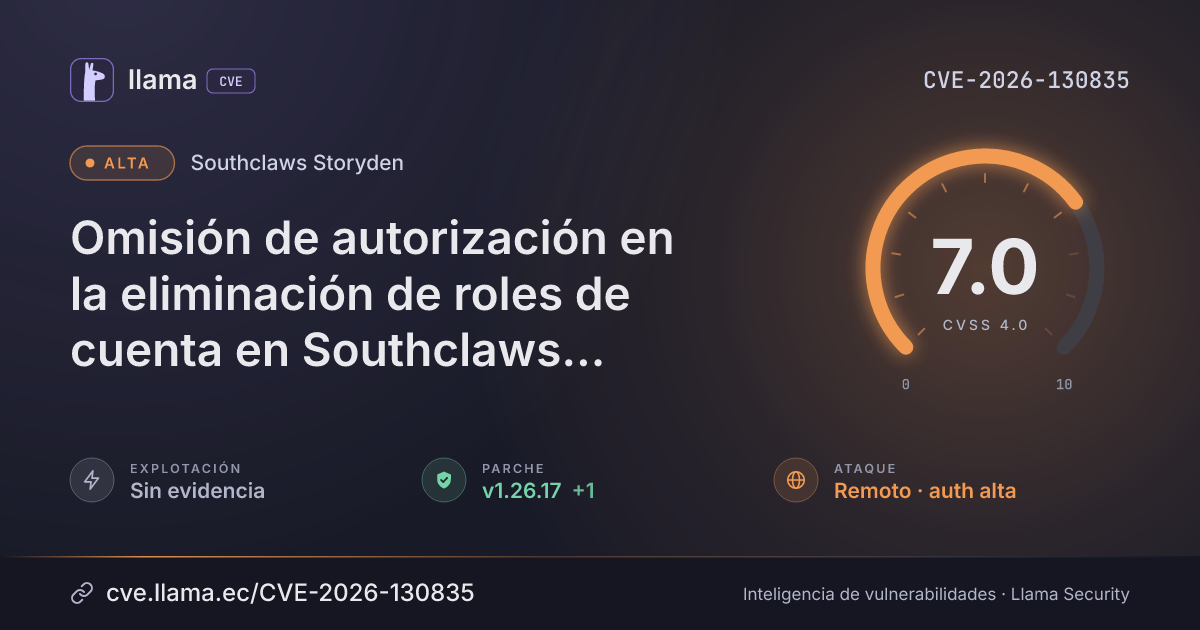
CVE-2026-130835
Southclaws Storyden authorization bypass in account role removal
A non-admin user with the manage roles permission can remotely remove administrator roles from other accounts.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:N/VC:N/VI:H/VA:L/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche v1.26.17 | github.com/Southclaws/storyden · -3 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-130835 divulgada · CVSS 7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Storyden, a forum and community software product, is affected in versions before the fixed release. A user with the MANAGE_ROLES permission, though not an administrator, can remotely remove administrator roles from other accounts by sending requests to the account roles endpoint, which could leave the instance with no administrator.
Storyden 1.26.16 and earlier let any account holding only the MANAGE_ROLES permission remove roles from administrators via the unprotected remove-role endpoint. Fixed in 1.26.17.
Descripción original del registro (VulnCheck)
Storyden before 1.26.17 contains a missing authorization vulnerability in the AccountRemoveRole handler that allows non-administrator users with MANAGE_ROLES to remove administrator roles. Attackers can send DELETE requests to the account roles endpoint to demote other administrators, potentially leaving the instance with no administrator.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gogithub.com/Southclaws/storyden |
Corregida | v1.26.17 | -3 d | v1.26.17 no afectada |
1.26.17v1.26.17Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/Southclaws/storyden/security/advisories/GHSA-c96v-r2gq-g68phttps://github.com/Southclaws/storyden/commit/d4baeb8985798fab11a4cf6516d6bcdc8735e0echttps://github.com/Southclaws/storyden/blob/v1.26.16/app/transports/http/bindings/accounts.go#L644-L684https://github.com/Southclaws/storyden/releases/tag/v1.26.17https://www.vulncheck.com/advisories/storyden-before-1.26.17-missing-authorization-via-accountremoverole-administrator-role-removalLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.