llamaCVEVulnerability Intelligence
/
Mitel MiCollab

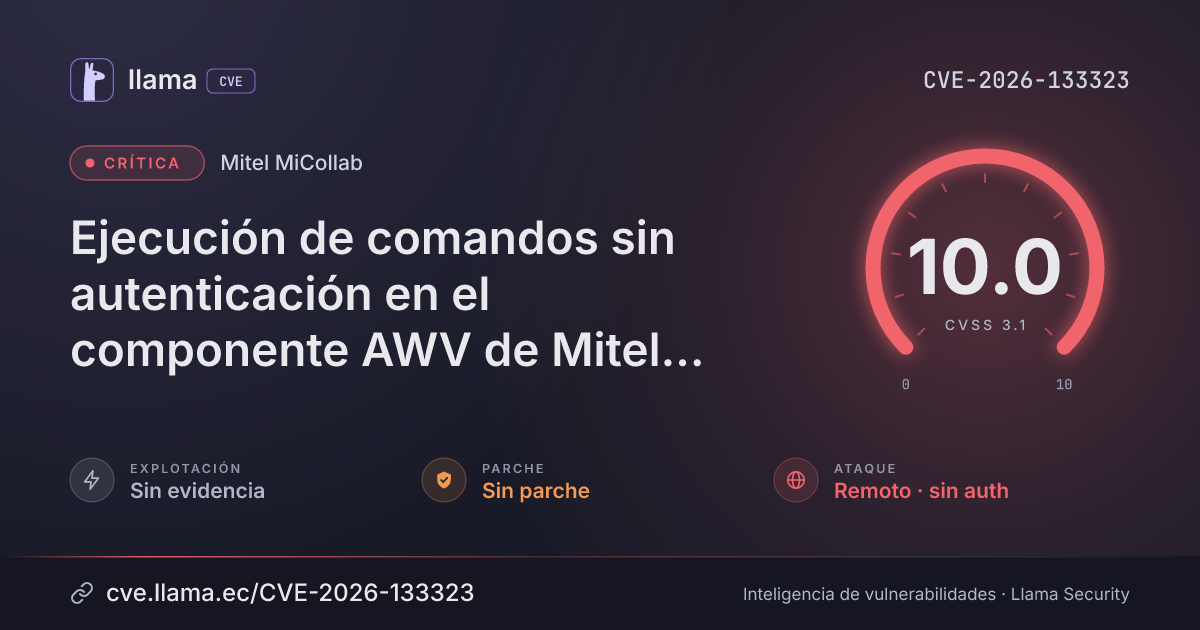
CVE-2026-133323

Mitel MiCollab unauthenticated command execution in AWV component

An unauthenticated attacker can run arbitrary commands on the system remotely over the network.

UnclearSin parche publicadoOS command injection
Descargar PNG JSON
CVSS 3.1
10.0
Crítica
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:H/A:H Fuente: CNA
ExplotaciónSin evidenciaSSVC: ninguna · no figura en CISA KEV
Exploits públicos0Ninguno conocido
ParcheSin parcheEl fabricante no ha publicado corrección
Exposición1 dDesde la divulgación, 19 nov 2026, 11:27 a. m.
Detección8 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir
Remediar en la ventana regular de mantenimiento
Sin explotación conocida, automatizable e impacto técnico parcial. No hay versión corregida: aplique mitigaciones.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada
Fuente: NIST NVD +1
11:27 a. m.
12:21 p. m.
02:47 a. m.
11:27 a. m.
09:17 p. m.
07:07 a. m.
04:57 p. m.
02:47 a. m.
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-133323 divulgada · CVSS 10 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 19 nov 2026

A vulnerability in the Audio, Web, and Video Conferencing (AWV) component of Mitel MiCollab could let an unauthenticated attacker run arbitrary commands on the system through a blind command injection caused by insufficient parameter sanitization. It can be reached remotely over the network, without logging in.

Affects Mitel MiCollab 10.3 (10.3.0.18) and earlier when the AWV component is involved. No fixed version or patch ID is named in the checked facts.

¿Qué significa?An unauthenticated attacker could execute arbitrary commands within the context of the system, with impact to integrity and availability.
¿Quién está afectado?Mitel MiCollab version 10.3 (10.3.0.18) and earlier, where the Audio, Web, and Video Conferencing (AWV) component is involved. A reader can compare the installed MiCollab version against 10.3 (10.3.0.18) to see whether it falls in this range.
¿Qué hacer?The advisory says to upgrade to the release it names and apply the provided patch, or to upgrade to a later release. The specific release and patch identifiers are not given in the checked facts.
no-patchThe workaround is to restrict external access to the AWV component.
Descripción original del registro (mitre)

A vulnerability in the Audio, Web, and Video Conferencing (AWV) component of Mitel MiCollab through 10.3 (10.3.0.18) could allow an unauthenticated attacker to conduct a blind command injection attack due to insufficient parameter sanitization. A successful exploit could allow an attacker to execute arbitrary commands within the context of the system. This is MTLVULN-1864.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Mitel MiCollab version 10.3 (10.3.0.18) and earlier.“10.3 (10.3.0.18) and earlier”
02
The Audio, Web, and Video Conferencing (AWV) component of MiCollab is involved.“Audio, Web, and Video Conferencing (AWV) component of MiCollab”
¿Quién debe revisar?Teams running Mitel MiCollab 10.3 (10.3.0.18) and earlier, including the AWV conferencing component.
MitigaciónRestrict external access to the AWV component.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:C
CambiadoSin cambio
ConfidencialidadC:N
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:H
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 10.0 (muy fácil) · sin evidencia de explotación.
Versiones

Rangos afectados

Afectada Corregida
MiCollab≤ 10.3 (10.3.0.18)
10.3 (10.3.0.18)
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
MiCollab
Sin parche — — —
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALmitre
Referencias
Fabricantehttps://www.mitel.com/support/security-advisories/mitel-product-security-advisory-misa-2026-0012

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.