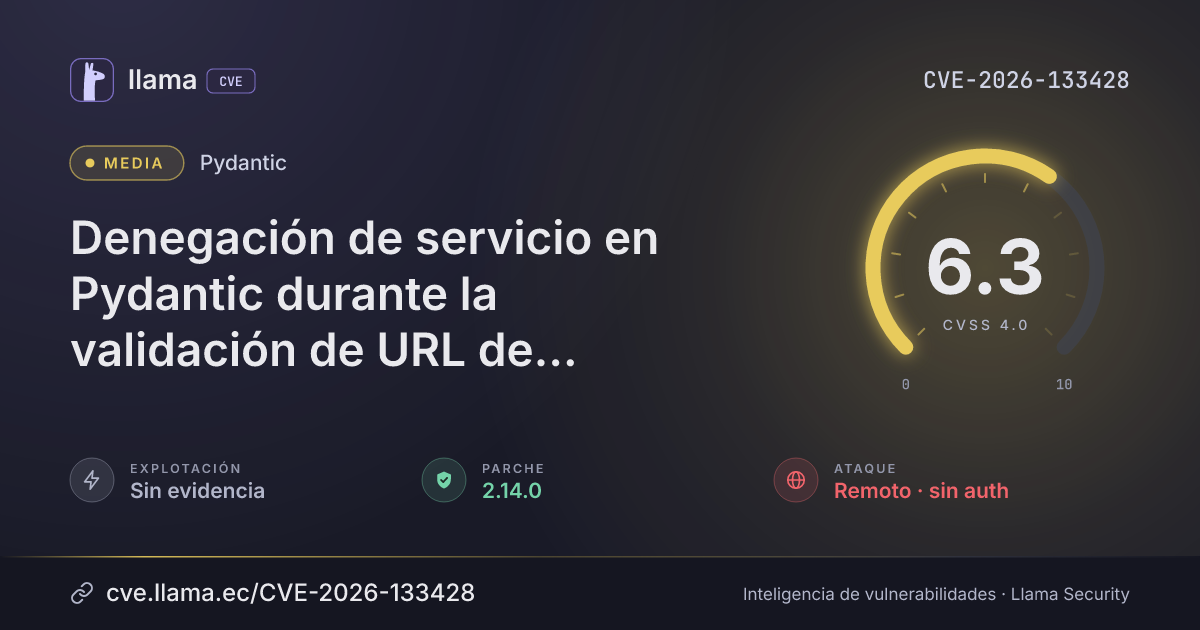
CVE-2026-133428
Pydantic denial of service in multi-host URL validation
A remote attacker can send a crafted URL without logging in to consume gigabytes of memory and stall the service.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:N/VI:N/VA:L/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 2.14.0 | pydantic · -43 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-133428 divulgada · CVSS 6.3 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Pydantic is affected by a bug where validating an untrusted URL with a long scheme and many hosts into a multi-host URL field, such as PostgresDsn, takes quadratic time and memory. A remote attacker who can send such input without logging in can use it to cause denial of service, since a roughly 100-kilobyte string can consume around a gigabyte of memory during validation.
Descripción original del registro (Pydantic)
Validating an untrusted URL with a long scheme and many hosts into a multi-host URL field (e.g. PostgresDsn) takes quadratic time and memory: an input of about a hundred kilobytes takes around a gigabyte of memory to validate. The parse_multihost_url() function (in pydantic-core/src/validators/url.rs) parses each host separately, prepending the whole URL prefix (including the scheme) to every one of them. As the scheme can be arbitrarily long, and is parsed and stored once per host, both time and memory grow quadratically with the input size. Allowed schemes (e.g. postgres for PostgresDsn) are only checked after parsing, so they don't prevent the issue. The issue was fixed in commit b4028f9d87e34750e53be0ba011d70f3c0fcc94e. Impact: denial of service through validation of untrusted input. Affected are applications validating untrusted strings into multi-host URL fields (PostgresDsn, MongoDsn, NatsDsn, or custom types built on MultiHostUrl).
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypipydantic |
Corregida | 2.14.0 | -43 d | 2.14.4 no afectada |
2.14.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/pydantic/pydantic/security/advisories/GHSA-955g-x97g-8mcphttps://github.com/pydantic/pydantic/blob/v2.13.5/pydantic-core/src/validators/url.rs#L537https://github.com/pydantic/pydantic/blob/v2.13.5/pydantic-core/src/validators/url.rs#L644-L649https://github.com/pydantic/pydantic/commit/b4028f9d87e34750e53be0ba011d70f3c0fcc94eLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.