llamaCVEVulnerability Intelligence
/
Fastify Express

CVE-2026-133867

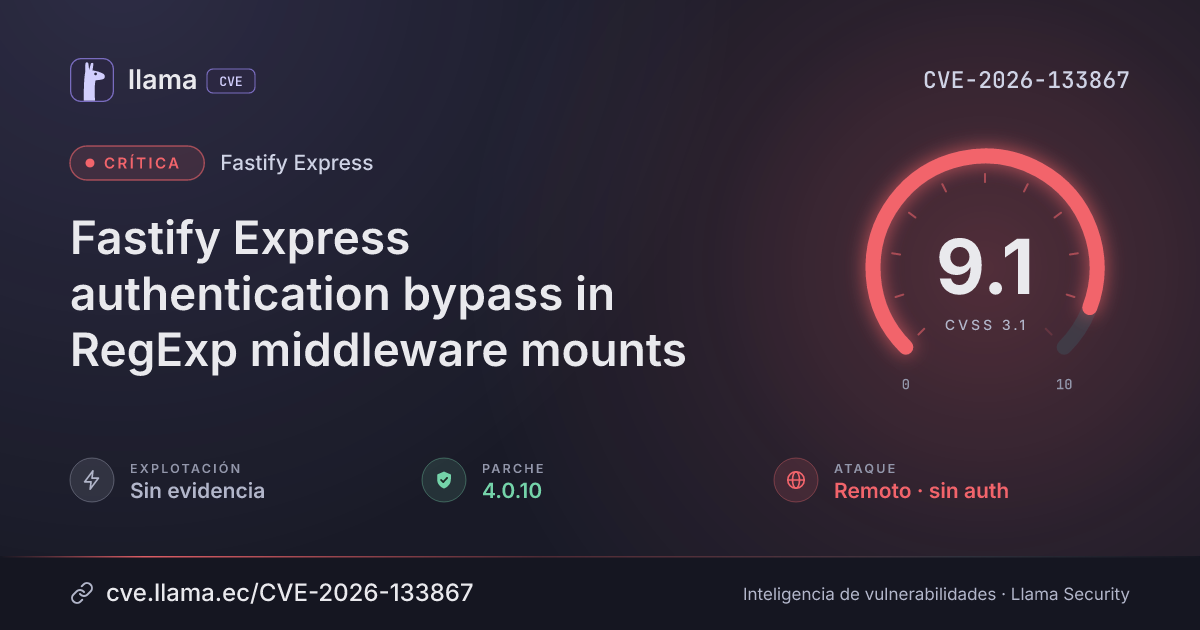
Fastify Express authentication bypass in RegExp middleware mounts

An unauthenticated attacker over the network can reach protected routes without logging in.

Afecta la configuración por defectoSin parche publicadoauthentication bypass
Descargar PNG JSON
CVSS 3.1
9.1
Crítica
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N Fuente: CNA
ExplotaciónSin evidenciaNo figura en CISA KEV
Exploits públicos0Ninguno conocido
ParcheSin parcheEl fabricante no ha publicado corrección
Exposición12 minDesde la divulgación, 21 nov 2026, 11:59 a. m.
Detección8 minDesde la divulgación hasta su ingreso al índice
Decisión estimadaAtender
Priorizar en el próximo ciclo de cambios
Estimación de Llama con el árbol SSVC de CISA a partir de vector CVSS 3.1 y la evidencia de explotación (sin evaluación oficial): sin explotación conocida, automatizable e impacto técnico total. No hay versión corregida: aplique mitigaciones.
Yo que tú, revisaba los logs de anoche.Mi radar llamuno marca riesgo alto. Confía.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Explotación
Remediación
Monitoreo
Detectada +1
11:59 a. m.
12:07 p. m.
11:59 a. m.
12:02 p. m.
12:05 p. m.
12:08 p. m.
12:11 p. m.
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-133867 divulgada · CVSS 9.1 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 21 nov 2026

Affected software: @fastify/express, the compatibility layer that runs Express middleware inside Fastify. When middleware is mounted with a regular expression inside a plugin registered under a parameterized prefix, Express skips that middleware while Fastify still runs the route handler, so an unauthenticated attacker can reach protected routes remotely over the network without logging in.

Only affects @fastify/express 4.0.7 through 4.0.9 with plugins registered under parameterized prefixes that mount RegExp-path middleware. Fixed in 4.0.10.

¿Qué significa?When a plugin is registered under a parameterized prefix such as /tenant/:tenantId, middleware mounted with a RegExp path inside that plugin can be skipped. Authentication or authorization middleware meant to guard protected routes may then not run, so unauthenticated clients can reach those routes.
¿Quién está afectado?Versions 4.0.7 through 4.0.9 of @fastify/express (range >= 4.0.7, < 4.0.10) are affected, in setups that register a plugin under a parameterized prefix and mount a RegExp-path middleware inside it. Check the installed @fastify/express version in your lockfile or with npm ls @fastify/express, and review plugin registrations for parameterized prefixes combined with RegExp middleware paths.
¿Qué hacer?Upgrade @fastify/express to 4.0.10, the fixed version.
Descripción original del registro (openjs)

@fastify/express is a compatibility layer that lets Express middleware run inside the Fastify web framework. In versions 4.0.7 through 4.0.9, the plugin does not rewrite regular-expression mount paths to account for a parameterized plugin prefix, so when middleware is mounted with a regular expression inside a plugin registered under a parameterized prefix, the Express matcher treats the prefix parameter as literal text and never matches the real request path. As a result, Express silently skips that middleware while Fastify still runs the route handler, so an application that relies on regular-expression mounted middleware for authentication or authorization inside a parameterized-prefix plugin exposes protected routes to unauthenticated clients. No special configuration is required beyond a parameterized prefix and a regular-expression mount. The issue is fixed in @fastify/express 4.0.10, and users should upgrade to 4.0.10 or later.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
@fastify/express versions 4.0.7 through 4.0.9 (affected range >= 4.0.7, < 4.0.10)“>= 4.0.7, < 4.0.10”
02
Plugin registered under a parameterized prefix, such as /tenant/:tenantId“When a plugin is registered under a parameterized prefix”
03
Middleware mounted with a RegExp path inside that plugin“middleware is mounted with a RegExp”
¿Quién debe revisar?Teams running @fastify/express 4.0.7 to 4.0.9 that register plugins under parameterized prefixes such as /tenant/:tenantId and mount auth middleware with RegExp paths.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 10.0 (muy fácil) · sin evidencia de explotación.
Versiones

Rangos afectados

Afectada Corregida Última
@fastify/express≥ 4.0.7 < 4.0.10
4.0.7
4.0.9
4.0.10
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
npm@fastify/express
Sin parche — — 4.0.9 afectada
Versiones corregidas4.0.10
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALopenjs
Referencias
Fabricantehttps://github.com/fastify/fastify-express/security/advisories/GHSA-84w6-xrf3-f8q8
Otrahttps://cna.openjsf.org/security-advisories.html

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.