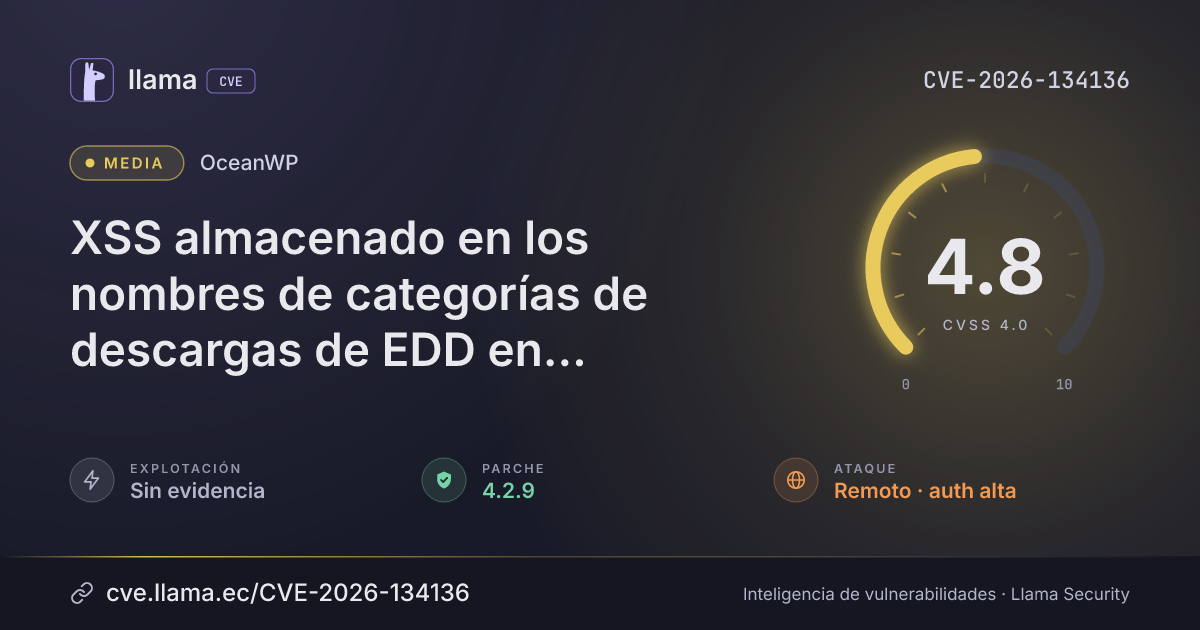
CVE-2026-134136
OceanWP stored XSS in EDD download category names
An attacker with download category rights can run scripts in visitors' browsers and may hijack admin sessions.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:N/VA:N/SC:L/SI:L/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-134136 divulgada · CVSS 4.8 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
The OceanWP WordPress theme has a stored cross-site scripting flaw in how it handles EDD download category names. A remote attacker who is logged in with permission to create download categories can plant a script in a category name that runs in the browsers of visitors who click the category link on the public archive page, and it could take over an administrator's session if one views that page while logged in.
Descripción original del registro (VulnCheck)
OceanWP WordPress Theme before 4.2.9 contains a stored cross-site scripting vulnerability in the oceanwp_edd_terms_list() function in inc/edd/edd-helpers.php, which allows authenticated users with EDD download category creation permissions to inject malicious JavaScript by crafting a category name that breaks out of an unescaped HTML title attribute. Attackers can create a category name containing an event-handler payload that executes in the browser of visitors who interact with the category link on the public EDD archive page, potentially compromising an administrator's session if they view the affected page while authenticated.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
oceanwp |
Corregida | 4.2.9 | — | — |
4.2.9Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/oceanwp/oceanwp/releases/tag/4.2.9https://github.com/oceanwp/oceanwp/pull/577https://www.vulncheck.com/advisories/oceanwp-before-stored-xss-via-edd-category-nameLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.