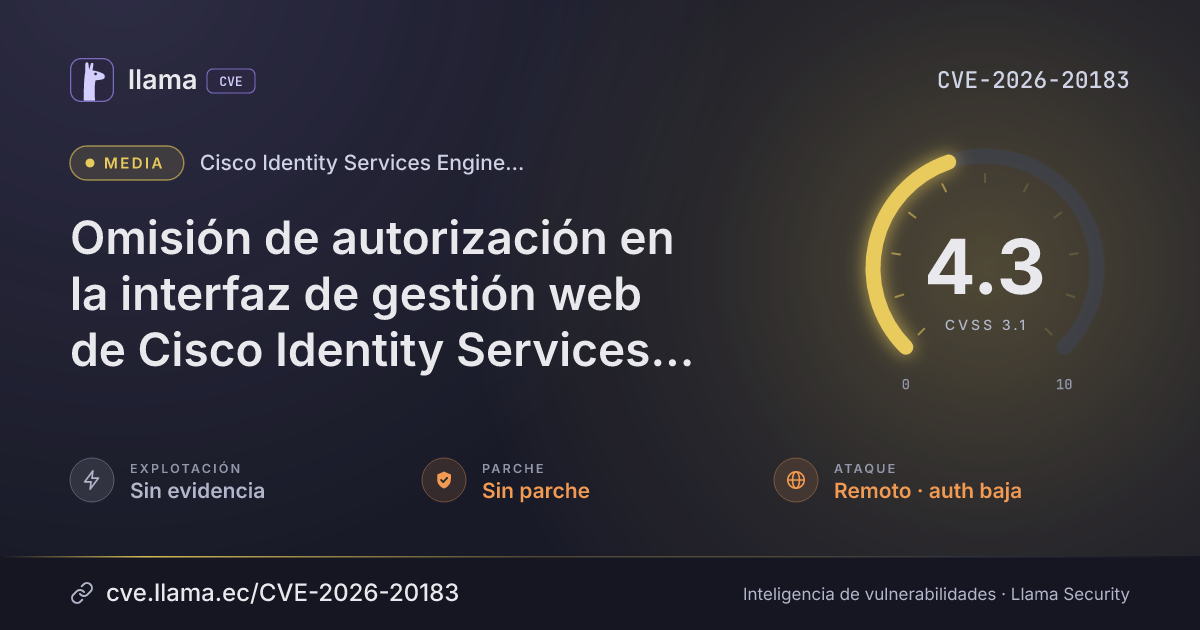
CVE-2026-20183
Cisco Identity Services Engine Software authorization bypass in web management interface
A remote attacker with valid admin credentials can alter file descriptions via a crafted HTTP request.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-20183 divulgada · CVSS 4.3 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Cisco Identity Services Engine (ISE) contains an authorization bypass flaw in its web-based management interface that lets a remote attacker who already holds valid administrator credentials modify descriptions of files on a specific page by sending a crafted HTTP request. Exploitation requires that low-privilege login, and the flaw is not known to be used in attacks.
Descripción original del registro (cisco)
A vulnerability in the web-based management interface of Cisco Identity Services Engine (ISE) could allow an authenticated, remote attacker to modify parts of the configuration on an affected device. This vulnerability is due to the lack of server-side validation of Administrator permissions. An attacker could exploit this vulnerability by submitting a crafted HTTP request to an affected system. A successful exploit could allow the attacker to modify descriptions of files on a specific page. To exploit this vulnerability, an attacker would need valid Administrator credentials.
Desglose de métricas
Versiones afectadas
3.1.03.1.0 p13.1.0 p33.1.0 p23.2.03.1.0 p43.1.0 p53.2.0 p13.1.0 p63.2.0 p23.1.0 p73.3.03.2.0 p33.2.0 p43.1.0 p83.2.0 p53.2.0 p63.1.0 p93.3 Patch 23.3 Patch 13.3 Patch 33.4.03.2.0 p73.3 Patch 43.4 Patch 13.1.0 p103.3 Patch 53.3 Patch 63.4 Patch 23.3 Patch 73.4 Patch 33.5.03.4 Patch 43.3 Patch 83.2 Patch 83.5 Patch 13.3 Patch 93.2 Patch 93.4 Patch 53.5 Patch 33.5 Patch 23.3 Patch 103.3 Patch 113.4 Patch 63.2 Patch 103.1.0 p113.1.0 p123.2 Patch 11Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Cisco Identity Services Engine Software |
Sin parche | — | — | — |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-auth-bypass-1-MxcTNgwxLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.