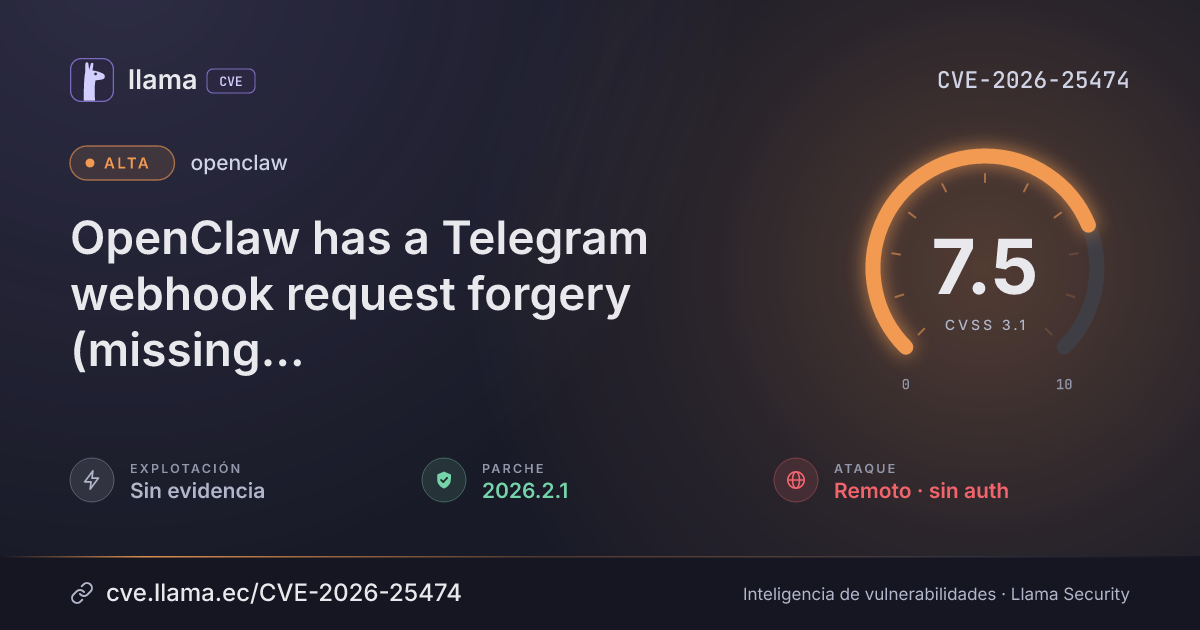
CVE-2026-25474
OpenClaw has a Telegram webhook request forgery (missing channels.telegram.webhookSecret) → auth bypass
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 2026.2.1 | openclaw · -17 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-25474 divulgada · CVSS 7.5 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
OpenClaw is a personal AI assistant. In versions 2026.1.30 and below, if channels.telegram.webhookSecret is not set when in Telegram webhook mode, OpenClaw may accept webhook HTTP requests without verifying Telegram’s secret token header. In deployments where the webhook endpoint is reachable by an attacker, this can allow forged Telegram updates (for example spoofing message.from.id). If an attacker can reach the webhook endpoint, they may be able to send forged updates that are processed as if they came from Telegram. Depending on enabled commands/tools and configuration, this could lead to unintended bot actions. Note: Telegram webhook mode is not enabled by default. It is enabled only when `channels.telegram.webhookUrl` is configured. This issue has been fixed in version 2026.2.1.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmopenclaw |
Corregida | 2026.2.1 | -17 d | 2026.11.3 no afectada |
2026.2.1Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/openclaw/openclaw/security/advisories/GHSA-mp5h-m6qj-6292https://github.com/openclaw/openclaw/commit/3cbcba10cf30c2ffb898f0d8c7dfb929f15f8930https://github.com/openclaw/openclaw/commit/5643a934799dc523ec2ef18c007e1aa2c386b670https://github.com/openclaw/openclaw/commit/633fe8b9c17f02fcc68ecdb5ec212a5ace932f09https://github.com/openclaw/openclaw/commit/ca92597e1f9593236ad86810b66633144b69314dhttps://github.com/openclaw/openclaw/releases/tag/v2026.2.1Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.