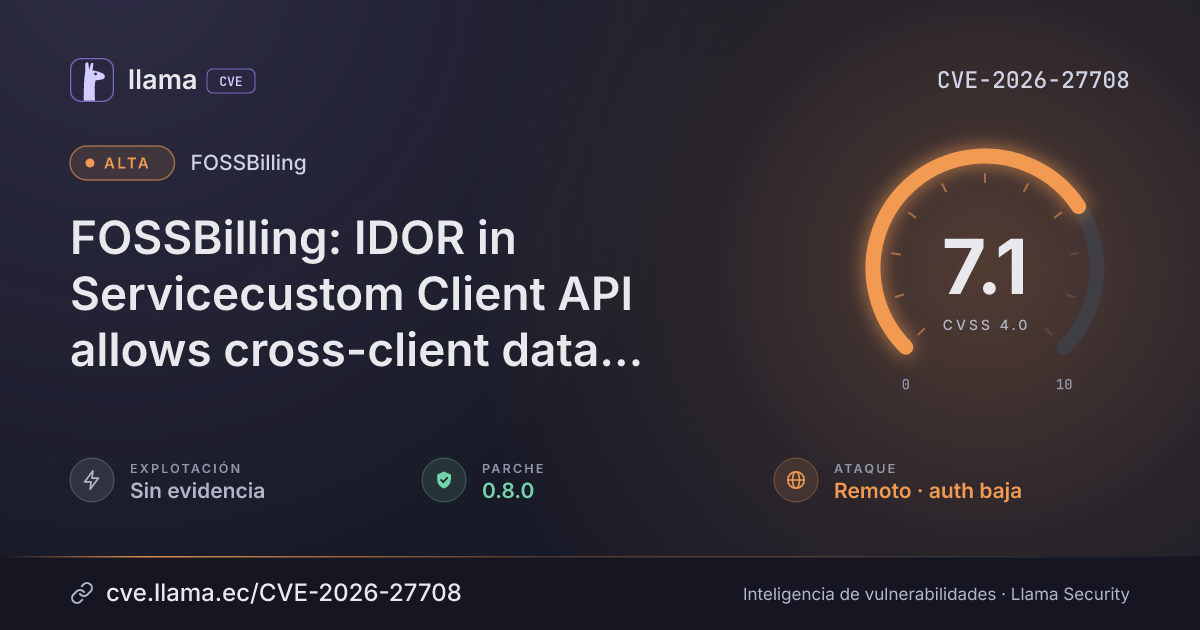
CVE-2026-27708
FOSSBilling: IDOR in Servicecustom Client API allows cross-client data access
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-27708 divulgada · CVSS 7.1 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
FOSSBilling is a free, open-source billing and client management system. In versions 0.7.2 and prior, the Servicecustom Client API's __call method accepts an order_id parameter and fetches the associated order without verifying the authenticated client owns it, potentially exposing cross-client data through IDOR. An authenticated client can access any other client's custom service by guessing sequential order IDs. This can lead to a confidentiality breach — attackers can read client PII (name, email, phone, address, company details, VAT number) and service configuration data belonging to other clients. This issue has been fixed in version 0.8.0.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
FOSSBilling |
Corregida | 0.8.0 | — | — |
0.8.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/FOSSBilling/FOSSBilling/security/advisories/GHSA-p36w-9x66-488jhttps://github.com/FOSSBilling/FOSSBilling/releases/tag/0.8.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.