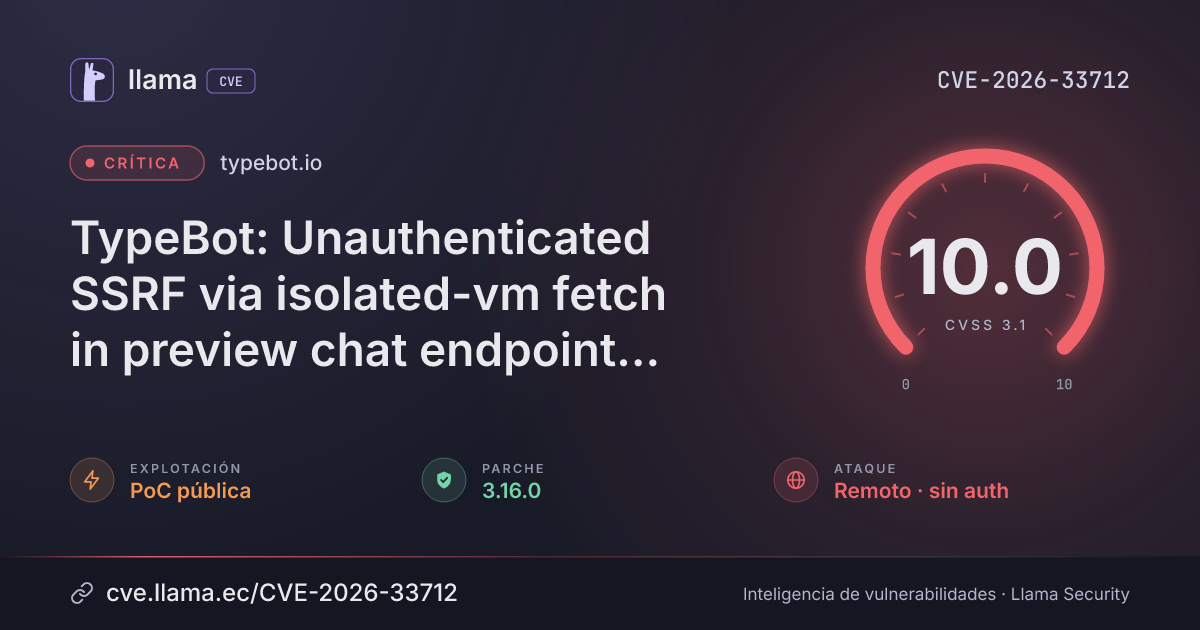
CVE-2026-33712
TypeBot: Unauthenticated SSRF via isolated-vm fetch in preview chat endpoint bypasses SSRF controls
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-33712 divulgada · CVSS 10 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación PoC pública | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Typebot is a chatbot builder tool. In versions 3.15.2 and prior, the preview chat endpoint (POST /api/v1/typebots/{typebotId}/preview/startChat) allows unauthenticated users to achieve Server-Side Request Forgery (SSRF) by supplying a custom typebot definition with server-side code blocks. The fetch function exposed inside the isolated-vm sandbox calls Node.js native fetch without the SSRF validation (validateHttpReqUrl) that protects the HTTP Request block. This bypasses all SSRF mitigations added after GHSA-8gq9-rw7v-3jpr. Exploitation of this unauthenticated SSRF vulnerability can lead to cloud credential theft, internal network access and data exfiltration for any self-hosted Typebot deployments and hosted services. This issue has been fixed in version 3.16.0.
Affects Typebot 3.15.2 and earlier when a custom typebot definition with server-side code blocks is sent to the preview chat endpoint. Fixed in 3.16.0.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
typebot.io |
Corregida | 3.16.0 | — | — |
3.16.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/baptisteArno/typebot.io/security/advisories/GHSA-vc2q-r6rq-ggj9https://github.com/baptisteArno/typebot.io/releases/tag/v3.16.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.