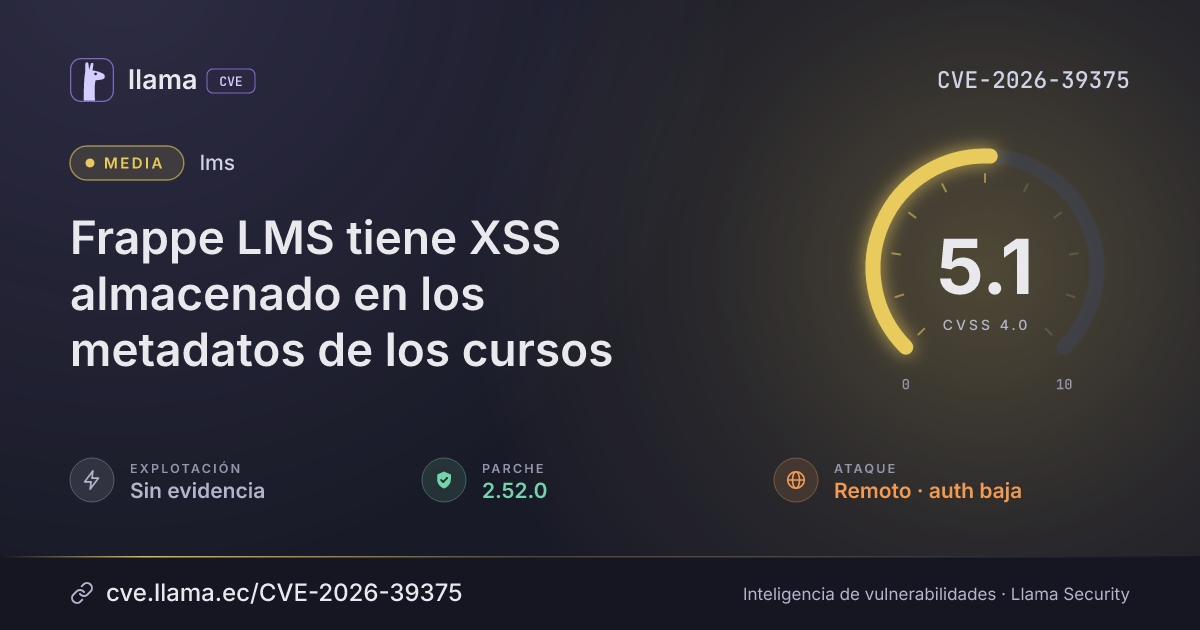
CVE-2026-39375
Frappe LMS has Stored XSS in Course Meta
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:L/VA:N/SC:L/SI:L/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-39375 divulgada · CVSS 5.1 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Frappe LMS, a learning management system used to structure course content, is affected by this vulnerability in its Course Management module. An authenticated user with a course editing role can inject malicious scripts through course meta tag fields, which execute when other users view the content.
Affects Frappe LMS versions before 2.52.0, where a user with a course editing role can store malicious JavaScript in course meta tag fields. Fixed in 2.52.0.
Descripción original del registro (GitHub_M)
Frappe Learning Management System (LMS) is a learning system that helps users structure their content. Prior to version 2.52.0, an authenticated user with a course editing role can inject malicious JavaScript through meta tag fields in the Course Management module. The values are stored without adequate HTML sanitization and are not safely escaped when rendered, allowing stored cross-site scripting. This issue is fixed in version 2.52.0.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
lms |
Corregida | 2.52.0 | — | — |
2.52.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/frappe/lms/security/advisories/GHSA-9fqj-95wr-6hm6https://github.com/frappe/lms/commit/cd6aca25f7d28425660720db4fdb920727edb670https://github.com/frappe/lms/commit/f244a6c9ff6e0b104fec48b2d97af4cc09896b60https://github.com/frappe/lms/tree/v2.52.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.