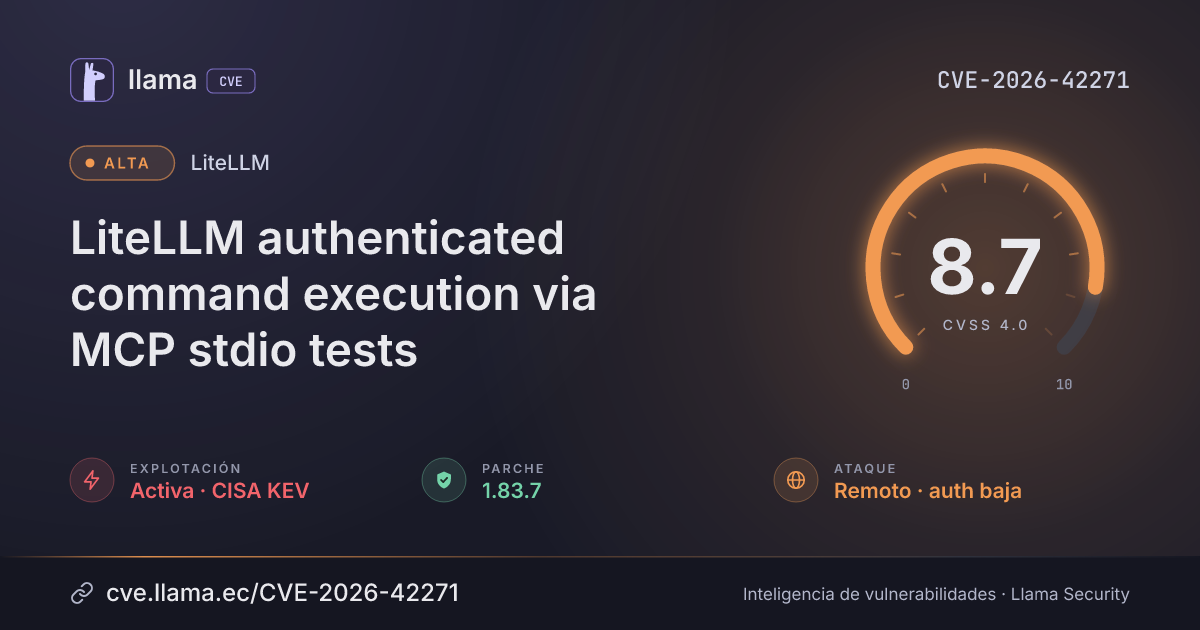
CVE-2026-42271
LiteLLM authenticated command execution via MCP stdio tests
Any user with a valid API key, even a low-privilege one, can run arbitrary commands on the host.
CVSS:4.0/AV:N/AC:L/AT:P/PR:L/UI:N/VC:H/VI:H/VA:H/SC:H/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 1.83.7 | litellm · -25 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-42271 divulgada · CVSS 8.7 (CNA) | |
| Explotación | CISA KEV | Agregada al catálogo de vulnerabilidades explotadas | |
| Remediación | Plazo KEV | Fecha límite de remediación para agencias federales (EE. UU.) | |
| Divulgación | Modificada | Última actualización del registro | |
| Explotación | Umbral EPSS | La probabilidad de explotación supera el 10 % | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
LiteLLM, the proxy server for calling LLM APIs, lets any user with a valid proxy API key, even a low-privilege one, run arbitrary commands on the host with the proxy's privileges. An attacker can do this remotely over the network by sending a stdio server configuration to the MCP test endpoints, and the bug is listed as exploited in attacks by CISA.
Affects the LiteLLM proxy (pip package litellm) 1.74.2 up to but not including 1.83.7, where any authenticated user could run commands on the host via the MCP test endpoints. Fixed in 1.83.7.
Descripción original del registro
LiteLLM is a proxy server (AI Gateway) to call LLM APIs in OpenAI (or native) format. From version 1.74.2 to before version 1.83.7, two endpoints used to preview an MCP server before saving it — POST /mcp-rest/test/connection and POST /mcp-rest/test/tools/list — accepted a full server configuration in the request body, including the command, args, and env fields used by the stdio transport. When called with a stdio configuration, the endpoints attempted to connect, which spawned the supplied command as a subprocess on the proxy host with the privileges of the proxy process. The endpoints were gated only by a valid proxy API key, with no role check. Any authenticated user — including holders of low-privilege internal-user keys — could therefore run arbitrary commands on the host. This issue has been patched in version 1.83.7.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypilitellm |
Corregida | 1.83.7 | -25 d | 1.109.1 no afectada |
1.83.7Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/BerriAI/litellm/security/advisories/GHSA-v4p8-mg3p-g94ghttps://github.com/BerriAI/litellm/releases/tag/v1.83.7-stableLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.