llamaCVEVulnerability Intelligence
/
argo-workflows

CVE-2026-42295

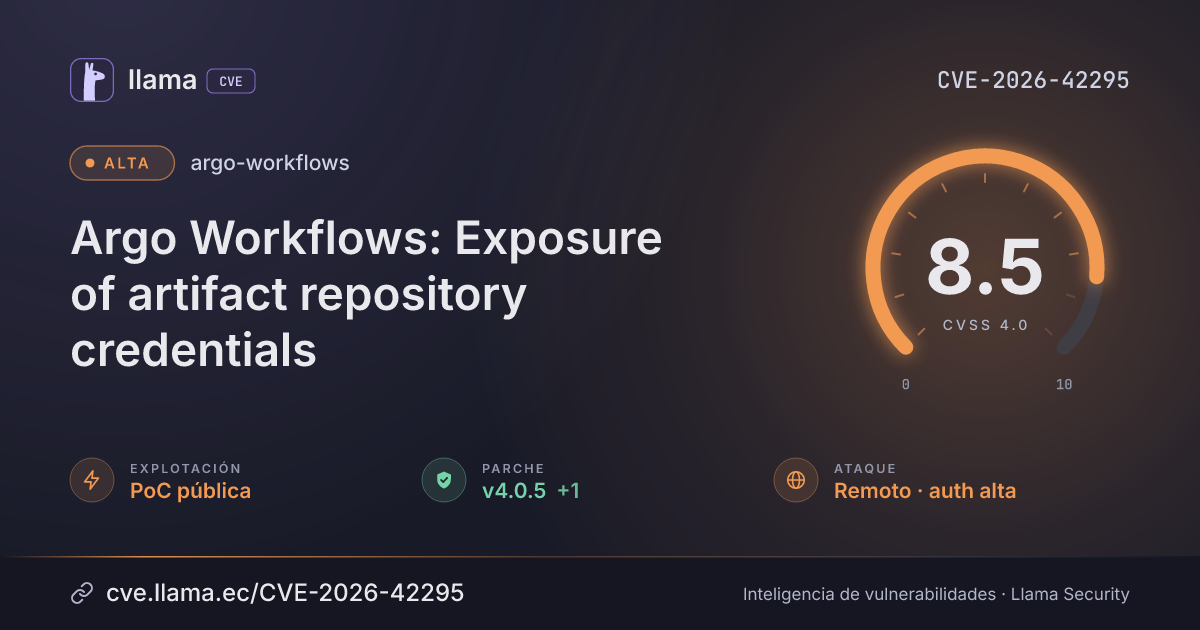
Argo Workflows: Exposure of artifact repository credentials

Specific setups onlySin parche publicado
Descargar PNG JSON
CVSS 4.0
8.5
Alta
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:N/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N Fuente: CNA
4.9NVD · CVSS 3.1CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:N/A:N
ExplotaciónPoC públicaSSVC: poc · no figura en CISA KEV
Exploits públicos0Ninguno conocido
ParcheSin parcheEl fabricante no ha publicado corrección
Exposición194 dDesde la divulgación, 8 may 2026, 10:48 p. m.
Detección178 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir de cerca
Monitorear y programar la remediación
Existe PoC pública, no automatizable e impacto técnico total. No hay versión corregida: aplique mitigaciones.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Parche v4.0.5
Monitoreo
Detectada
Verificada
23 abr 26
9 may 26
11 may 26
3 nov 26
18 nov 26
19 nov 26
23 abr 26
14 jun 26
6 ago 26
27 sept 26
19 nov 26
FechaFaseEventoDetalle
Remediación Parche v4.0.5 github.com/argoproj/argo-workflows/v4 · -16 d desde divulgación
Divulgación Publicada CVE-2026-42295 divulgada · CVSS 8.5 (CNA)
Divulgación Evaluación SSVC CISA-ADP · explotación PoC pública
Divulgación Modificada Última actualización del registro
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen

Argo Workflows is an open source container-native workflow engine for orchestrating parallel jobs on Kubernetes. From version 4.0.0 to before version 4.0.5, the workflow executor logs all artifact repository credentials (S3 access keys, secret keys, GCS service account keys, Azure account keys, Git passwords, etc.) in plaintext on artifact operation. Any user with read access to workflow pod logs can extract these credentials. This issue has been patched in version 4.0.5.

Affects Argo Workflows 4.0.0 up to but not including 4.0.5, when S3, OSS or GCS artifact repository credentials are configured. Fixed in 4.0.5.

¿Qué significa?Artifact operations in the workflow executor can write artifact repository credentials, such as S3 access keys, secret keys, and GCS service account keys, in plaintext into workflow pod logs. Anyone with read access to those logs can extract the credentials.
¿Quién está afectado?Versions from 4.0.0 up to but not including 4.0.5 are affected, and the issue applies when S3, OSS or GCS artifact repository credentials are configured. To check, look at the installed Argo Workflows version and whether an artifact repository with those credential types is set up.
¿Qué hacer?Upgrade to Argo Workflows 4.0.5, the fixed version, using the release install manifest at https://github.com/argoproj/argo-workflows/releases/download/v4.0.5/install.yaml.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Argo Workflows versions from 4.0.0 up to but not including 4.0.5“>=4.0.0, < 4.0.5”
02
Artifact operation in the workflow executor with S3, OSS or GCS artifact repository credentials configured“in plaintext on artifact operation”
¿Quién debe revisar?Teams running Argo Workflows 4.0.x before 4.0.5 on Kubernetes, including Go projects importing github.com/argoproj/argo-workflows, that use S3, OSS or GCS artifact repositories
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · NVD
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:H
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:N
AltoBajoNinguno
DisponibilidadA:N
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida Última
github.com/argoproj/argo-workflows · github.com/argoproj/argo-workflows/v2 · github.com/argoproj/argo-workflows/v3todas
argo-workflows · github.com/argoproj/argo-workflows/v4≥ 4.0.0 < 4.0.5
v2.5.2+incompatible
v3.7.18
4.0.0
4.0.5
v4.1.6
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
gogithub.com/argoproj/argo-workflows
Sin parche — — v2.5.2+incompatible afectada
gogithub.com/argoproj/argo-workflows/v3
Sin parche — — v3.7.18 afectada
gogithub.com/argoproj/argo-workflows/v4
Corregida v4.0.5 -16 d v4.1.6 no afectada
Versiones corregidas4.0.5v4.0.5
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/argoproj/argo-workflows/security/advisories/GHSA-7vf8-2cr6-54mf
Otrahttps://github.com/argoproj/argo-workflows/releases/tag/v4.0.5

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.