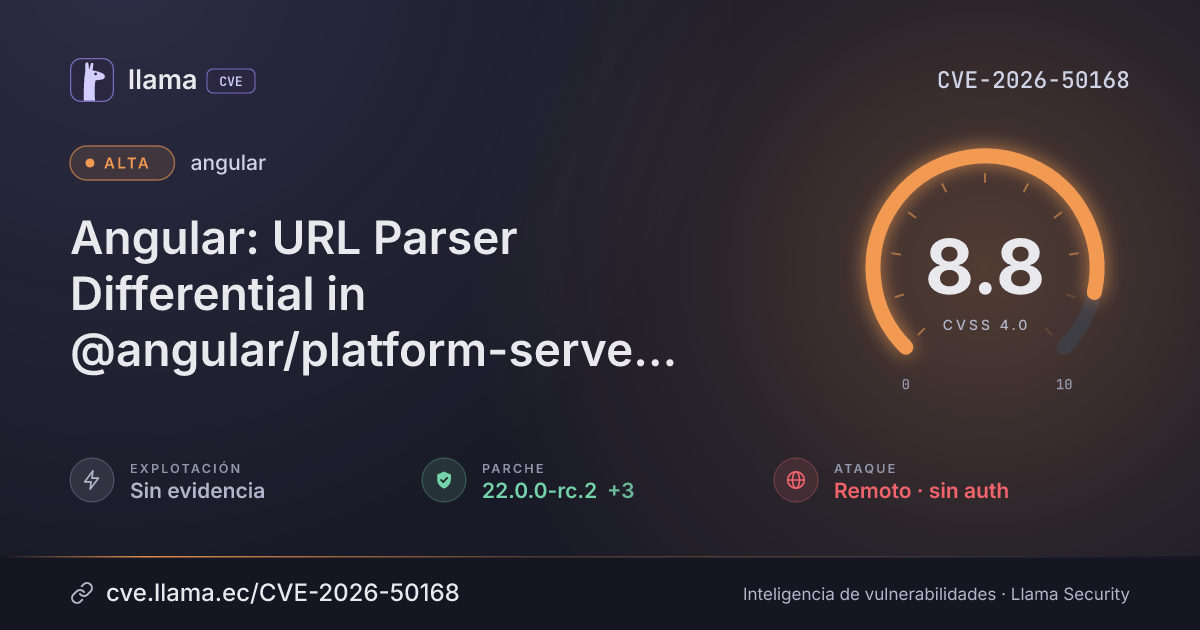
CVE-2026-50168
Angular: URL Parser Differential in @angular/platform-server leading to SSRF Allowlist Bypass
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:L/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 19.2.23 | @angular/platform-server · -26 d desde divulgación | |
| Remediación | Parche 20.3.22 | @angular/platform-server · -26 d desde divulgación | |
| Remediación | Parche 21.2.15 | @angular/platform-server · -25 d desde divulgación | |
| Remediación | Parche 22.0.0-rc.2 | @angular/platform-server · -25 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-50168 divulgada · CVSS 8.8 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Angular is a development platform for building mobile and desktop web applications using TypeScript/JavaScript and other languages. Prior to 22.0.0-rc.2, 21.2.15, 20.3.22, and 19.2.23, an issue in the @angular/platform-server package allows remote attackers to bypass host allowlist constraints and direct server-side outgoing requests to arbitrary external endpoints. This occurs due to a parser differential between the strict WHATWG URL parser used for allowlist validation and the lenient Domino URL parser used to initialize the server emulated DOM. When a server-side request contains a malformed URL with a double port structure (e.g., http://evil.com:80:80/path), Node's strict URL.canParse(url) logic returns false and skips host check validation entirely. However, the same malformed URL is later accepted and parsed leniently by Domino's internal parser, which resolves the origin to http://evil.com:80. The Angular SSR HTTP request interceptor (relativeUrlsTransformerInterceptorFn) then resolves all relative backend HTTP requests against this adopted origin, executing the SSRF attack. This vulnerability is fixed in 22.0.0-rc.2, 21.2.15, 20.3.22, and 19.2.23.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npm@angular/platform-server |
Corregida | 19.2.23, 20.3.22, 21.2.15, 22.0.0-rc.2 | -26 d · -26 d · -25 d · -25 d | 22.2.6 no afectada |
19.2.2320.3.2221.2.1522.0.0-rc.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/angular/angular/security/advisories/GHSA-xrxm-cp7j-8xf6https://github.com/angular/angular/pull/68928Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.