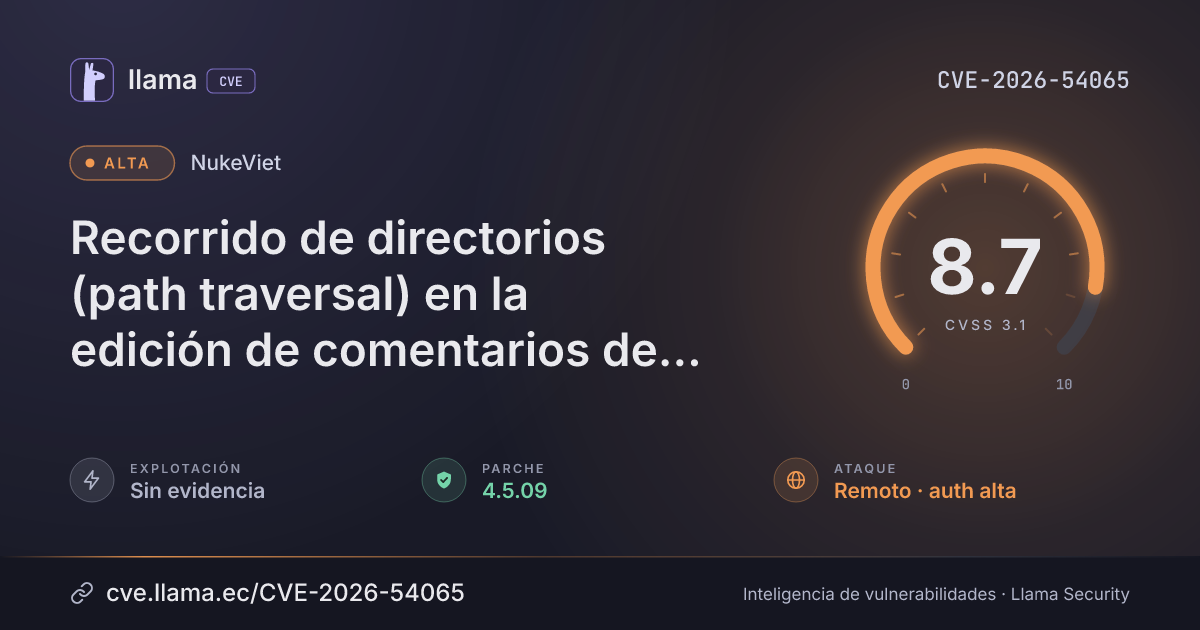
CVE-2026-54065
NukeViet path traversal in comment editing allows file deletion
An attacker with admin login can delete files outside the upload folder, such as config.php, causing an outage.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:C/C:N/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-54065 divulgada · CVSS 8.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
NukeViet CMS is affected through its comment editing and deletion features. A remote attacker who already holds administrator-level login can delete application files outside the upload folder, such as config.php, which causes an outage.
NukeViet CMS releases before 4.5.09 are affected, and 4.5.09 is the fixed version. CVSS scores it 8.7 (High), and no vendor severity is given.
Descripción original del registro (GitHub_M)
NukeViet CMS is a multi Content Management System. Prior to 4.5.09, an authenticated administrator can submit a crafted attach value to modules/comment/admin/edit.php. The handler removed a fixed-length upload prefix without validating containment, allowing padding followed by a traversal path to be stored in the database. When the comment is deleted, modules/comment/admin/del.php joins the stored path to NV_UPLOADS_REAL_DIR and passes it to nv_deletefile(), whose realpath() check restricts deletion only to NV_ROOTDIR rather than the upload directory, permitting deletion of application files such as config.php and causing an outage. This issue is fixed in version 4.5.09.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
nukeviet |
Corregida | 4.5.09 | — | — |
4.5.09Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/nukeviet/nukeviet/security/advisories/GHSA-c9xg-64p9-f2jjhttps://github.com/nukeviet/nukeviet/commit/27ba63c32eea2782837b1464a930baf75f0b4d29https://github.com/nukeviet/nukeviet/releases/tag/4.5.09Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.