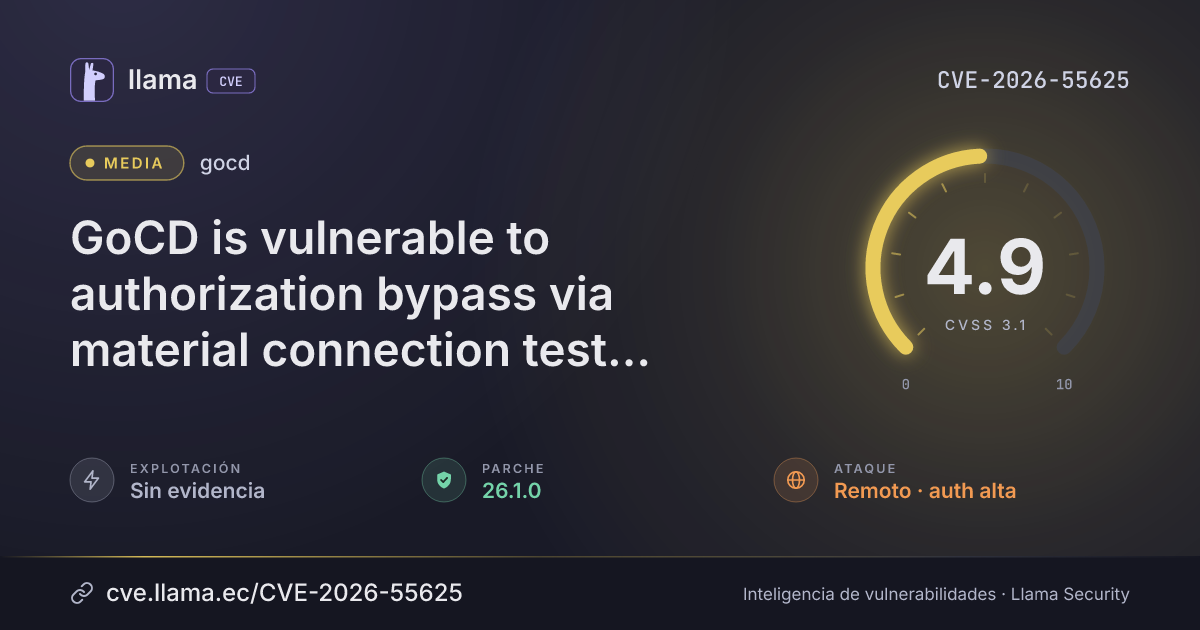
CVE-2026-55625
GoCD is vulnerable to authorization bypass via material connection test APIs
CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:N/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-55625 divulgada · CVSS 4.9 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV |
GoCD is a continuous deliver server. From 16.1.0 until 26.1.0, the internal material connection test APIs at /go/api/admin/internal/material_test and /go/api/internal/config_repos/*/material_test accept an arbitrary existing pipeline and pipeline-group context without sufficient validation. A pipeline group administrator can invoke Test Connection for source control materials outside the administrator's authorized pipeline group or configuration repository and potentially use credentials from those materials. For GoCD 20.6.0 and later, the test context can also resolve external secrets managed by secret-management plugins, including global reusable secrets with separate permissions. This issue is fixed in version 26.1.0.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gocd |
Corregida | 26.1.0 | — | — |
26.1.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/gocd/gocd/security/advisories/GHSA-4557-94j8-5p66https://www.gocd.org/releases/#26-1-0https://github.com/gocd/gocd/commit/f0dda0fb8af4cff5e2f4bf52b753fb41a7ec8918https://github.com/gocd/gocd/releases/tag/26.1.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.